
Exposure Management: How It Reduces Cyber Risk
Exposure management is a continuous cybersecurity approach that helps organizations identify, understand, prioritize, and reduce the weaknesses attackers are most likely to exploit. Instead of focusing only on software vulnerabilities, it considers a much wider range of exposures, including cloud misconfigurations, weak identities, internet-facing assets, excessive permissions, unprotected services, outdated systems, and risky attack paths. The goal is to determine which weaknesses create meaningful business risk rather than treating every technical finding as equally urgent. Modern organizations may have thousands or millions of potential security findings across cloud, endpoints, applications, networks, and third-party services. Exposure management brings those findings into a more risk-based process. It helps security teams spend limited time and resources on weaknesses that could genuinely lead to compromise.
The approach has become increasingly important as IT environments grow more distributed and difficult to understand. Organizations now operate SaaS applications, cloud infrastructure, remote endpoints, APIs, containers, identities, operational technology, and internet-facing services at the same time. Traditional vulnerability scanning remains important, but a vulnerability list alone cannot explain whether an attacker can actually reach a sensitive system through a realistic path. Exposure management adds context such as exploitability, asset importance, internet accessibility, user privileges, threat activity, and security controls. This allows teams to prioritize remediation according to likely attack outcomes. This guide explains exposure management, how it works, how it differs from vulnerability management, and how organizations can use it to reduce cyber risk continuously.
What Is Exposure Management?
Exposure management is the ongoing process of discovering security weaknesses across an organization’s technology environment and determining which ones create the greatest risk. An exposure can be a software vulnerability, but the term is broader than traditional vulnerability management. It may include a publicly accessible cloud database, an employee account with excessive privileges, an abandoned internet-facing server, a weak authentication configuration, or an application containing a dangerous access-control flaw. Exposure management connects these weaknesses with the assets and business processes they could affect. The objective is to understand where attackers have realistic opportunities rather than simply count how many security issues exist. This risk-oriented perspective helps organizations make more effective remediation decisions.
A useful way to understand exposure management is to imagine the organization from an attacker’s point of view. An attacker does not necessarily care which system has the highest vulnerability score if that system is isolated and contains no valuable information. Instead, the attacker looks for a route that begins with something accessible and eventually reaches sensitive systems or privileged accounts. That route could involve a forgotten web server, reused credentials, an overly permissive cloud role, and an internal application weakness. Exposure management tries to identify these connected conditions before an attacker does. It therefore focuses heavily on relationships between weaknesses rather than examining each finding in isolation.
The concept also recognizes that cyber risk changes continuously. A server considered low risk today may become more important tomorrow because a new application begins using it. A vulnerability that has existed quietly for months can become urgent when public exploit code appears or attackers begin targeting it actively. Cloud resources can become exposed through configuration changes, while employees may receive new permissions as their roles change. Exposure management therefore cannot operate as a once-a-year assessment. It requires continuous discovery, monitoring, prioritization, remediation, and validation as the environment and threat landscape evolve.
Business context is another defining element of exposure management. Security teams need to know which assets support critical services, contain sensitive data, or provide administrative access to other systems. A vulnerability affecting a customer payment platform usually deserves different treatment from the same vulnerability on a temporary development server with no meaningful connectivity. Asset ownership also matters because findings cannot be corrected efficiently if nobody knows which team is responsible. Exposure management platforms therefore often enrich technical findings with business information, identity relationships, asset value, and dependency data. This helps turn raw security telemetry into decisions that business and technology teams can act on.
Exposure management is sometimes discussed alongside continuous threat exposure management, commonly abbreviated CTEM. The underlying idea is that security teams should repeatedly scope important areas, discover exposures, prioritize them, validate whether attack paths are realistic, and mobilize remediation. The emphasis is on reducing exploitable conditions rather than producing larger lists of findings. Organizations do not need to eliminate every possible weakness before benefiting from the approach. They need a repeatable way to identify which exposures matter most and reduce them faster than attackers can take advantage. This makes exposure management an operational cybersecurity discipline rather than simply another scanning technology.
How Does Exposure Management Work?
The exposure management process usually begins with asset discovery because organizations cannot manage risks associated with systems they do not know exist. Security teams identify endpoints, servers, applications, cloud resources, identities, network devices, SaaS platforms, containers, APIs, and other technology assets. Discovery should include both internally managed systems and externally visible infrastructure because attackers frequently target forgotten internet-facing assets. Information may come from vulnerability scanners, cloud APIs, identity platforms, configuration databases, endpoint tools, and attack surface management systems. The objective is to create a current picture of the environment. Incomplete asset visibility can leave serious weaknesses outside normal security processes.
After assets are discovered, security tools identify exposures associated with them. Vulnerability scanners find known software flaws, while cloud security tools detect risky configurations and identity platforms reveal excessive permissions or weak authentication. Application security testing may identify code-level problems, and external attack surface management can detect exposed services, domains, certificates, and shadow IT. Each technology produces a different type of finding. Exposure management brings these sources together so teams can understand how multiple weaknesses interact. A single misconfiguration may appear minor until it is combined with an exposed service and an overly privileged identity.
Prioritization follows discovery because organizations rarely have enough staff to fix every issue immediately. Exposure management evaluates technical severity together with real-world context such as exploit availability, active threat activity, internet exposure, asset criticality, data sensitivity, existing security controls, and attack path relationships. A medium-severity flaw on an internet-facing identity server may create more practical risk than a critical vulnerability buried inside an isolated laboratory network. Risk-based prioritization therefore challenges the assumption that severity scores alone determine remediation order. It aims to answer a more useful question: which exposure is most likely to help an attacker cause meaningful damage?
Validation helps determine whether prioritized attack paths and weaknesses are truly exploitable in the organization’s specific environment. Security teams may use penetration testing, breach and attack simulation, attack path analysis, or controlled validation tools to confirm whether an attacker could move from one system to another. The purpose is not to exploit production systems recklessly. Instead, validation provides evidence that a suspected exposure represents a realistic attack opportunity. Findings that cannot be exploited under current conditions may receive a different remediation priority. This evidence-based approach helps reduce wasted effort while increasing confidence in high-priority security decisions.
Remediation and continuous monitoring complete the cycle. Security teams assign issues to responsible infrastructure, application, identity, or cloud teams and track corrective action. Fixes may involve patching software, removing public access, changing permissions, disabling unused accounts, segmenting networks, or updating application code. After remediation, the environment should be rescanned or revalidated to confirm that the exposure actually disappeared. New exposures are then discovered as systems change, starting the cycle again. Exposure management therefore functions as a continuous feedback loop rather than a project with a fixed completion date.
Key Components of an Exposure Management Program
Attack surface management is a major component because organizations need visibility into systems that attackers can discover from outside. Public cloud services, forgotten subdomains, abandoned web applications, remote access portals, APIs, and development environments can all become entry points. External attack surface management tools continuously search for assets associated with the organization and identify unexpected exposure. This is particularly valuable after mergers, acquisitions, cloud migrations, and decentralized technology purchases. Security teams often discover infrastructure they did not realize was still online. Reducing unnecessary public exposure can eliminate attack opportunities before patching or advanced detection becomes necessary.
Vulnerability management remains another essential component, even though exposure management extends beyond it. Organizations still need to identify missing patches, insecure software versions, and known flaws across endpoints, servers, network devices, and applications. The difference is that vulnerability findings are enriched with broader context rather than being handled as an isolated list. Exploitability, asset value, threat intelligence, and attack paths can change remediation priority significantly. Exposure management therefore does not replace vulnerability scanning. It makes vulnerability data more actionable by connecting it with the circumstances that determine whether an attacker can use the weakness effectively.
Identity exposure has become increasingly important because attackers frequently target user accounts rather than infrastructure directly. Weak passwords, inactive accounts, excessive permissions, missing multifactor authentication, and privileged identities can provide paths into sensitive systems. Cloud environments make identity relationships even more complicated because one role may inherit permissions through several policies and groups. Exposure management maps these relationships to identify accounts that could be abused for privilege escalation or lateral movement. Removing unnecessary permissions can sometimes reduce risk faster than patching dozens of unrelated software vulnerabilities. Strong identity governance is therefore central to modern exposure reduction.
Cloud and configuration security provide another major source of exposure data. Cloud environments can be created and changed rapidly, making manual reviews difficult to maintain. Security tools detect public storage, unrestricted security groups, overly broad IAM permissions, unencrypted resources, weak logging, exposed secrets, and other risky configurations. Containers and Kubernetes environments introduce additional configuration layers that must be monitored. Exposure management places these findings alongside vulnerability and identity data so teams can see how cloud weaknesses combine. A publicly reachable workload with a vulnerable service and powerful cloud role may represent a particularly dangerous exposure chain.
Threat intelligence and business context help determine which exposures deserve immediate attention. Threat intelligence can show whether attackers are actively exploiting a vulnerability, whether exploit code is widely available, or whether a particular technology is being targeted by ransomware groups. Business context explains what the affected asset actually does for the organization. An exposure on a public authentication system supporting thousands of customers may warrant urgent action even when its technical severity is moderate. Combining technical, threat, and business information produces a more realistic picture of risk. This context is what transforms exposure management from broad scanning into focused cyber risk reduction.
Exposure Management vs Vulnerability Management
Vulnerability management focuses primarily on identifying, assessing, and remediating known weaknesses in software and systems. Organizations use scanners and asset inventories to detect missing patches, insecure versions, and known vulnerabilities. Findings are commonly assigned severity ratings that help teams decide which systems should be updated first. This process remains a fundamental part of cybersecurity because unpatched vulnerabilities provide attackers with well-understood entry points. However, vulnerability management usually concentrates on individual technical flaws. It may not fully explain whether those flaws are reachable, connected to important systems, or combined with other weaknesses that create a larger attack path.
Exposure management uses vulnerability data but expands the analysis significantly. It considers internet exposure, cloud configuration, identity permissions, application weaknesses, asset criticality, threat activity, and relationships among systems. A server can create risk even when it has no known critical vulnerability if it is publicly accessible with weak authentication and stores sensitive information. Conversely, a system with several high-severity vulnerabilities may present limited immediate danger if it is isolated, temporary, and protected by strong compensating controls. Exposure management therefore asks whether the organization is realistically exposed to attack. Vulnerability management asks more specifically which known technical flaws are present.
Another difference involves prioritization. Traditional programs may produce thousands of high and critical vulnerabilities, leaving remediation teams overwhelmed. If every finding is urgent, teams struggle to determine what should actually be fixed first. Exposure management narrows the list by considering exploitability and potential business impact. A vulnerability that sits directly on an attack path to a domain administrator or production database may rise significantly in priority. A similar vulnerability on an isolated test device may move lower. This prioritization helps security teams align remediation effort with the outcomes attackers are most likely to pursue.
The two practices should therefore complement each other rather than compete. Vulnerability scanning supplies essential technical information that exposure management needs for accurate analysis. Patch management remains necessary because exposure scoring does not remove the underlying software flaw. Exposure management simply helps organizations decide which patches, permission changes, configuration fixes, and architectural improvements should happen first. Mature security programs can maintain broad vulnerability hygiene while using exposure intelligence to accelerate the most important actions. This combination provides both systematic coverage and practical risk prioritization.
Exposure management also creates stronger links between security and business teams. A vulnerability ticket stating that a server has a severity score of 9.8 may not explain why an application owner should interrupt other work immediately. An exposure-based explanation can show that the server is publicly reachable, contains customer information, has active exploit activity, and provides a path toward a critical application. That context makes the remediation decision easier to understand. Security teams can communicate in terms of business impact rather than isolated technical ratings. Better communication often improves remediation speed because stakeholders understand exactly what risk the requested change is reducing.
Attack Paths and Risk Prioritization
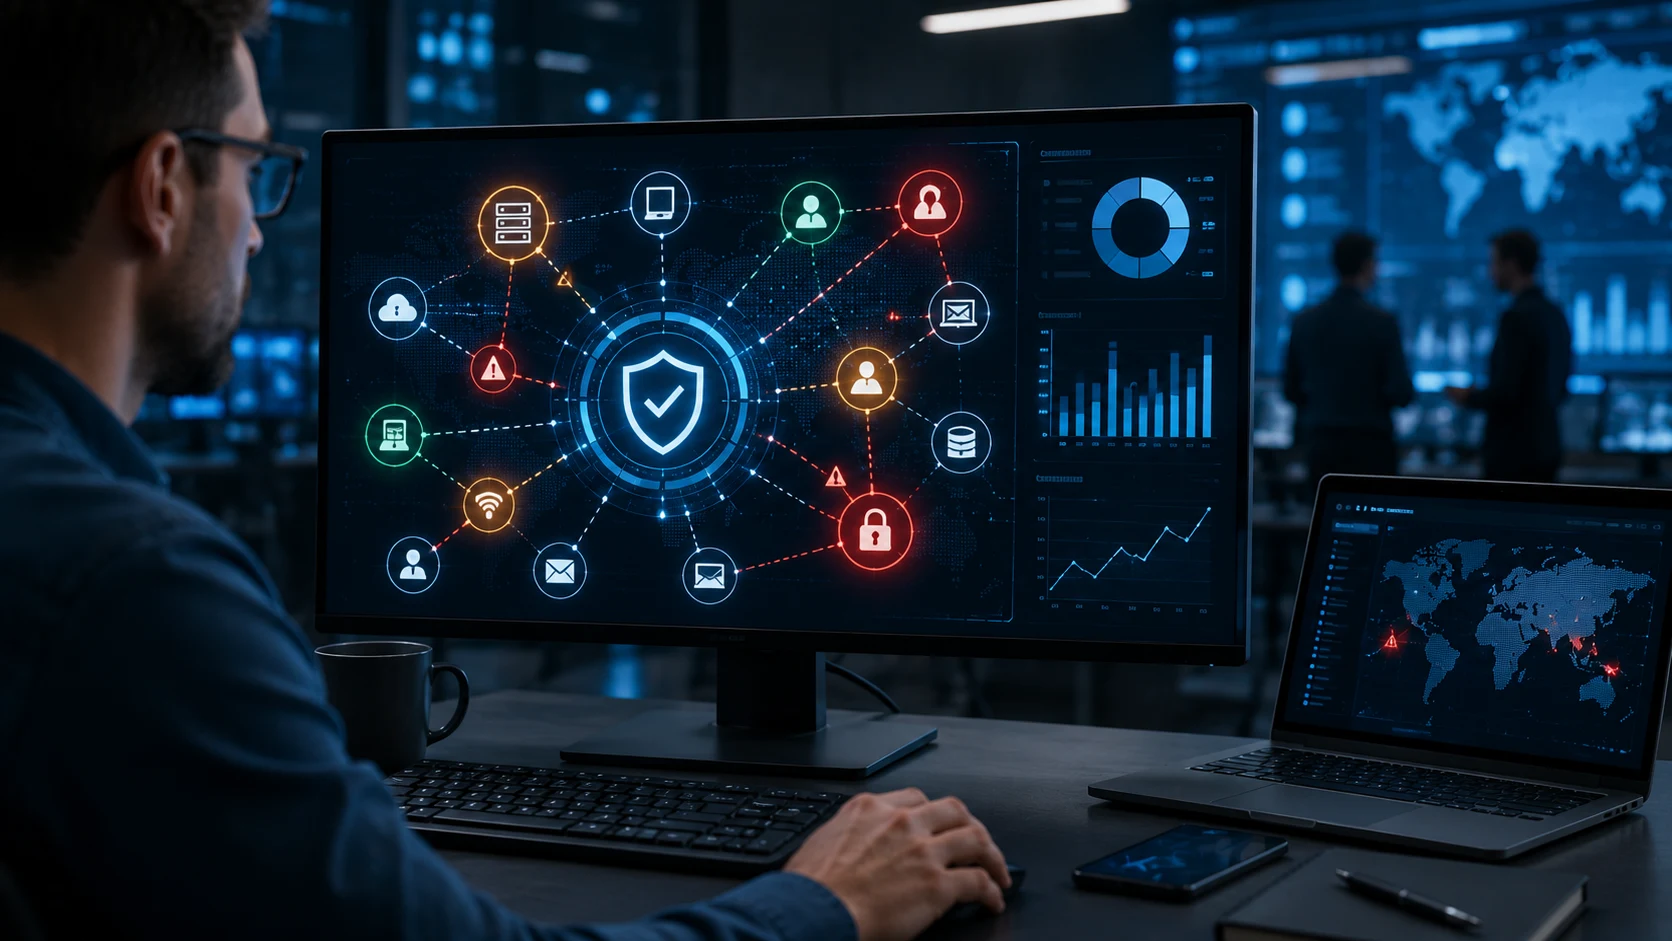
An attack path is a sequence of weaknesses or relationships an attacker could potentially use to move from an initial entry point toward a valuable target. The path may begin with an internet-facing application and continue through compromised credentials, excessive permissions, and an internal system. Each individual weakness may appear manageable when reviewed separately. Together, however, they can provide a realistic route toward sensitive data or privileged control. Exposure management maps these relationships so defenders can see how one weakness increases the importance of another. This helps security teams move from vulnerability counting toward understanding possible attacker behavior.
Identity relationships often create some of the most dangerous attack paths. A low-privilege employee account may belong to a group that can access a server where administrator credentials are stored. Those credentials may provide access to another system with broader cloud permissions. An attacker can move through these relationships even when no single step looks like a catastrophic security failure. Attack path analysis reveals where privilege can accumulate. Removing one unnecessary group membership or stored credential may break the entire chain and reduce more risk than patching several unrelated systems.
Network connectivity also shapes attack paths. A vulnerable server that cannot communicate with sensitive systems presents different risk from one connected directly to critical databases and identity infrastructure. Segmentation reduces opportunities for lateral movement by limiting which systems can communicate. Exposure management can analyze firewall rules, network paths, security groups, and service relationships to understand where attackers could travel after compromising an initial host. This helps teams identify overly broad connectivity that traditional vulnerability scans may not flag. Reducing connectivity can sometimes eliminate several potential attack routes at once.
Business importance influences which attack paths deserve the most attention. A route toward an unused development system may be technically interesting but less urgent than a route toward payroll, customer data, intellectual property, or production infrastructure. Asset classification and business impact analysis help security teams identify high-value targets. The most dangerous exposures are often those combining easy initial access with a clear path to something important. Prioritization should therefore account for both attacker opportunity and potential consequence. Focusing only on one side can produce misleading risk rankings.
Effective prioritization also considers whether attackers are currently exploiting the technologies involved. Threat intelligence can reveal that a vulnerability previously considered theoretical is now being used actively in real attacks. Public exploit code can lower the skill level required to take advantage of a weakness. Exposure to the internet further increases urgency because attackers can scan broadly for vulnerable systems. Security teams can combine these signals with asset criticality and attack paths to create remediation queues. The result is a smaller set of actions tied more directly to realistic cyber risk.
How Exposure Management Reduces Cyber Risk
Exposure management reduces cyber risk first by improving visibility. Organizations cannot protect assets they do not know exist, and shadow IT is a common source of security problems. Continuous discovery reveals forgotten systems, unmanaged cloud resources, external applications, and unexpected services before attackers exploit them. Visibility also improves understanding of who owns each asset and what business function it supports. Security teams can then ensure those systems receive patching, monitoring, and access controls. Simply eliminating unnecessary exposed assets can reduce the attack surface substantially.
Risk-based prioritization improves security efficiency because teams stop treating every finding as equally important. Security departments often face more vulnerabilities and configuration issues than they can remediate immediately. Exposure management identifies the weaknesses that contribute most directly to realistic attack scenarios. Engineering teams can then focus on changes that remove the largest amount of risk with available resources. This does not mean lower-priority issues should be ignored forever. It means remediation order reflects threat likelihood and business impact rather than only scanner severity.
Exposure management can also reduce attacker movement inside an environment. Mapping identity permissions and network relationships reveals where one compromised system can lead to broader control. Teams can remove unnecessary administrative privileges, restrict service accounts, segment networks, and limit connections between systems. These actions make it harder for attackers to move laterally after gaining an initial foothold. Breaking one strategic attack path can protect several downstream assets simultaneously. This approach strengthens defense even when every individual vulnerability cannot be fixed immediately.
Continuous validation provides another important benefit because organizations can confirm whether security improvements actually work. A patch may appear installed while the vulnerable service remains exposed because of an incomplete deployment. A firewall change might block one route but leave an alternative path open. Validation tools and controlled security testing help verify whether the attacker opportunity has truly disappeared. This feedback makes exposure management more outcome-focused than processes that close tickets based only on administrative confirmation. Security teams gain evidence that remediation changed the environment as intended.
Finally, exposure management supports better communication about cybersecurity risk. Executives and business leaders rarely need detailed lists containing thousands of vulnerability identifiers. They need to understand which business services are exposed, how attackers could reach them, and whether risk is increasing or decreasing. Exposure management metrics can show high-risk attack paths, critical assets with unresolved exposures, remediation progress, and trends over time. This creates a stronger link between technical security work and business priorities. When leadership understands the risk being reduced, security investment and remediation decisions become easier to justify.
Best Practices for Building an Exposure Management Program
Start with accurate asset visibility and ownership. Organizations should combine discovery from cloud platforms, endpoint tools, network scans, identity systems, SaaS inventories, and external attack surface monitoring. Every important asset should have enough context to identify its owner, purpose, environment, and business importance. Temporary infrastructure should also be included because short-lived systems can still introduce serious risk. Asset information needs regular updating as systems appear and disappear. Exposure management built on an incomplete inventory will inevitably miss weaknesses attackers may discover themselves.
Prioritize according to real-world risk rather than severity labels alone. Teams should consider whether the asset is internet-facing, whether exploitation is occurring in the wild, whether sensitive information is involved, and whether the weakness provides access toward other critical systems. Identity privilege and network reachability should influence rankings alongside vulnerability scores. Business owners can help classify assets according to operational importance. This context reduces alert fatigue and creates remediation queues people can actually complete. Priority models should also be reviewed periodically because threat conditions and business systems change over time.
Integrate exposure management with existing security and IT workflows rather than creating another isolated dashboard. High-priority findings should move automatically into ticketing, patch management, cloud engineering, application development, or identity governance processes. Responsible teams need clear remediation instructions and evidence explaining why the issue matters. Ownership rules should prevent findings from remaining unassigned indefinitely. Security teams should also track whether deadlines match the level of risk. Integration turns exposure analysis into operational action instead of leaving valuable findings trapped inside a security platform.
Validate important remediation actions and attack paths continuously. Penetration testing can provide deep human analysis at selected intervals, while automated attack simulation and validation tools can assess specific controls more frequently. Organizations should verify that critical systems cannot be reached through previously identified routes after fixes are applied. Validation is particularly useful for permission changes, segmentation, and complex cloud environments where configuration interactions are difficult to predict manually. The goal is to measure whether attacker opportunities disappeared. Closing a ticket without verification can create false confidence.
Measure progress using risk reduction rather than only raw activity counts. Reporting the number of vulnerabilities closed can look impressive while leaving the most important attack path untouched. Better metrics may include the number of critical assets with exploitable exposure, average time to remediate high-risk findings, externally reachable attack paths, excessive privileged access, and recurring configuration problems. Trend analysis can show whether exposure is shrinking as the organization changes. Leadership should also understand which risks remain accepted and why. A mature exposure management program focuses on reducing meaningful opportunities for attackers rather than simply generating more security data.
Frequently Asked Questions About Exposure Management
What is exposure management in cybersecurity?
Exposure management is the continuous process of discovering, prioritizing, validating, and reducing security weaknesses across an organization’s technology environment. It considers vulnerabilities, identities, cloud configurations, attack surfaces, asset importance, and attack paths together.
How is exposure management different from vulnerability management?
Vulnerability management focuses mainly on known software and system flaws. Exposure management uses vulnerability data but also considers internet exposure, permissions, cloud misconfigurations, threat intelligence, business impact, and how weaknesses combine into realistic attack paths.
What is an attack path in exposure management?
An attack path is a sequence of systems, permissions, vulnerabilities, or misconfigurations that could allow an attacker to move from an initial entry point toward a valuable target. Breaking one important step in the path can significantly reduce the chance of a successful compromise.
Why is exposure management important?
Exposure management helps organizations focus limited security resources on weaknesses most likely to lead to meaningful business impact. It reduces alert overload, improves remediation priorities, reveals hidden attack paths, and provides better visibility into how cyber risk changes over time.
Is exposure management a one-time security assessment?
No. Exposure management is designed to be continuous because assets, vulnerabilities, permissions, cloud configurations, and attacker techniques change constantly. Organizations need ongoing discovery, prioritization, remediation, and validation to keep exposure under control.