
Integrated Risk Management Software: Complete Guide
Integrated risk management software helps organizations identify, assess, monitor, and respond to risks across different departments from one connected platform. Instead of managing cybersecurity, compliance, operational risk, vendor risk, financial exposure, and business continuity in separate spreadsheets or disconnected tools, an IRM platform brings these activities together. It gives leaders a broader view of how risks are related and how one event could affect several parts of the business. Modern platforms often include risk registers, control libraries, assessments, dashboards, workflow automation, incident tracking, and compliance mapping. They can also connect risk information with business objectives, critical assets, third parties, and regulatory requirements. The result is a more coordinated approach to understanding uncertainty and making informed decisions.
Integrated risk management has become increasingly important because organizations depend on cloud systems, external vendors, digital services, complex supply chains, and changing regulatory environments. A cybersecurity incident can quickly become an operational, financial, legal, and reputational problem rather than remaining an IT-only issue. Similarly, a supplier failure may interrupt production, affect customers, create contractual problems, and increase financial costs at the same time. IRM software helps organizations see these connections before decisions are made in isolation. It also gives executives a consistent way to compare different risks using common scoring and reporting methods. This guide explains integrated risk management software, how it works, its main features, benefits, use cases, implementation steps, and what to consider when selecting a platform.
What Is Integrated Risk Management Software?
Integrated risk management software is a platform used to coordinate risk-related activities across an organization rather than handling each risk category separately. It typically provides a central place to record risks, evaluate likelihood and impact, assign ownership, document controls, track remediation, and monitor changes over time. The platform may support operational risk, cybersecurity risk, compliance risk, financial risk, strategic risk, third-party risk, and business continuity. Each area can maintain specialized information while still contributing to a shared enterprise risk view. This structure helps organizations identify relationships between risks that might otherwise remain hidden. IRM software therefore acts as both a management system and a decision-support tool.
The word integrated is important because traditional risk management programs often develop separately within different departments. Security teams may maintain vulnerability spreadsheets, legal teams track regulatory obligations, procurement monitors suppliers, and finance handles financial exposures independently. Each group can understand its own risks well while leadership still lacks one coherent picture of overall business exposure. Integrated risk management connects these areas using shared risk categories, scoring models, controls, owners, and reporting. A critical cloud provider, for example, can be linked simultaneously to cybersecurity, operational resilience, vendor, and compliance risks. This shared context makes cross-functional risk easier to understand.
IRM software also supports the risk lifecycle rather than simply storing a list of problems. A risk can be identified, analyzed, assigned to an owner, connected with controls, treated through mitigation actions, and monitored until its status changes. The system can record whether management chooses to reduce, avoid, transfer, or accept a particular risk. Automated reminders can notify owners when assessments, control tests, or action plans become overdue. Historical records show how risk ratings changed after corrective work was completed. This lifecycle approach improves accountability because every major risk has a documented path from discovery to decision.
Many IRM platforms also connect risks with business objectives and assets. Instead of saying only that a vulnerability or vendor issue exists, the system can show which revenue-generating service, customer process, location, technology platform, or strategic goal could be affected. This makes risk information more meaningful to leaders who need to allocate budgets and resources. An issue affecting a low-value internal application may receive a different priority from one threatening a customer payment platform. Business context therefore turns technical findings into information decision-makers can compare across departments. It also helps executives understand why certain remediation activities deserve urgent attention.
Integrated risk management software does not eliminate uncertainty or replace leadership judgment. Risk scoring models are useful, but they cannot predict every business event precisely. Organizations still need subject-matter experts who understand operational conditions, legal obligations, security threats, and strategic priorities. The software provides structure, evidence, and visibility so those people can make more consistent decisions. A poorly designed risk process will not automatically improve simply because it is moved into a sophisticated platform. The strongest results come when technology supports clear governance, defined ownership, useful risk criteria, and regular management review.
How Does Integrated Risk Management Software Work?
The IRM process usually begins with identifying risks across the organization. Employees, managers, auditors, security tools, compliance teams, vendor assessments, and incident reviews can all contribute new risk information. A risk record typically includes a description, category, affected business area, owner, potential impact, likelihood, and supporting evidence. The software may also connect the risk to specific assets, third parties, regulations, projects, or business processes. Standardized templates help teams describe risks consistently instead of using completely different formats. This common structure makes later comparison and reporting much easier.
Risk assessment comes next, where organizations evaluate how serious each identified risk may be. Many platforms use likelihood and impact scales to calculate an inherent risk rating before controls are considered. Financial loss, customer impact, operational downtime, regulatory consequences, and reputational damage may all influence the assessment. Organizations can use qualitative scales such as low, medium, and high or more detailed numerical scoring methods. Some risks may require scenario analysis or quantitative modeling when potential losses need financial estimates. The purpose is not to produce a perfect number but to support consistent prioritization.
Controls are then mapped to risks to determine how much protection already exists. A cybersecurity risk might be reduced by multifactor authentication, network segmentation, monitoring, and secure backup procedures. A supplier risk could have alternative vendors, contractual protections, inventory buffers, and business continuity plans as controls. The software can record control owners, testing frequency, evidence, effectiveness, and weaknesses. After controls are evaluated, the organization can calculate residual risk, which represents the level of risk remaining after existing safeguards are considered. This distinction helps management decide whether additional action is necessary.
Treatment plans are created when residual risk exceeds acceptable levels. A risk owner may be assigned tasks such as implementing a new control, improving a process, changing a contract, applying a security fix, or purchasing insurance. Workflow automation can route approvals, establish deadlines, and escalate overdue actions to management. The platform tracks progress until each mitigation step is completed and verified. In some cases, leadership may formally accept the remaining risk rather than spend additional resources reducing it. Documenting that decision creates accountability and prevents important risks from disappearing simply because remediation is inconvenient.
Continuous monitoring keeps risk information current after the initial assessment. Key risk indicators, audit findings, incidents, control failures, vendor ratings, and external threat information can trigger reassessment when conditions change. Dashboards show executives whether overall exposure is increasing, which risks remain overdue, and where control weaknesses are concentrated. Some systems integrate with security, finance, HR, or operational platforms so risk data updates automatically. This reduces dependence on occasional manual assessments that become outdated quickly. Integrated risk management therefore works as a repeating cycle of identification, assessment, treatment, monitoring, and improvement.
Core Features of Integrated Risk Management Software
A centralized risk register is one of the most important IRM features because it creates a consistent record of risks across the organization. Each entry can include description, owner, category, likelihood, impact, status, affected assets, related controls, and remediation plans. Departments may maintain different views while leadership sees an enterprise-wide summary. Search and filtering make it easier to find risks connected to a particular supplier, regulation, business unit, or technology system. Historical information shows whether a risk is improving or becoming more serious. A well-designed register prevents important issues from remaining trapped in separate spreadsheets and email conversations.
Risk assessment tools help organizations evaluate exposure using standardized methodologies. Administrators can configure scoring scales, impact categories, likelihood definitions, and risk matrices according to the organization’s needs. Questionnaires can guide users through assessments and automatically calculate ratings based on responses. More advanced platforms may support quantitative risk analysis, scenario modeling, or financial impact estimates. Standardized assessments improve comparability because different departments evaluate risk using the same basic framework. The system can also distinguish inherent risk from residual risk after controls are considered, giving management a clearer view of how effective current safeguards are.
Control management provides another major capability because risk cannot be evaluated properly without understanding what protections already exist. Organizations can maintain control libraries containing policies, technical safeguards, procedures, approvals, and monitoring activities. One control may support several risks and regulatory requirements simultaneously, reducing duplicated testing work. Owners can upload evidence showing that a control operated as expected, while reviewers document test results and deficiencies. Failed controls can automatically generate issues or remediation actions. This makes IRM software useful for both risk management and ongoing assurance activities.
Workflow automation helps organizations move from identifying risk to taking action. The system can send assessments to risk owners, route exceptions for approval, remind employees about overdue tasks, and escalate unresolved issues automatically. Action plans can include multiple tasks with separate owners and due dates. Approval workflows create a formal record when management accepts risk or closes a remediation item. Automated notifications reduce the administrative burden on central risk teams, which otherwise may spend large amounts of time chasing updates. Workflow also improves consistency because similar risk events follow the same defined process.
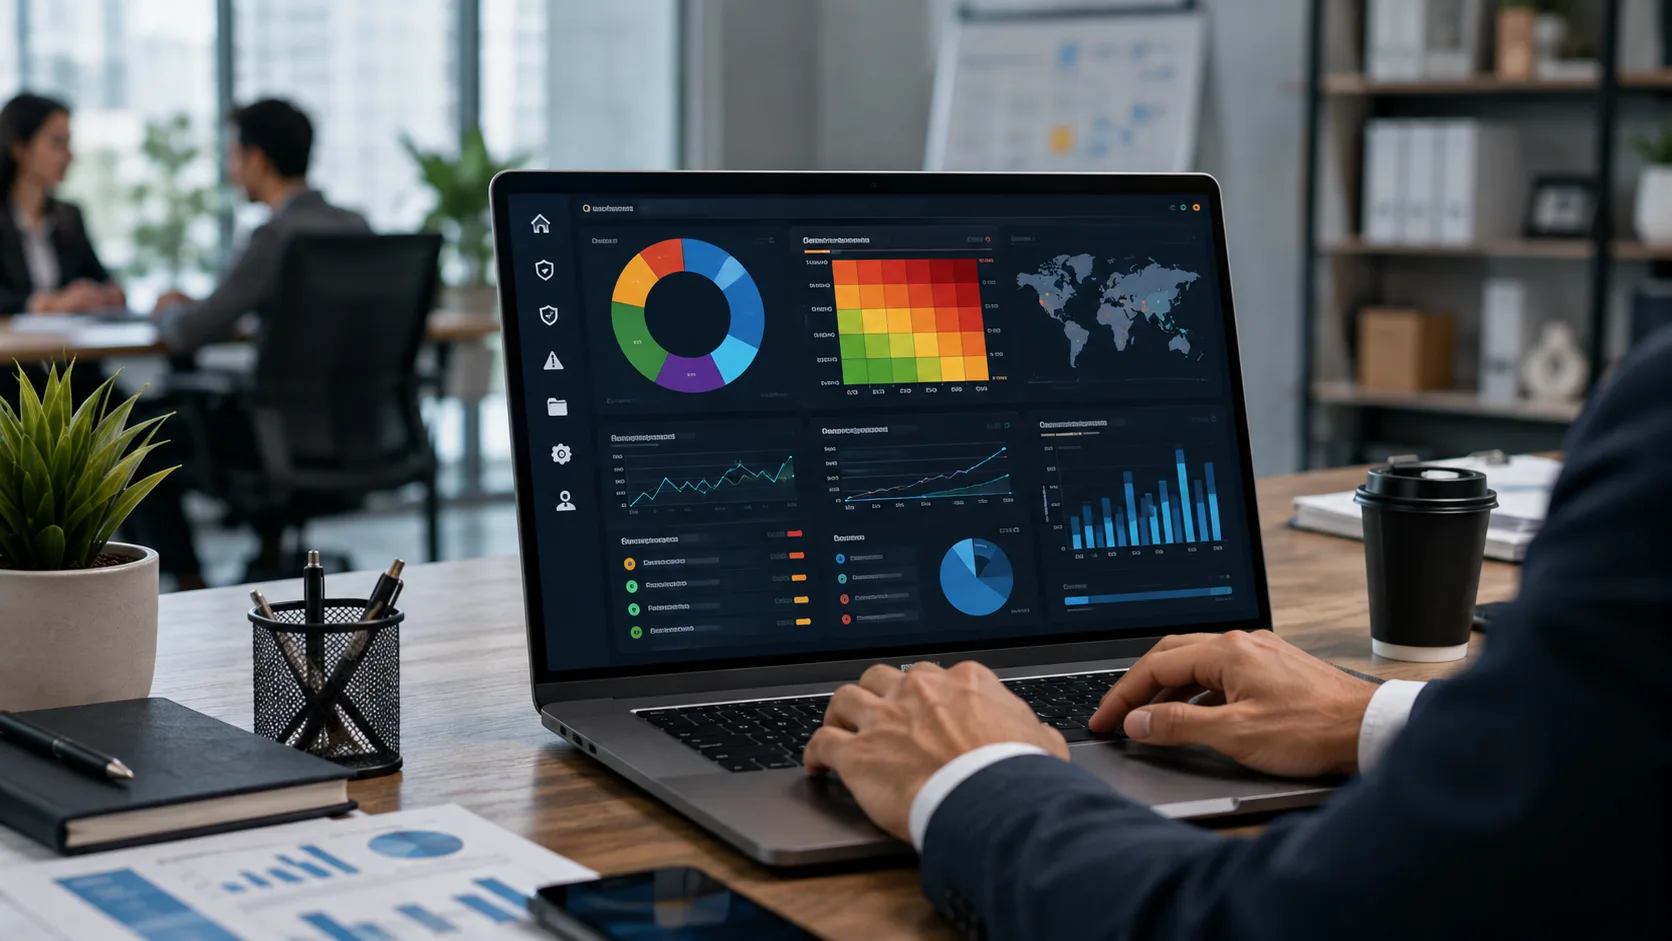
Dashboards and reporting provide leadership with a summarized view of the organization’s risk position. Executives can see top enterprise risks, overdue treatments, control failures, vendor concerns, regulatory gaps, and trends across business units. Heat maps visually compare likelihood and impact, while key risk indicators show whether exposure is moving toward defined thresholds. Reports can also support board meetings, audits, compliance reviews, and risk committee discussions. Good dashboards allow users to move from high-level summaries into detailed supporting records when necessary. This combination helps decision-makers understand both overall risk patterns and the specific issues driving them.
Types of Risk Managed Through IRM Software
Operational risk includes failures in processes, people, technology, facilities, or other resources required for normal business activity. Examples include production interruptions, system outages, processing mistakes, staffing shortages, and breakdowns in internal procedures. IRM software helps organizations identify these events and connect them with critical business services. Controls can be documented, incidents tracked, and recovery actions assigned when weaknesses appear. Operational risk data can also be linked to business continuity and disaster recovery planning. This connection helps organizations understand not only what might fail but also how quickly critical functions need to recover.
Cybersecurity and technology risk are increasingly important areas within integrated risk management. Organizations can record risks related to ransomware, unauthorized access, cloud misconfiguration, data breaches, vulnerable applications, identity weaknesses, or outdated infrastructure. Security findings from technical tools can be translated into business-oriented risk records instead of remaining as isolated vulnerability lists. The platform can show which critical business processes depend on exposed systems. Technology risks can also be connected to relevant controls such as encryption, monitoring, access restrictions, and backups. This helps leadership understand cybersecurity in terms of business impact rather than technical severity alone.
Third-party risk management focuses on suppliers, contractors, cloud providers, consultants, and other external organizations that support business operations. Vendors may process sensitive data, provide critical software, host infrastructure, or supply essential materials. IRM software can store assessments, contracts, security findings, certifications, service dependencies, and performance information for these relationships. Critical suppliers can receive more frequent reviews based on the potential impact of their failure. The platform may also track fourth-party dependencies when one supplier relies heavily on another provider. This visibility helps organizations identify concentration risk and weak links outside their direct control.
Compliance and regulatory risk arise when organizations fail to meet legal, industry, contractual, or internal requirements. IRM platforms can map specific requirements to controls, policies, business processes, and evidence. When one control satisfies several frameworks, the organization can test it once and reuse the results across multiple compliance obligations. Regulatory changes can trigger reviews of affected processes and policies. Audit findings can be connected directly with related risks and corrective actions. This approach makes compliance more closely integrated with enterprise risk instead of treating every regulation as an independent checklist exercise.
Strategic and financial risks can also be managed through IRM platforms when organizations want a broader enterprise view. Strategic risk may involve market changes, failed investments, new competitors, major projects, or dependence on one product category. Financial risk can include liquidity problems, credit exposure, currency movements, or unexpected costs. These risks often require different assessment methods from cybersecurity or operational issues, but they still benefit from shared governance and reporting. An integrated platform lets executives compare different sources of uncertainty using common business priorities. This broader perspective helps align risk decisions with strategic planning rather than managing risk only as a defensive function.
Integrated Risk Management vs GRC and ERM
Integrated risk management and governance, risk, and compliance, commonly called GRC, overlap substantially. GRC traditionally focuses on connecting organizational governance, risk processes, compliance requirements, and internal controls. Many GRC software platforms already include features such as risk registers, policy management, audit tracking, control testing, and compliance reporting. IRM emphasizes integration and business decision-making across multiple risk domains rather than viewing compliance as the primary organizing concept. In practice, the software categories often overlap so heavily that different vendors use different labels for similar capabilities. Buyers should therefore focus on functionality rather than terminology alone.
Enterprise risk management, or ERM, is a broader management discipline focused on identifying and managing risks that could affect organizational objectives. ERM includes strategic, financial, operational, legal, technology, and reputational risk, depending on the business. Integrated risk management software can support an ERM program by providing the workflows, dashboards, and data structures required to coordinate those risks. However, ERM is not simply a software product. It depends on leadership, governance, risk appetite, ownership, and integration with strategic planning. The platform supports those activities but cannot define the organization’s risk philosophy by itself.
IRM differs from siloed risk management primarily through the connections it creates. A security team may identify a vulnerability, while a compliance team separately knows that the affected system supports regulated data. Operations may understand that the same application is critical to customer service, and procurement may know the hosting provider has experienced previous outages. An integrated platform brings those facts together around one risk scenario. This helps organizations recognize when several moderate concerns combine into a much more significant business exposure. Traditional departmental tools may not reveal that broader relationship.
Compliance management software usually has a narrower purpose than a full IRM platform. It may focus on tracking regulatory requirements, collecting evidence, managing policies, and preparing for audits. These functions are valuable but do not necessarily provide enterprise risk analysis, third-party risk, business continuity, or strategic risk capabilities. IRM can include compliance as one risk domain alongside several others. Organizations with limited needs may still prefer a focused compliance tool rather than a larger integrated platform. The right choice depends on program maturity and how much cross-functional risk coordination the business actually needs.
The most important distinction is whether the software supports the organization’s desired operating model. A company trying to manage only cybersecurity findings may not need a broad enterprise platform, while a regulated multinational organization may require extensive controls, risk mapping, vendor oversight, and board reporting. Product category labels should not drive the decision. Buyers should evaluate data models, workflows, integrations, analytics, scalability, and governance capabilities against real business requirements. Integrated risk management works best when the technology supports how risk decisions are actually made across the organization.
Benefits of Integrated Risk Management Software
One major benefit of IRM software is improved risk visibility. Senior leaders can see high-priority risks across technology, operations, suppliers, compliance, and strategy without requesting separate reports from every department. Common scoring and categorization make it easier to compare different types of exposure. Dashboards can highlight which business units face increasing risk and which corrective actions are overdue. This enterprise-wide visibility is particularly valuable when one event could affect several functions simultaneously. Leadership gains a more complete picture of uncertainty rather than receiving fragmented views that may contradict one another.
Better prioritization is another important benefit because organizations rarely have enough resources to address every risk at the same time. IRM platforms combine impact, likelihood, control effectiveness, asset criticality, and other context to identify issues requiring the most urgent attention. Teams can focus remediation spending where it produces the greatest reduction in business exposure. Lower-priority issues remain visible without competing equally with risks capable of causing significant disruption. This approach improves both efficiency and accountability. Decisions can be explained using documented criteria rather than depending entirely on subjective opinion.
Automation can significantly reduce administrative work within risk programs. Manual programs often require employees to send questionnaires, collect spreadsheets, track overdue actions, and assemble reports repeatedly. IRM software can automate assessment distribution, reminders, approvals, evidence collection, and escalation. Risk owners receive tasks directly while central teams monitor progress through dashboards. Standard templates reduce the effort required to create new assessments or registers. Automation allows skilled risk professionals to spend more time analyzing emerging issues and helping the business make decisions rather than managing routine coordination.
Consistency improves because different departments work from shared processes and terminology. One business unit should not define a “critical” risk completely differently from another unless there is a deliberate reason. Standard likelihood definitions, impact categories, risk acceptance procedures, and control testing methods create a more reliable enterprise view. Historical records also improve continuity when employees change roles. New risk owners can see previous assessments, decisions, and remediation actions instead of reconstructing context from email. Consistency makes both internal management and external assurance more dependable.
Integrated reporting also strengthens communication with executives, boards, auditors, and regulators. Risk teams can create reports showing top exposures, trends, accepted risks, control failures, and remediation progress. Leaders can move beyond large technical spreadsheets and focus on business consequences and treatment decisions. Audit teams benefit from centralized evidence and documented approval histories. Regulators or customers may receive more organized demonstrations of how significant risks are governed. Better reporting does not eliminate risk, but it makes accountability and oversight more effective across the organization.
Real-World Integrated Risk Management Use Cases
A financial services company can use IRM software to connect cybersecurity, operational resilience, regulatory obligations, and third-party dependencies. A critical payment platform may depend on cloud infrastructure, identity services, telecommunications providers, and internal processing systems. The risk platform can map these dependencies and show how one outage could affect customer transactions and compliance requirements. Security findings can be linked to the same service, giving management a combined view of technology and operational exposure. Recovery plans, controls, and remediation actions can then be tracked in one location. This integrated perspective is far more useful than separate reports that never explain their relationships.
A healthcare organization can manage privacy, technology, vendor, and patient-service risks through the same platform. Third-party applications may handle appointment scheduling, billing, medical administration, and communications while storing sensitive personal information. The IRM system can track vendor assessments, contractual obligations, access controls, and incident history. Business units can also document how system outages would affect patient-facing services. Compliance requirements can be mapped to controls and tested periodically. This creates a stronger connection between data protection, operational continuity, and regulatory responsibilities.
Manufacturing companies can use IRM to manage operational technology, supply chain, safety, production, and cybersecurity risks together. A single supplier failure may interrupt production, while a ransomware incident could affect factory systems and delivery schedules simultaneously. The platform can identify critical suppliers, alternative sources, production dependencies, and recovery requirements. Risk owners can track mitigation plans such as additional inventory, secondary vendors, network segmentation, and system backups. Executives can then understand which risks threaten production targets rather than viewing technology and supply chain issues separately. This supports more resilient operating decisions.
A software company can use IRM software to coordinate cloud security, data privacy, availability, third-party services, and product compliance. Customer-facing applications may depend on infrastructure providers, payment processors, analytics tools, identity platforms, and support systems. Risk assessments can identify which vendors or internal components create the greatest concentration of exposure. Security controls, uptime commitments, privacy obligations, and incident response plans can all be connected with relevant services. Product teams can receive remediation tasks directly when risks exceed approved thresholds. The result is a risk program more closely integrated with software delivery and customer commitments.
A large retailer can use IRM to connect ecommerce, payment security, physical operations, logistics, and supplier risk. A disruption affecting a distribution center could create delivery delays across many regions, while a payment-system breach could create both financial and reputational damage. The platform can show how these risks affect revenue-generating processes and customer experience. Business continuity teams can document alternative fulfillment options, while cybersecurity teams track controls protecting transaction systems. Vendor reviews can identify logistics or technology partners requiring stronger oversight. Integrated information helps management prioritize resilience investments across the complete retail operation.
How to Choose and Implement Integrated Risk Management Software
The selection process should begin with defining the organization’s risk management goals. Some businesses need a basic enterprise risk register, while others require extensive cybersecurity, compliance, vendor, continuity, audit, and control-management capabilities. Teams should identify which risk domains need integration and which systems already contain relevant data. User groups, reporting requirements, regulatory expectations, and expected assessment volume should also be documented. A clear scope prevents organizations from purchasing an overly complex platform simply because it offers hundreds of features. The best software is the one that supports the risk program the organization can realistically operate.
Usability should receive careful attention because risk management depends on participation from people outside the central risk team. Business managers may need to complete assessments only a few times each year, so the interface should be understandable without extensive training. Risk owners need clear task lists and simple ways to update mitigation progress. Executives require dashboards that explain business impact without excessive technical detail. Administrators need flexible configuration without depending on developers for every small change. Poor usability often drives employees back toward spreadsheets and email, undermining the benefits of the platform.
Integration capability is another important requirement. The IRM platform may need data from security tools, HR systems, procurement platforms, cloud infrastructure, asset inventories, financial applications, ticketing systems, and identity providers. APIs and prebuilt connectors reduce manual entry and help risk information remain current. A security vulnerability can automatically create or update a risk record when defined conditions are met. Vendor information can flow from procurement systems, while employee and organizational data can update ownership structures. Integration turns IRM into part of the broader technology environment instead of creating another isolated database.
Implementation should usually begin with a manageable number of high-value use cases. Trying to digitize every risk process across the enterprise at once can create complexity and slow adoption. A business might start with enterprise risk and third-party risk before adding compliance, continuity, and cybersecurity integrations later. Existing data should be cleaned before migration so outdated or duplicate risks do not enter the new system. Scoring models and workflows should also be simplified where possible. Early success gives users confidence and provides lessons that improve later expansion.
Governance and continuous improvement remain essential after launch. Organizations need clear rules for creating risks, assigning owners, approving acceptance, testing controls, and closing remediation actions. Risk criteria should be reviewed as business objectives and operating conditions change. Dashboard usage and overdue actions can reveal whether teams are actually adopting the platform. User feedback can identify workflows that are unnecessarily complicated. Integrated risk management software delivers the most value when the organization treats it as a living management system rather than a one-time implementation project.
Frequently Asked Questions About
What is integrated risk management software?
Integrated risk management software is a platform used to identify, assess, monitor, and manage risks across multiple business areas. It can combine enterprise risk, cybersecurity, compliance, third-party risk, operational risk, controls, and reporting within one system.
What are the main features of IRM software?
Common features include risk registers, assessments, control management, workflow automation, dashboards, key risk indicators, issue tracking, third-party risk, compliance mapping, audit trails, and remediation management.
What is the difference between IRM and GRC?
IRM and GRC overlap significantly. GRC traditionally combines governance, risk, and compliance processes, while IRM places stronger emphasis on integrating multiple risk domains and connecting them with business objectives and decision-making.
Who uses integrated risk management software?
Risk managers, compliance teams, cybersecurity professionals, internal auditors, procurement teams, operations leaders, business continuity teams, and executives can all use IRM software. Different users may access different dashboards and workflows based on their responsibilities.
What are the benefits of integrated risk management software?
IRM software improves risk visibility, prioritization, accountability, automation, reporting, and cross-department coordination. It helps organizations focus resources on the risks most likely to affect important business objectives.