
What Is Multicloud Security?
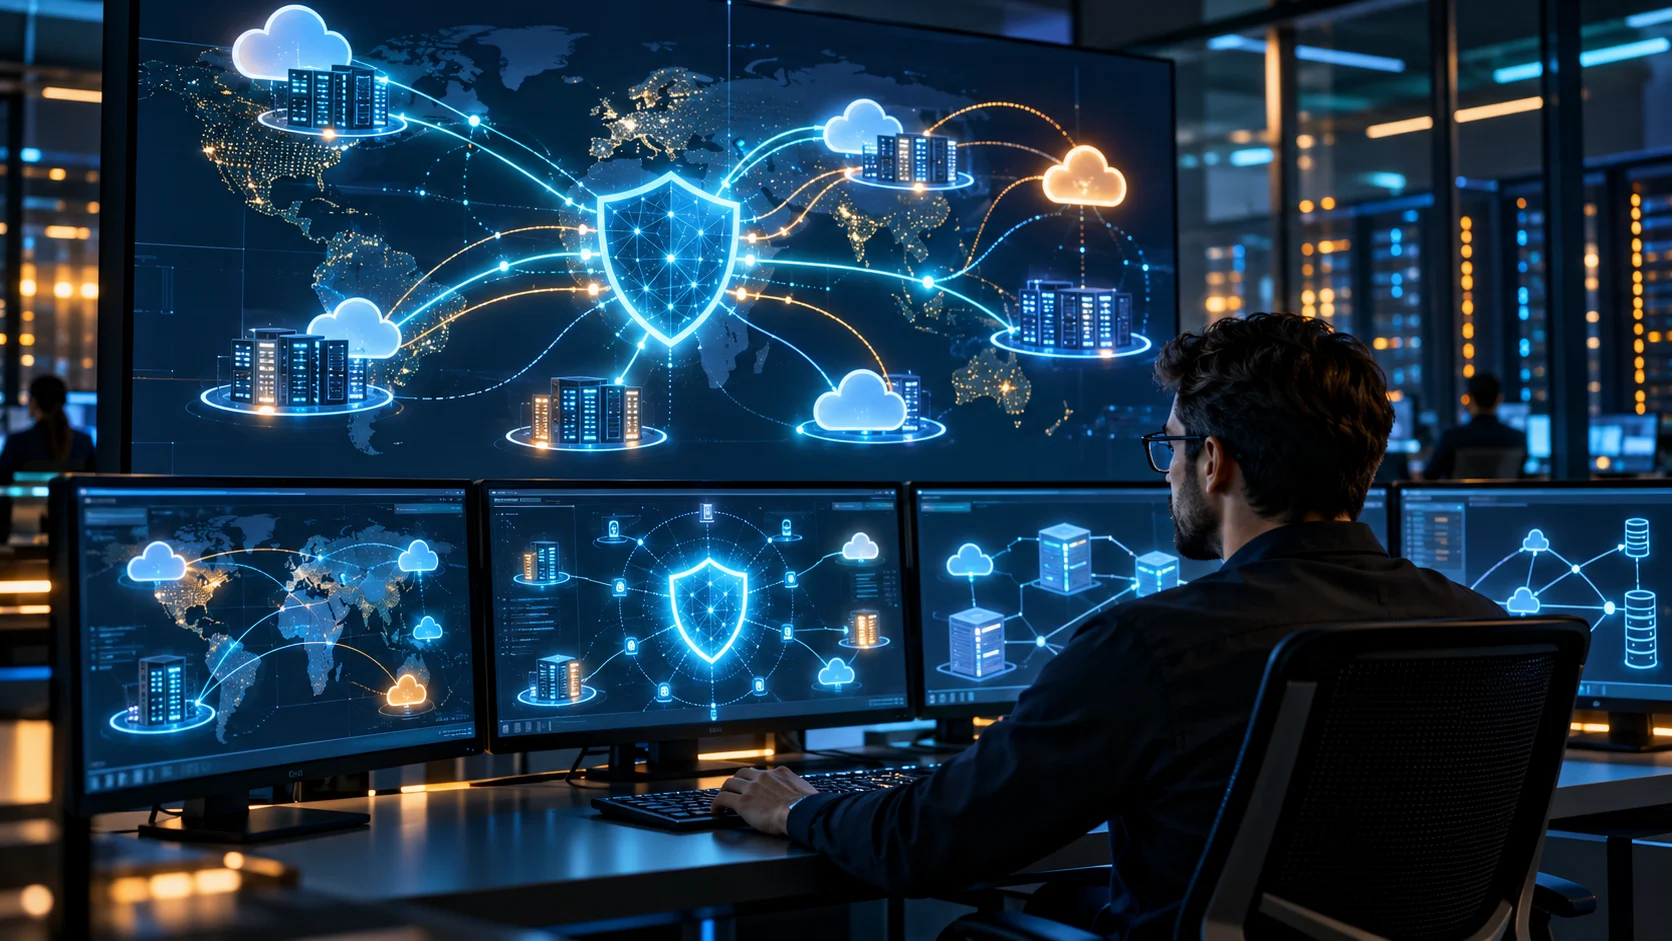
Multicloud security is the practice of protecting applications, data, identities, and infrastructure spread across services from multiple cloud providers. A company might use one provider for databases, another for business applications, and a third for analytics. Each environment has its own tools and settings, so security needs to cover the full system rather than each cloud in isolation.
Multicloud does not always mean hybrid cloud. A multicloud setup uses services from more than one cloud provider, while a hybrid cloud combines private infrastructure with public cloud services. For a quick introduction to cloud service and hosting terminology, see this cloud hosting guide.
The goal is to create consistent protection across different platforms without ignoring their differences. Teams need to know what assets exist, who can access them, how data moves, and who is responsible for each control. Strong multicloud security combines shared policies with provider-specific configuration and monitoring.
Why Organizations Use Multiple Cloud Providers
Organizations may choose multiple cloud providers to access specialized services, support different regional requirements, or avoid relying on one provider for every workload. A company may also inherit different platforms through acquisitions or business units. Multicloud architecture can support flexibility, but it adds security and operational work.
Different services may suit different workloads. One cloud might provide a particular analytics service, while another supports an application that already depends on its infrastructure. This can help teams select tools based on business and technical needs, provided they understand how each service fits into the overall design.
Using multiple providers does not automatically improve resilience or reduce risk. Misconfigured access, duplicated data, inconsistent monitoring, and unclear ownership can create new exposures. Organizations should define the business reason for each cloud service and make sure its security requirements are understood before deployment.
Common Multicloud Security Challenges
A common challenge is fragmented visibility. Each provider has its own console, terminology, logs, policy options, and alerts, which can make it difficult to see the security posture of the whole environment. Teams may overlook a workload, exposed service, or risky permission if cloud inventories are incomplete or inconsistent.
Configuration differences create another source of risk. A setting that is secure by default in one service may require manual changes in another, and teams can make errors when applying policies across different interfaces. Publicly exposed storage, overly permissive network rules, and unprotected management interfaces can result from configuration mistakes.
Operational complexity can also lead to gaps. Security teams may have to coordinate cloud specialists, application owners, developers, and third-party providers across multiple environments. If no one owns a control or incident, detection and response can slow down while teams determine who is responsible and which systems are affected.
Manage Identity and Access Across Clouds
Identity and access management is central to multicloud security because people, applications, and services need credentials to use cloud resources. Start by identifying all human and machine identities, including administrator accounts, service accounts, API keys, and temporary credentials. Remove unused identities and assign each account only the access needed for its work.
Use multifactor authentication for sensitive access, particularly for administrators and remote users. Apply role-based access control or attribute-based policies so permissions reflect a person’s job, resource, and context. Regular access reviews can catch excessive privileges that accumulate when employees change roles or projects.
Where feasible, use a central identity provider and federated access to reduce separate passwords across services. Federation must be configured carefully because a compromised identity system or token can affect multiple environments. Set short token lifetimes where appropriate, protect signing keys, and monitor for unusual authentication or privilege changes.
Protect Data Wherever It Moves
Multicloud environments often spread data across storage, databases, applications, backups, and analytics services. Create an inventory that records what data exists, where it is stored, who owns it, and how sensitive it is. Classification helps teams apply stronger protections to regulated, confidential, or business-critical information.
Encrypt sensitive data in transit and at rest, and define how encryption keys are created, stored, accessed, rotated, and revoked. Key management responsibilities can differ between services, so document which party controls each key and how access is audited. Avoid storing secrets or credentials in code, logs, or unprotected files.
Data movement between clouds can create exposure if transfer paths, permissions, or retention rules are unclear. Restrict sharing to approved accounts and services, and review cross-cloud connections regularly. Keep backup copies protected with separate access controls and test recovery procedures so backups remain useful during an incident.
Secure Networks, Applications, and Workloads
Network security should limit unnecessary paths between users, applications, and cloud resources. Use segmentation to separate workloads by function and sensitivity, and restrict inbound and outbound traffic to approved destinations. A zero-trust approach verifies identity and access for each connection instead of treating network location as proof of trust.
Cloud workloads include virtual machines, containers, serverless functions, and managed services. Apply secure configuration baselines, patch operating systems and dependencies, scan images before deployment, and remove unnecessary services. Automate checks in development and deployment pipelines so common security requirements are tested before workloads reach production.
Application programming interfaces connect services and can expose sensitive data or actions if they are not protected. Require strong authentication, validate inputs, limit permissions, and monitor API activity. For service-to-service communication across clouds, use managed identities or short-lived credentials where available instead of long-lived secrets that are difficult to track and rotate.
Centralize Logging and Monitor Activity
Effective multicloud monitoring starts with collecting important logs from each provider, application, identity system, and network control. Centralized logging can help teams correlate activity across services and investigate events that would be hard to understand from one cloud console alone. Retain logs long enough to support threat detection, compliance, and incident response.
Define alerts for meaningful events such as unusual administrator activity, repeated failed logins, privilege escalation, changes to logging settings, and unexpected data transfers. Too many low-value alerts can overwhelm analysts and hide important signals. Tune detections over time and make sure high-risk alerts have a clear owner and response path.
Protect the logging system itself. Restrict who can change retention or delete records, synchronize system time across environments, and transmit logs through authenticated, encrypted channels. Periodically confirm that critical services are still sending data and that logs can be searched during an investigation.
Create Consistent Governance and Compliance Controls
A multicloud security policy should establish clear minimum requirements across all providers. These may cover identity, encryption, network access, logging, vulnerability management, data handling, and backup. Teams can then adapt implementation to each platform while keeping the intended security outcome consistent.
Cloud providers and customers share security responsibilities, but the division varies by service. A managed application, platform service, and virtual machine do not place the same duties on the customer. Document the provider’s responsibilities alongside your own so teams know who configures, monitors, patches, and responds to each part.
Compliance work becomes more manageable when controls are mapped to the organization’s obligations and tracked across environments. Automate evidence collection where possible, but validate that reports reflect the actual configuration. Governance should help teams make secure decisions early, rather than functioning only as a review step after a workload is already deployed.
Prepare for Multicloud Incidents
Incident response can be difficult when evidence and response tools are spread across several providers. Prepare a plan that explains how to isolate workloads, disable compromised credentials, preserve logs, and contact provider support. Include owners and escalation paths for every cloud account, application, and critical data store.
Run exercises that involve security, IT, application teams, legal, and business stakeholders. Practice scenarios such as a stolen cloud credential, exposed storage, ransomware affecting backups, or a compromised deployment pipeline. Exercises can reveal gaps in access, communication, and decision-making before a real incident puts pressure on the organization.
After an incident, preserve relevant evidence and coordinate across provider teams before making changes that could erase useful records. Document the timeline, affected identities, systems, data, and actions taken. Use the lessons to improve policies, detections, training, and recovery procedures across all cloud environments.
Best Practices for Building a Multicloud Security Program
Begin with an accurate inventory of cloud accounts, services, applications, identities, data stores, and external connections. Assign an owner to each important asset and record its business purpose and risk level. Without a reliable inventory, teams cannot confidently apply policies or prioritize security work.
Standardize foundational controls, then automate them through approved templates and infrastructure-as-code workflows. Use policy checks to prevent common misconfigurations before deployment, and scan for drift after changes occur. Give developers secure patterns they can reuse so good configuration is easier than creating custom settings from scratch.
Review the program regularly as cloud services and business needs change. Track meaningful measures such as unresolved critical findings, time to revoke access, log coverage, backup recovery results, and policy compliance. Use these measures to identify specific gaps, assign corrective work, and verify that improvements remain effective.
Choose Security Tools That Fit the Environment
Multicloud security tools can help with asset discovery, configuration management, threat detection, identity analysis, workload protection, and compliance reporting. Some organizations use provider-native tools, while others add platforms that combine visibility across services. The right mix depends on architecture, team skills, regulatory needs, and existing security investments.
Before adopting a tool, confirm which providers and services it supports and how often it refreshes data. Check whether it can show relationships between identities, workloads, networks, and data, since isolated findings may be hard to prioritize. Test its alert quality and integration with the systems your team already uses.
A security platform cannot replace clear ownership, sound architecture, or trained responders. Tools are most valuable when they support defined processes and lead to action. Start with a specific problem, run a focused evaluation, and confirm that the tool reduces risk or operational effort before expanding its use.
Conclusion
Multicloud security protects the identities, data, workloads, applications, and connections distributed across multiple cloud providers. The main challenges include fragmented visibility, inconsistent configuration, complex identity management, and unclear responsibility. Organizations need a shared view of risk while accounting for each provider’s specific controls.
Build a strong foundation with asset inventory, least-privilege access, encryption, secure workload configuration, centralized logging, and tested incident response. Automate repeatable controls and involve security teams early in cloud architecture decisions. Regular access reviews and recovery exercises help keep protections aligned with changing environments.
A multicloud strategy can support business flexibility, but it requires deliberate security governance. Define why each provider is used, assign owners to important services, and measure whether controls work in practice. With clear policies and ongoing monitoring, teams can manage cloud risk without relying on disconnected provider settings.
FAQs
What is multicloud security?
Multicloud security is the set of policies, tools, and practices used to protect data, identities, applications, and infrastructure across services from multiple cloud providers.
What are the biggest multicloud security risks?
Common risks include misconfigured services, excessive access privileges, inconsistent monitoring, exposed data, weak API security, and unclear responsibility between teams and providers.
How can organizations secure identity across multiple clouds?
Use centralized identity where appropriate, require multifactor authentication, apply least-privilege access, review permissions regularly, and protect tokens, keys, and service credentials.
Should companies use one multicloud security platform?
Not always. A unified platform can improve visibility, but organizations should assess provider coverage, alert quality, integrations, cost, and fit with their existing security processes.
How often should multicloud security controls be reviewed?
Review controls continuously through automated monitoring where possible, and conduct scheduled access, configuration, logging, and recovery reviews. Reassess them whenever architecture, services, or business requirements change.