
Trojan Horse Meaning: How This Malware Attacks
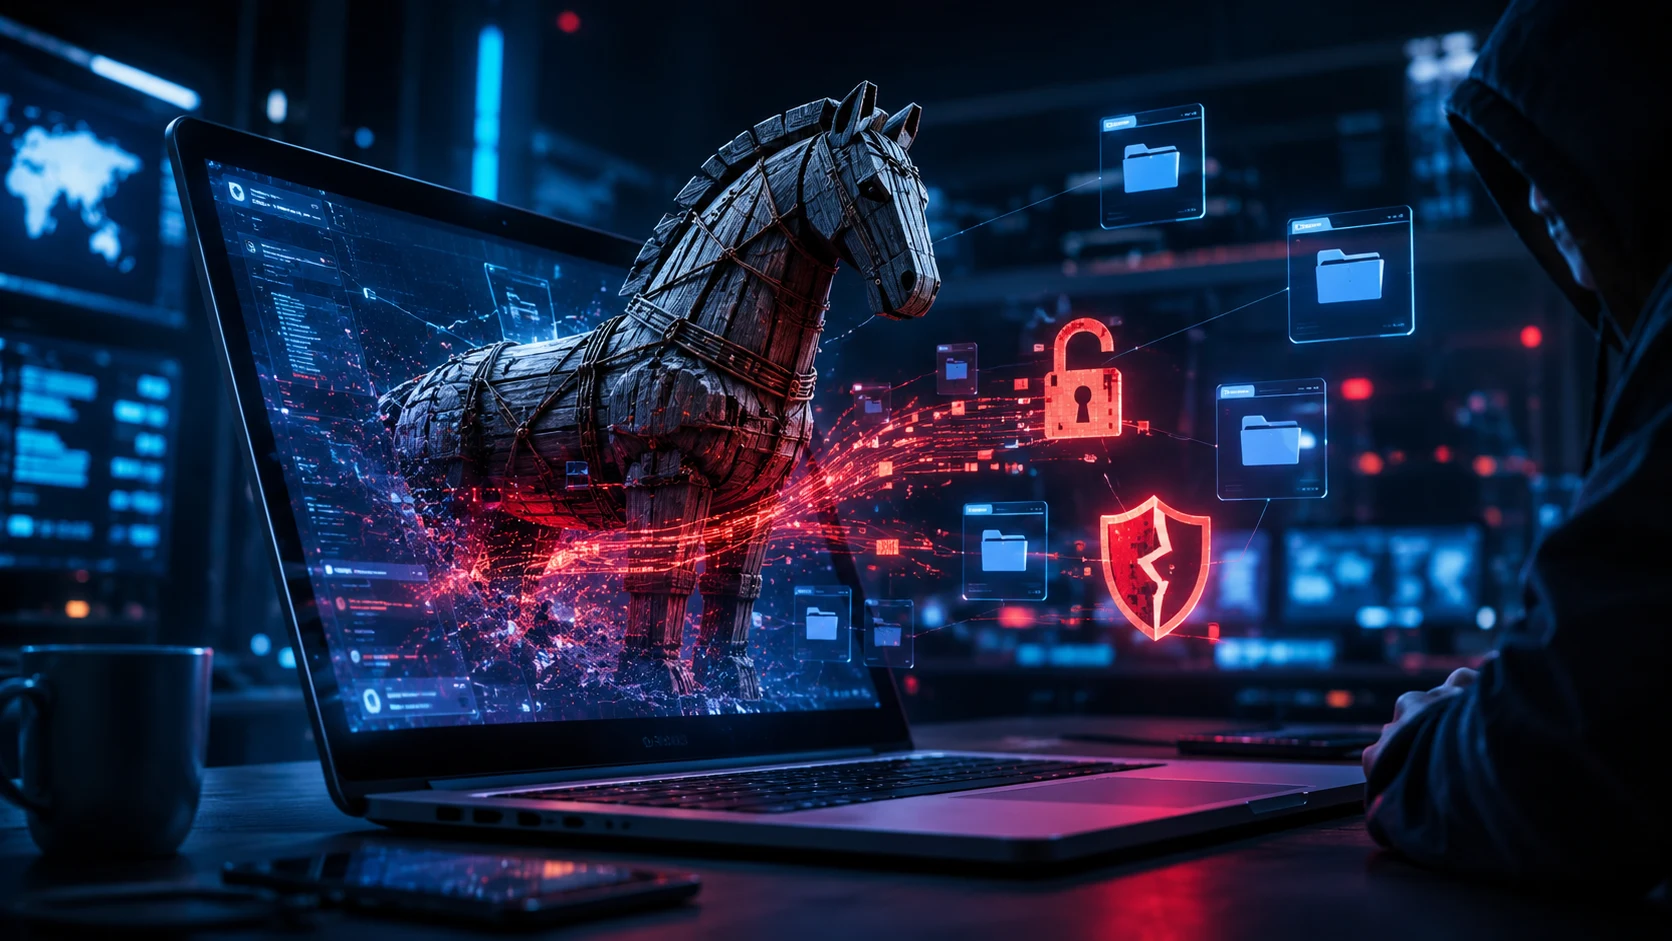
A Trojan horse is a type of malicious software that disguises itself as something legitimate or useful so that a person is more likely to install, open, or run it. Unlike malware that primarily spreads by exploiting systems automatically, a Trojan often depends on deception to gain its first opportunity to execute. It may arrive as a fake software installer, email attachment, cracked application, browser extension, document, game modification, or security update. Once activated, the Trojan can perform hidden actions such as stealing passwords, downloading additional malware, monitoring activity, or giving an attacker remote access. The name comes from the ancient story of the Trojan Horse, where something that appeared harmless concealed a hidden threat. In cybersecurity, the same basic idea describes software that hides malicious behavior behind an apparently trustworthy appearance.
Trojan malware can affect personal computers, business systems, smartphones, and other devices capable of running malicious software. Some Trojans focus on banking credentials, while others create backdoors that allow attackers to control infected machines remotely. A Trojan may also act as a loader that installs ransomware, spyware, cryptominers, or other malware after gaining access. This makes Trojans especially dangerous because the visible file users interact with may be only the first stage of a larger attack. Understanding how Trojans work helps users recognize suspicious downloads and organizations improve their security controls. This guide explains Trojan horse meaning, common types, infection methods, warning signs, prevention, removal, and how Trojan malware differs from viruses, worms, and ransomware.
What Is a Trojan Horse in Cybersecurity?
A Trojan horse in cybersecurity is malicious software designed to appear legitimate while secretly performing unauthorized actions on a device. The attacker tries to convince the victim that the file or program is safe enough to open. A Trojan might pretend to be a document viewer, system utility, game, antivirus program, video file, or installer for popular software. The disguise gives the malware an opportunity to bypass the user’s natural caution. Once the program runs, its hidden code can begin carrying out whatever actions the attacker designed. Those actions can range from monitoring activity to taking full control of the infected system.
The defining feature of a Trojan is deception rather than one specific malicious capability. Two Trojans can behave completely differently after installation while still belonging to the same general malware category. One may steal browser passwords, while another allows remote administration and a third installs ransomware. This flexibility is why the word Trojan often describes the delivery or disguise method more than the final payload. Security tools may classify malware further according to what it actually does. The Trojan label therefore provides an important clue about how the threat gains execution but does not always reveal the full consequences of infection.
Trojans often require some form of user interaction, although attackers continually look for ways to make that interaction minimal. A person might open an attachment, enable a document feature, install an application, or approve a fake update. Social engineering makes these actions more likely by creating urgency, curiosity, fear, or the promise of something useful. Attackers may impersonate employers, delivery companies, banks, software vendors, or colleagues to increase credibility. Once the victim takes the requested action, the Trojan no longer needs to maintain the original disguise. It can begin working quietly in the background while the user believes nothing unusual happened.
A Trojan does not necessarily display obvious signs after installation. Many are intentionally designed to remain quiet because attackers gain more value when victims do not realize they have been compromised. The malware may create scheduled tasks, registry entries, startup items, services, or other persistence mechanisms that allow it to return after the computer restarts. It can communicate with attacker-controlled infrastructure and wait for commands or send stolen information periodically. Some Trojans also attempt to disable security tools or hide their processes. The absence of pop-ups or dramatic system failures therefore does not prove that a device is safe.
Trojan infections can affect organizations as well as individual users. A single employee opening a malicious attachment can create a foothold inside a corporate network. Attackers may then use stolen credentials to reach shared files, cloud applications, administrative systems, or other devices. The Trojan can become the first step in a much larger intrusion involving lateral movement, data theft, fraud, or ransomware. Businesses therefore treat Trojan prevention as part of broader endpoint, email, identity, and network security. Stopping the initial malicious program is important, but limiting what one compromised account can access is equally valuable.
How Does a Trojan Horse Attack Work?
A Trojan attack usually begins with delivery. The attacker needs to place a convincing malicious file, link, installer, or application where the intended victim is likely to encounter it. Email remains a common channel because attackers can send attachments or links while pretending to represent a trusted organization. Malicious advertisements, fake download websites, social media messages, compromised websites, and pirated software can also deliver Trojans. In targeted attacks, the message may include real information about the recipient’s job or company. The better the disguise, the more likely the victim is to take the next step.
The second stage is execution, when the victim or system actually runs the malicious code. A fake installer may display a normal installation screen while the Trojan begins its hidden activity in the background. A malicious document may attempt to exploit a vulnerability or persuade the user to enable functionality that runs code. Some attackers package Trojans inside archives to make scanning or inspection more difficult. Once execution occurs, the attacker has crossed an important security boundary because code is now running on the victim’s device. Endpoint protections may still detect and stop it at this stage if its behavior or file is recognized as malicious.
Persistence is often the next objective because attackers usually want access that survives a restart. A Trojan can create startup entries, scheduled tasks, services, login items, or other mechanisms that automatically relaunch it. More sophisticated malware may abuse legitimate operating system features so its persistence appears similar to normal system activity. Trojans can also store components in hidden or unusual directories to reduce the chance of casual discovery. If the malware gains administrative privileges, it may be able to establish deeper persistence or change security settings. Security teams therefore examine persistence mechanisms closely when investigating a suspected infection.
Many Trojans then communicate with command-and-control infrastructure controlled by the attacker. This communication allows the malware to receive instructions, download modules, or send stolen information. A remote access Trojan may wait for commands such as capturing screenshots, browsing files, or executing additional software. A banking Trojan may send credentials or session information after detecting a financial website. Attackers often try to make network traffic blend into ordinary web communication so it is harder to identify. Network monitoring and endpoint detection can still reveal unusual destinations, unexpected processes, or suspicious patterns of outbound activity.
The final impact depends on the attacker’s objective. A Trojan can remain focused on one device, or it can become the starting point for a broader compromise. Stolen credentials may allow the attacker to log into email, cloud storage, business applications, or remote access systems. Additional malware may encrypt files, steal data, or create new access methods. In some incidents, attackers spend days or weeks exploring the environment before taking visible action. This staged approach explains why Trojan infections can be much more serious than the original malicious attachment might suggest.
Main Types of Trojan Malware
Remote access Trojans, commonly called RATs, are designed to give an attacker remote control over an infected device. After installation, a RAT may allow the attacker to browse files, execute commands, install software, capture screenshots, or interact with connected hardware depending on its capabilities. The victim may see no obvious interface because the malware operates in the background. RATs can be used in targeted espionage as well as broader criminal campaigns. They are especially dangerous when installed on a computer belonging to an administrator or employee with access to sensitive systems. Strong endpoint monitoring can help identify unusual remote-control behavior before the attacker expands access.
Banking Trojans focus on stealing information related to financial accounts and transactions. They may monitor browser activity, capture login credentials, modify displayed webpages, or attempt to intercept authentication information. Some variants target online banking portals, payment systems, cryptocurrency wallets, or financial applications. A banking Trojan can also use fake forms that look like part of a legitimate website to collect additional information from the victim. Because financial services increasingly use stronger authentication, attackers may target session cookies or trick victims into approving transactions instead of stealing only passwords. Keeping browsers, operating systems, and security tools updated helps reduce some of these attack opportunities.
Downloader and loader Trojans are primarily designed to install additional malicious software. The initial Trojan may be relatively small and contain only enough functionality to contact an attacker-controlled server and retrieve another payload. This modular approach allows attackers to change the final malware without changing the original delivery method. A loader might install spyware on one victim and ransomware on another depending on campaign objectives. Attackers can also update their payload after gaining access to better evade security products. This is why detecting a loader should be treated seriously even if it has not yet caused visible damage.
Spyware Trojans collect information from infected systems without authorization. They may capture browser history, screenshots, clipboard contents, keystrokes, saved credentials, documents, or other sensitive data. Some variants are designed to monitor a particular application or user activity rather than steal everything available. Information can be stored temporarily before being sent to the attacker. Business devices can be especially valuable because they may contain customer information, internal documents, or access to corporate services. Data-loss prevention, endpoint detection, and identity controls can reduce the impact when spyware attempts to access information beyond the user’s legitimate permissions.
Backdoor Trojans create hidden ways for attackers to return to compromised systems. A backdoor may open a network listener, establish outbound communication, create new accounts, or provide another mechanism for executing commands remotely. Attackers value backdoors because they can maintain access even after the original phishing message or malicious installer has been forgotten. Some malware combines backdoor behavior with credential theft and downloading capabilities. Removing only the visible malicious file may therefore be insufficient if additional persistence mechanisms remain. A complete incident response investigation should determine what the Trojan changed and whether other accounts or devices were affected.
How Trojans Get Onto Computers and Phones
Phishing is one of the most common Trojan delivery methods because it allows attackers to exploit trust instead of defeating technical defenses directly. A malicious email may claim to contain an invoice, shipping notice, job application, tax document, or urgent account warning. The attachment may actually be an executable, archive, script, or weaponized document. Alternatively, the message can link to a website that delivers the Trojan through a fake download. Targeted phishing may use the victim’s real name, company, or role to make the request more believable. Users should therefore judge unexpected files by context rather than assuming familiar branding proves legitimacy.
Fake software downloads are another major infection route. Attackers create websites that imitate popular applications or place malicious advertisements around search results for commonly downloaded tools. The victim thinks they are installing a browser, media player, game, PDF tool, or system utility, but the package contains Trojan code. Pirated and cracked software is particularly risky because users already expect modified installers and may disable security warnings to make the software work. Attackers can take advantage of that behavior to distribute malware. Downloading applications from official stores or verified vendor websites reduces exposure to these disguised installers.
Fake updates use a similar strategy by pretending that existing software needs an urgent security or performance update. A webpage may display a warning claiming that the browser, video player, operating system, or security software is outdated. Clicking the update button downloads the Trojan instead of legitimate software. Real modern applications usually deliver updates through built-in mechanisms, official stores, or clearly documented vendor channels. Unexpected webpage prompts should therefore be treated cautiously. Users should open the application’s own settings or official update system rather than trusting a random website that insists an immediate download is required.
Mobile Trojans can arrive through malicious applications, unofficial app stores, deceptive links, or applications requesting far more permissions than their stated purpose requires. An app pretending to be a game or utility may ask for access to SMS messages, accessibility services, notifications, or contacts. Those permissions can sometimes be abused to capture authentication codes, monitor activity, or perform unauthorized actions. Android environments allowing installation from outside official stores can face additional risk when users download unknown APK files. Smartphones should be treated as full computing devices because they hold credentials, banking apps, email, personal messages, and business information valuable to attackers.
Trojans can also be delivered through compromised legitimate infrastructure. An attacker who gains control of a trusted website, software distribution account, or development environment may replace a real download with a malicious version. This type of supply-chain compromise is especially dangerous because users may follow normal safe behavior and still receive infected software. Code signing, secure update systems, and vendor security controls help reduce this risk. Organizations should also monitor software behavior after installation rather than assuming every application from a recognized supplier will always remain safe. Layered security is important because no single delivery-control method can stop every Trojan campaign.
What Can a Trojan Horse Do After Infection?
Credential theft is one of the most valuable capabilities for attackers because valid usernames, passwords, and session information can provide access to services beyond the infected device. A Trojan may search browsers for stored credentials, monitor login forms, capture keystrokes, or steal authentication tokens. Those credentials can then be tested against email, cloud accounts, social media, financial services, or company systems. Password reuse increases the damage because one stolen password may unlock several services. Multifactor authentication can reduce some risks, but attackers may still attempt to steal active sessions or trick users into approving requests. Strong identity security therefore remains important even after endpoint protection is deployed.
Data theft is another common objective. Trojans can search local drives and connected storage for documents, spreadsheets, images, databases, source code, and other valuable information. They may also access shared folders or cloud-synchronized files available to the compromised account. Attackers can compress information before sending it out to make transfer easier. Business data may be used for extortion, fraud, espionage, or resale. Personal information can support identity theft and targeted phishing. Limiting users to the data they genuinely need can reduce the amount available to an attacker who compromises one device.
A Trojan can also install additional malware after establishing a foothold. The attacker may deploy ransomware, cryptominers, spyware, credential-stealing tools, or remote-control software depending on the victim’s value. This makes the initial Trojan similar to an entry point rather than the complete attack. Malware loaders can receive different payloads over time as criminal campaigns change. Security teams should therefore investigate downstream activity rather than assuming removal of the first detected file ends the incident. Network connections, scheduled tasks, new services, accounts, and downloaded files all need review when a significant infection is suspected.
Some Trojans can manipulate the infected system directly. They may change browser settings, disable security services, modify firewall rules, redirect web traffic, or create hidden user accounts. Others can capture screenshots, activate microphones or cameras where permissions and platform capabilities allow, or monitor clipboard contents. Remote access Trojans may provide attackers with an interactive view of the device that feels similar to legitimate remote support software. These capabilities can create serious privacy and security consequences. Users should treat unexplained changes to system settings or security tools as warning signs requiring investigation.
In business environments, the most damaging capability may be the access the Trojan enables beyond the original device. Attackers can use credentials and network information to move toward servers, cloud systems, or administrative accounts. They may map the network and identify where valuable data is stored before taking further action. A compromised workstation can therefore become a stepping stone toward a wider breach. Network segmentation, least-privilege access, strong authentication, and behavioral monitoring limit the opportunities available after initial compromise. Endpoint prevention remains important, but organizations should also design networks assuming one device could eventually become infected.
Warning Signs of a Trojan Infection
Unexpected performance problems can be a warning sign, although they are not proof of malware by themselves. A device infected with a Trojan may suddenly become slow because hidden processes are consuming CPU, memory, disk, or network resources. Fans might run more frequently, battery life can fall faster, or applications may take longer to open. These symptoms can also result from legitimate software updates or hardware issues, so they need context. Task managers and system monitoring tools can reveal unfamiliar processes using unusual resources. Security software should be used to investigate rather than deleting random processes based only on their names.
Unexplained network activity can also indicate that malware is communicating with external infrastructure. A computer may upload significant amounts of data while the user is not performing any obvious online activity. Network usage might continue when ordinary applications are closed. Security tools can identify connections from unexpected processes or traffic toward suspicious destinations. Home users may have limited visibility into detailed network behavior, but unusually high data use can still justify a malware scan. Businesses often use endpoint and network monitoring together to identify devices behaving differently from normal peers.
Changes to security software or system configuration deserve attention. A Trojan may attempt to disable antivirus protection, modify firewall settings, stop updates, or add exclusions that prevent malicious files from being scanned. Users may also notice unfamiliar startup entries, browser extensions, scheduled tasks, or applications they do not remember installing. Security warnings that suddenly disappear can be as concerning as warnings that suddenly increase. Attackers benefit when victims believe protection is still functioning normally. Checking security status through the operating system’s trusted settings rather than through unexpected pop-ups helps avoid further deception.
Account-related warning signs can indicate that a Trojan has stolen credentials even if the malware itself remains hidden. Users may receive alerts about logins from unfamiliar locations, password reset messages they did not request, or multifactor authentication prompts that appear unexpectedly. Emails or social media messages may be sent from the account without the user’s knowledge. Financial accounts can show unrecognized activity. These events should trigger both account-security action and examination of the device used to access the account. Changing a password on an infected computer may simply give the attacker the new credential as well.
Pop-ups and fake security alerts can appear with certain Trojan campaigns, particularly those designed to persuade users into installing additional software or paying for fraudulent services. A message may claim that the computer contains dozens of viruses and insist on downloading a specific cleanup tool. Other Trojans may redirect browser searches, change the home page, or open unwanted advertisements. However, sophisticated Trojans often avoid these obvious behaviors because stealth increases their useful lifetime. Users should therefore not rely on visible symptoms as the only indicator of infection. Routine security updates, reputable scanning, and cautious software installation remain necessary even when the device appears normal.
Trojan Horse vs Virus, Worm, Ransomware, and Spyware
A Trojan and a computer virus differ primarily in how they spread and operate. A virus typically attaches itself to legitimate files or programs and replicates when infected content is executed. A Trojan instead relies mainly on disguise and deception, presenting itself as something the user wants or trusts. Trojans do not need to reproduce themselves in the same way viruses do. One malicious program can still infect many victims if attackers distribute it broadly through phishing or fake downloads. The terms are sometimes used loosely in everyday conversation, but cybersecurity professionals distinguish them because their behavior and defenses differ.
A worm is malware designed to spread automatically between systems or across networks without requiring the same level of user interaction associated with many Trojans. Worms often exploit software vulnerabilities or weak services to copy themselves to additional devices. This automated propagation can make a worm spread extremely quickly. A Trojan may instead arrive on one machine through a deceptive installer and remain there unless the attacker uses it to move elsewhere. Some real-world malware combines behaviors and may include both Trojan-like delivery and worm-like propagation. Malware categories describe characteristics rather than always representing completely separate families.
Ransomware is defined mainly by its impact rather than its disguise. It typically encrypts data or otherwise disrupts access and then demands payment, although modern ransomware campaigns may also steal information for additional extortion. A Trojan can serve as the delivery mechanism that installs ransomware after compromising a system. In that scenario, the Trojan and ransomware are different stages of the same attack. This relationship explains why a seemingly small malware alert should not be ignored. Stopping an initial loader can prevent a much more damaging payload from being installed later.
Spyware is malware designed to monitor activity or collect information covertly. A spyware program can itself be delivered as a Trojan if it disguises itself as legitimate software. Likewise, some remote access Trojans contain extensive spying capabilities such as screenshot capture and keystroke monitoring. The categories therefore overlap. “Trojan” describes the deceptive nature or installation approach, while “spyware” describes the information-stealing function. Understanding this overlap is useful because a single malicious program may receive several labels depending on which behavior the security product emphasizes.
Adware, cryptominers, rootkits, and other malware categories can also be delivered through Trojan techniques. A fake application might install software that displays advertisements, consumes computing resources for cryptocurrency mining, or hides deeper malicious components. Attackers choose the payload according to their business model or objectives. The important lesson for users is that a Trojan is not one predictable type of damage. Opening one malicious file can expose a system to many possible outcomes. Prevention should therefore focus on stopping unauthorized code execution and limiting what malware can do afterward rather than defending against only one named category.
How to Prevent Trojan Malware
The most effective prevention habit is to download software only from sources you can reasonably trust. Official vendor websites, established application stores, and organization-approved software catalogs reduce the chance of receiving a modified installer. Avoid cracked programs, unofficial activation tools, and unknown download portals because attackers frequently use them as Trojan delivery channels. Search advertisements can sometimes imitate legitimate download pages, so verify the actual domain before installing important software. File reputation and digital signatures can provide additional confidence when supported. A few extra seconds spent checking the source can prevent a much longer malware recovery process.
Phishing awareness is equally important because many Trojans arrive through messages designed to create urgency or curiosity. Treat unexpected attachments carefully, especially when the sender asks you to open a file immediately or bypass a security warning. Verify unusual requests through a separate communication method when they involve sensitive business activity. Hovering over links can sometimes reveal suspicious destinations, but sophisticated phishing can still use convincing domains. Email filtering and attachment scanning provide technical protection, while user awareness adds another layer. Employees should have an easy way to report suspicious messages without being criticized for asking questions.
Keeping operating systems, browsers, applications, and security products updated reduces opportunities for Trojans that rely on exploitable vulnerabilities. Automatic updates are helpful because users do not need to track every security fix manually. Unsupported software should be replaced when practical because new vulnerabilities may remain permanently unpatched. Browsers and document applications deserve particular attention because they frequently process content received from outside the organization. Updates do not prevent every social-engineering attack, but they reduce the chance that merely opening content can exploit an old weakness. Patch management is therefore a basic part of Trojan prevention.
Reputable antivirus and endpoint protection can identify known Trojan files and suspicious behaviors during execution. Modern endpoint detection may flag unusual process relationships, persistence attempts, credential access, or malicious network connections even when a file has not been seen before. Organizations can strengthen protection through application control that limits which programs are allowed to run. Ordinary users should avoid disabling security software merely because an installer requests it. Legitimate applications rarely need users to permanently turn off core protections. Security warnings should be investigated rather than treated automatically as obstacles.
Least-privilege access and strong authentication reduce the damage when prevention fails. Users should work with ordinary accounts rather than administrator privileges unless elevated access is genuinely needed. Multifactor authentication makes stolen passwords less useful in many scenarios, while unique passwords prevent one credential from unlocking several services. Network segmentation can prevent an infected workstation from reaching every server automatically. Regular backups provide recovery options if the Trojan later deploys destructive malware such as ransomware. Layered protection recognizes that no single security tool can guarantee a Trojan will never execute.
How to Remove a Trojan Horse Safely
If you suspect a Trojan infection, disconnecting the affected device from networks can help limit further communication or spread while the situation is assessed. This may mean disabling Wi-Fi, unplugging Ethernet, or isolating the endpoint through an organization’s security platform. Avoid immediately deleting every suspicious file manually because the Trojan may have installed additional components or persistence mechanisms. Business users should contact their IT or security team quickly because investigation data can be lost if the system is modified extensively. Organizations may need to preserve logs and evidence to understand whether other devices or accounts were affected. Containment is the first priority when the scope is unclear.
Run a scan using trusted and updated security software. The operating system’s built-in security tools or an established endpoint protection product may be able to identify and quarantine known Trojan components. Some threats are easier to detect through an offline scan that examines the system before normal startup processes can hide malicious activity. Avoid downloading random “Trojan remover” programs from pop-up advertisements because fake cleanup tools are themselves a common malware tactic. If security software cannot operate normally, that may indicate deeper compromise. Professional support may be appropriate when sensitive information or business systems are involved.
Passwords and account sessions should be treated as potentially compromised when a Trojan may have stolen credentials. Change important passwords from a separate device that is known to be clean rather than using the suspected computer. Prioritize email, financial accounts, password managers, cloud services, and work credentials because access to these can enable broader compromise. Sign out of existing sessions where services provide that option and review recent login activity. Enable multifactor authentication if it is not already active. In a business environment, security teams may also reset tokens, revoke sessions, and disable suspicious accounts centrally.
A severe Trojan infection may justify reinstalling the operating system or restoring the device from a known-clean image rather than attempting endless manual cleanup. This is particularly true when attackers gained administrator-level control, security tools were disabled, or rootkit-like persistence is suspected. Before restoring files, ensure backups were created before the infection or have been scanned appropriately. Reinstall applications from trusted sources rather than copying unknown executable files from the old system. A clean rebuild provides stronger confidence than removing only the malicious file that happened to trigger an alert. The exact response should match the sensitivity of the device and the severity of the compromise.
Finally, determine how the Trojan entered the system so the same route does not immediately cause another infection. Review recent downloads, email messages, browser extensions, software installations, and security alerts. Patch vulnerable software, remove unnecessary administrator rights, and improve email or web filtering where appropriate. Organizations should examine whether stolen credentials were used elsewhere and whether additional endpoints show similar indicators. Backups, monitoring, and employee training may also need improvement based on lessons from the incident. Trojan removal is most effective when it includes both technical cleanup and prevention of the original attack path.
Frequently Asked Questions About Trojan Horses
What is a Trojan horse in simple terms?
A Trojan horse is malicious software that pretends to be a legitimate or useful file or program. Once the victim runs it, the Trojan can secretly steal data, create remote access, install more malware, or perform other unauthorized actions.
Is a Trojan horse a virus?
No. A virus usually infects other files and reproduces through them, while a Trojan primarily relies on deception to persuade someone to run malicious software. The terms are sometimes used casually, but they describe different malware behaviors.
Can a Trojan steal passwords?
Yes. Some Trojans are specifically designed to steal passwords, browser credentials, authentication tokens, banking details, or other account information. Remote access and spyware Trojans may also capture credentials as part of broader monitoring.
How do Trojans usually infect computers?
Common infection methods include phishing attachments, fake software downloads, pirated applications, malicious links, deceptive updates, and compromised websites or software distribution channels. Mobile devices can also receive Trojanized applications from unsafe sources.
Can antivirus software remove a Trojan?
Reputable antivirus or endpoint security software can detect and remove many Trojan infections. More serious compromises may require additional investigation, credential resets, offline scanning, or a complete system reinstall to ensure that hidden persistence and secondary malware are removed.