
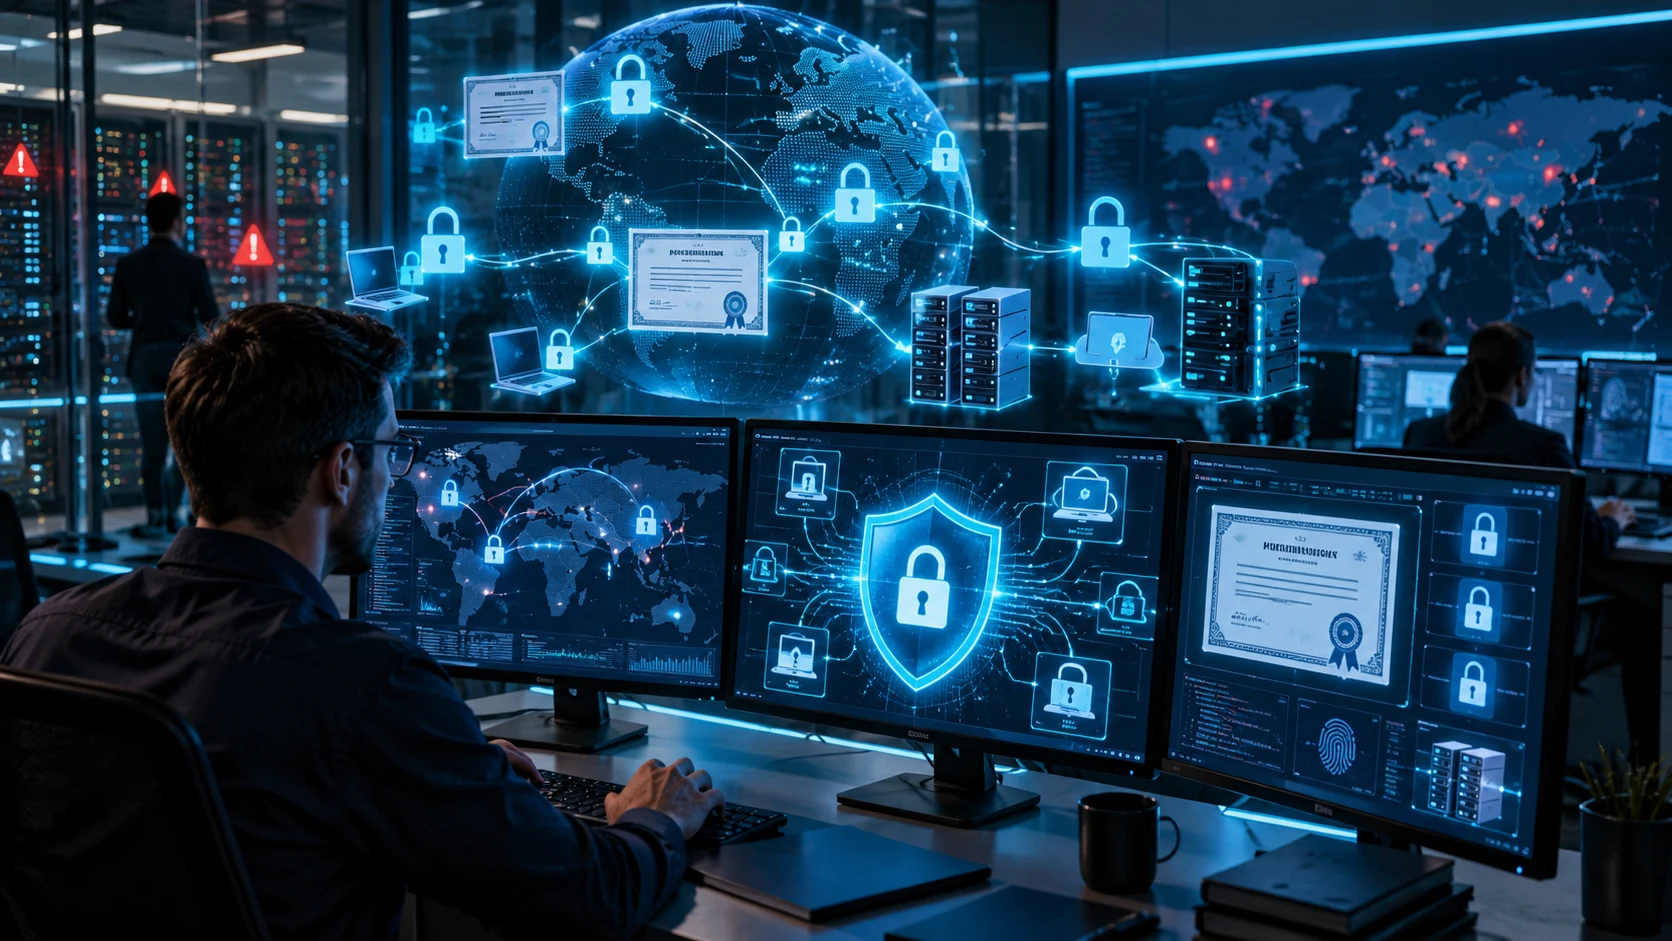
Public Key Infrastructure, commonly called PKI, is a foundational security system used to protect digital communication, verify identities, and establish trust between users, devices, applications, and websites. If you are learning what is PKI in cyber security, the simplest explanation is that PKI combines encryption technologies, digital certificates, keys, policies, and trusted authorities to secure information exchanged over networks.
Every time you visit a secure HTTPS website, authenticate a device, sign a digital document, or establish an encrypted connection, technologies related to PKI may be working behind the scenes. The system helps confirm that you are communicating with the intended service instead of an attacker pretending to be that service. It also protects information from unauthorized interception or modification.
PKI may initially seem complicated because it involves public keys, private keys, certificates, Certificate Authorities, and cryptographic processes. However, the basic purpose is straightforward: establish digital trust. Understanding how the main components work makes PKI much easier to understand and shows why it remains important in modern cyber security.
What Is PKI in Cyber Security?
PKI stands for Public Key Infrastructure. It is a framework that manages digital certificates and cryptographic keys used to authenticate identities and secure electronic communication. Organizations use PKI to verify users, websites, servers, applications, and devices while ensuring that sensitive information can travel through networks with greater confidentiality and integrity.
The system relies heavily on asymmetric cryptography, which uses two mathematically related keys. One is called a public key and can be distributed openly, while the other is a private key that must remain protected. These keys support encryption, digital signatures, authentication, and other security processes that establish trust between communicating parties.
Understanding what is PKI in cyber security therefore means looking beyond encryption alone. PKI also defines how certificates are created, issued, validated, renewed, revoked, and trusted. It combines technology, policies, processes, and trusted organizations to create a structured system for managing digital identities securely.
How Does PKI Work?
PKI starts with cryptographic key pairs that include a public key and a private key. The public key can be shared with others, while the private key remains secret with its owner. Depending on the security process, these keys can be used to encrypt information, verify identities, or confirm that data has not been altered.
Digital certificates connect a public key to a specific identity, such as a website, organization, user, or device. A trusted Certificate Authority checks relevant information before issuing the certificate. When another system receives that certificate, it can examine who issued it and determine whether the certificate should be trusted.
This process creates a chain of trust. Instead of every internet user personally verifying every website or device, they rely on trusted Certificate Authorities and certificate validation mechanisms. PKI makes secure digital communication practical by providing a standardized way to establish confidence between systems that have never directly interacted before.
What Are Public and Private Keys?
Public and private keys are central to asymmetric cryptography. The public key is designed to be distributed, allowing other systems to use it for specific cryptographic operations. The private key is kept confidential because anyone who gains unauthorized access to it may be able to impersonate the legitimate owner or compromise protected communications.
One common concept involves encrypting information using a public key so that only the corresponding private key can decrypt it. This allows someone to send protected information without first sharing a secret encryption key. Asymmetric cryptography therefore solves important challenges related to secure key exchange across untrusted networks.
Private keys can also be used to create digital signatures. Other users can verify those signatures using the associated public key, helping confirm who signed the information and whether it was changed afterward. Protecting private keys is critical because the trust provided by PKI depends heavily on preventing unauthorized access to these secret credentials.
What Is a Digital Certificate in PKI?
A digital certificate is an electronic credential that connects an identity with a public key. It may contain information such as the certificate owner, issuing authority, public key, expiration date, and other technical details. Certificates allow systems to verify that a particular public key belongs to the entity claiming ownership.
Websites commonly use digital certificates to establish secure HTTPS connections. When your browser connects to a protected site, it checks the certificate and determines whether it was issued by a trusted authority. It also checks important details such as the domain name and certificate validity before treating the connection as trusted.
Certificates are not permanent. They usually have defined expiration dates and may need to be renewed periodically. They can also be revoked when a private key is compromised, an organization changes ownership, or the certificate should no longer be trusted for another security-related reason.
What Is a Certificate Authority?
A Certificate Authority, commonly abbreviated as CA, is a trusted organization or internal service responsible for issuing and managing digital certificates. Before issuing a certificate, the CA validates information about the requesting entity according to its procedures. The certificate is then digitally signed so other systems can verify that it came from the trusted authority.
Public Certificate Authorities issue certificates used by websites and other internet-facing services. Operating systems and browsers maintain lists of trusted root authorities, allowing them to recognize certificates issued within those trust chains. Organizations may also operate private CAs for employees, internal servers, devices, and applications.
Certificate Authorities play an important role because a compromised or poorly managed CA can undermine trust across many systems. Strong security controls are therefore required around certificate issuance, administrative access, and private signing keys. Protecting these systems helps prevent attackers from creating fraudulent certificates that appear legitimate.
How PKI Protects Websites and HTTPS Connections
When you visit an HTTPS website, your browser and the web server establish an encrypted connection using TLS. The server provides a digital certificate containing information about its identity and public key. Your browser checks whether the certificate is valid and whether it belongs to the website you intended to visit.
After successful verification, cryptographic processes allow the browser and server to establish protected communication. Information such as login credentials, payment details, personal data, and session information can then travel through the encrypted connection. This makes it significantly harder for someone monitoring network traffic to read the information directly.
PKI also reduces impersonation risks. Without certificate verification, an attacker might attempt to create a fake website and pretend to be a legitimate service. Certificate validation provides an additional method of checking identity, helping browsers recognize whether they are establishing connections with properly authenticated websites.
How PKI Supports Authentication
PKI can authenticate more than websites. Organizations can issue digital certificates to employees, computers, mobile devices, servers, and applications. These certificates provide a strong identity mechanism that can be used when users or machines attempt to access protected networks, systems, or services.
Certificate-based authentication can reduce dependence on passwords alone. Instead of asking only what a user knows, such as a password, systems can also verify whether the user or device possesses a trusted certificate and private key. This adds an additional layer of identity verification that can make unauthorized access more difficult.
Devices can also use certificates to authenticate automatically without requiring users to enter credentials repeatedly. This is particularly useful in large organizations managing thousands of machines. Proper certificate lifecycle management allows administrators to issue, renew, and revoke device identities as hardware enters or leaves the environment.
What Are Digital Signatures in PKI?
A digital signature provides a way to verify the authenticity and integrity of electronic information. The signer uses a private key as part of the signing process, and recipients can use the corresponding public key to validate the signature. This helps confirm that the information came from the expected signer.
Digital signatures can also reveal whether signed information has been modified. Even a small change to a signed document can cause signature verification to fail. This makes digital signatures useful for contracts, software packages, emails, business documents, and other information where integrity is important.
PKI provides the certificate system needed to connect the signing key to a trusted identity. Without reliable identity management, a technically valid signature would provide less confidence about who actually created it. Certificates make digital signatures more useful by supporting both cryptographic verification and identity trust.
How PKI Helps Protect Enterprise Devices
Modern organizations manage large numbers of laptops, servers, smartphones, network devices, and cloud workloads. PKI can provide each approved device with a unique digital identity. Security systems can then verify those identities before allowing devices to connect to wireless networks, VPNs, applications, or other protected resources.
Certificate-based device authentication is valuable because passwords can be stolen, reused, or shared. A protected private key stored on a managed device can provide stronger evidence that the connecting machine is legitimate. Organizations can also revoke the certificate if the device is stolen, retired, or considered compromised.
PKI works alongside other defensive technologies rather than replacing them. For example, understanding EDR in cyber security shows how endpoint monitoring can detect suspicious behavior after devices are authenticated. PKI establishes trusted identities, while endpoint security helps monitor what those trusted devices actually do.
What Is Certificate Lifecycle Management?
Digital certificates move through several stages during their lifetime. They are requested, validated, issued, installed, monitored, renewed, and eventually revoked or allowed to expire. Certificate lifecycle management refers to controlling these stages so that certificates remain valid, secure, and properly associated with the correct users, devices, or services.
Poor certificate management can cause both security and operational problems. An expired website certificate may generate browser warnings or interrupt access to important services. A forgotten certificate associated with a compromised private key can create a more serious problem because attackers may be able to abuse the trusted identity.
Large organizations often automate certificate lifecycle management because manually tracking thousands of certificates becomes difficult. Automation can help detect upcoming expirations, renew certificates, maintain inventories, and apply organizational policies consistently. Effective lifecycle management reduces outages while also improving the overall security of PKI environments.
What Are the Benefits of PKI?
One major benefit of PKI is secure identity verification. Certificates give users, devices, and applications a standardized method of proving their identity digitally. This supports secure websites, remote access, wireless authentication, encrypted email, software signing, and many other security use cases across both public and private networks.
PKI also provides strong encryption capabilities. Secure communication reduces the risk that sensitive information will be exposed when traveling across untrusted networks. Combined with digital signatures, PKI can support confidentiality, integrity, authentication, and stronger confidence that information came from the expected source.
Another advantage is scalability. Organizations can create policies for issuing and managing certificates across thousands of users and devices. When properly designed, PKI allows administrators to establish trust consistently without manually validating every connection, making it suitable for large enterprise and cloud environments.
What Are the Risks and Challenges of PKI?
PKI can become complex because certificates, keys, policies, and trust relationships must be managed carefully. Large organizations may operate thousands of certificates across websites, devices, servers, cloud services, and applications. Without accurate inventories, administrators can lose track of important certificates and create unnecessary security or availability risks.
Private key protection is another major challenge. If attackers steal a valuable private key, they may be able to impersonate a trusted system or misuse certificates. Hardware security modules, strong access controls, secure storage, and careful administrative practices can help reduce the likelihood of private key compromise.
Certificate expiration can also cause unexpected service interruptions. Applications may fail to connect when certificates are no longer valid, even when the underlying systems are operating normally. Monitoring expiration dates and automating renewal where appropriate can prevent these avoidable outages while maintaining secure certificate practices.
Best Practices for Managing PKI Securely
Organizations should maintain a complete inventory of certificates and cryptographic keys. Administrators need to know which systems use each certificate, when it expires, who owns it, and what purpose it serves. Good visibility makes it easier to identify unnecessary certificates and respond quickly when a security problem occurs.
Private keys should receive strong protection throughout their lifecycle. Access should be limited to authorized systems and users, while highly sensitive keys may require dedicated hardware-based protection. Organizations should also define procedures for replacing keys quickly when compromise is suspected instead of continuing to trust potentially exposed credentials.
Automation can improve reliability by managing renewals, deployment, and monitoring consistently. However, automated systems should still be audited and controlled carefully. A strong PKI program combines secure technology with clear policies, defined responsibilities, regular reviews, and incident-response procedures for handling compromised certificates or keys.
Conclusion
Understanding what is PKI in cyber security begins with recognizing PKI as a system for creating and managing digital trust. It uses public and private keys, digital certificates, Certificate Authorities, and security policies to authenticate identities, encrypt communications, and verify the integrity of digital information.
PKI supports many technologies people use every day, including HTTPS websites, secure remote access, device authentication, encrypted communication, and digital signatures. Its value comes from allowing systems to verify identities and establish protected connections even when the communicating parties have never previously interacted.
Strong PKI security depends on more than simply issuing certificates. Organizations must protect private keys, monitor expiration dates, revoke compromised certificates, and maintain accurate inventories. When these processes are managed effectively, PKI becomes a powerful foundation for protecting users, devices, applications, and digital communication.
FAQs
What does PKI stand for in cyber security?
PKI stands for Public Key Infrastructure. It is a framework of digital certificates, cryptographic keys, trusted authorities, policies, and processes used to secure communication and verify digital identities.
What is the main purpose of PKI?
The main purpose of PKI is to establish digital trust. It supports secure authentication, encryption, digital signatures, and identity verification between websites, users, devices, applications, and other systems.
What is a Certificate Authority in PKI?
A Certificate Authority is a trusted entity that validates identities and issues digitally signed certificates. Systems use those certificates to determine whether websites, users, devices, or services should be trusted.
What is the difference between a public key and a private key?
A public key can be distributed openly and used in cryptographic operations, while the related private key must remain secret. Together, they support encryption, authentication, and digital signatures.
Is PKI used for HTTPS websites?
Yes. HTTPS relies on digital certificates and public key technologies to authenticate websites and establish protected connections. This helps prevent interception, impersonation, and unauthorized reading of information exchanged between browsers and servers.