
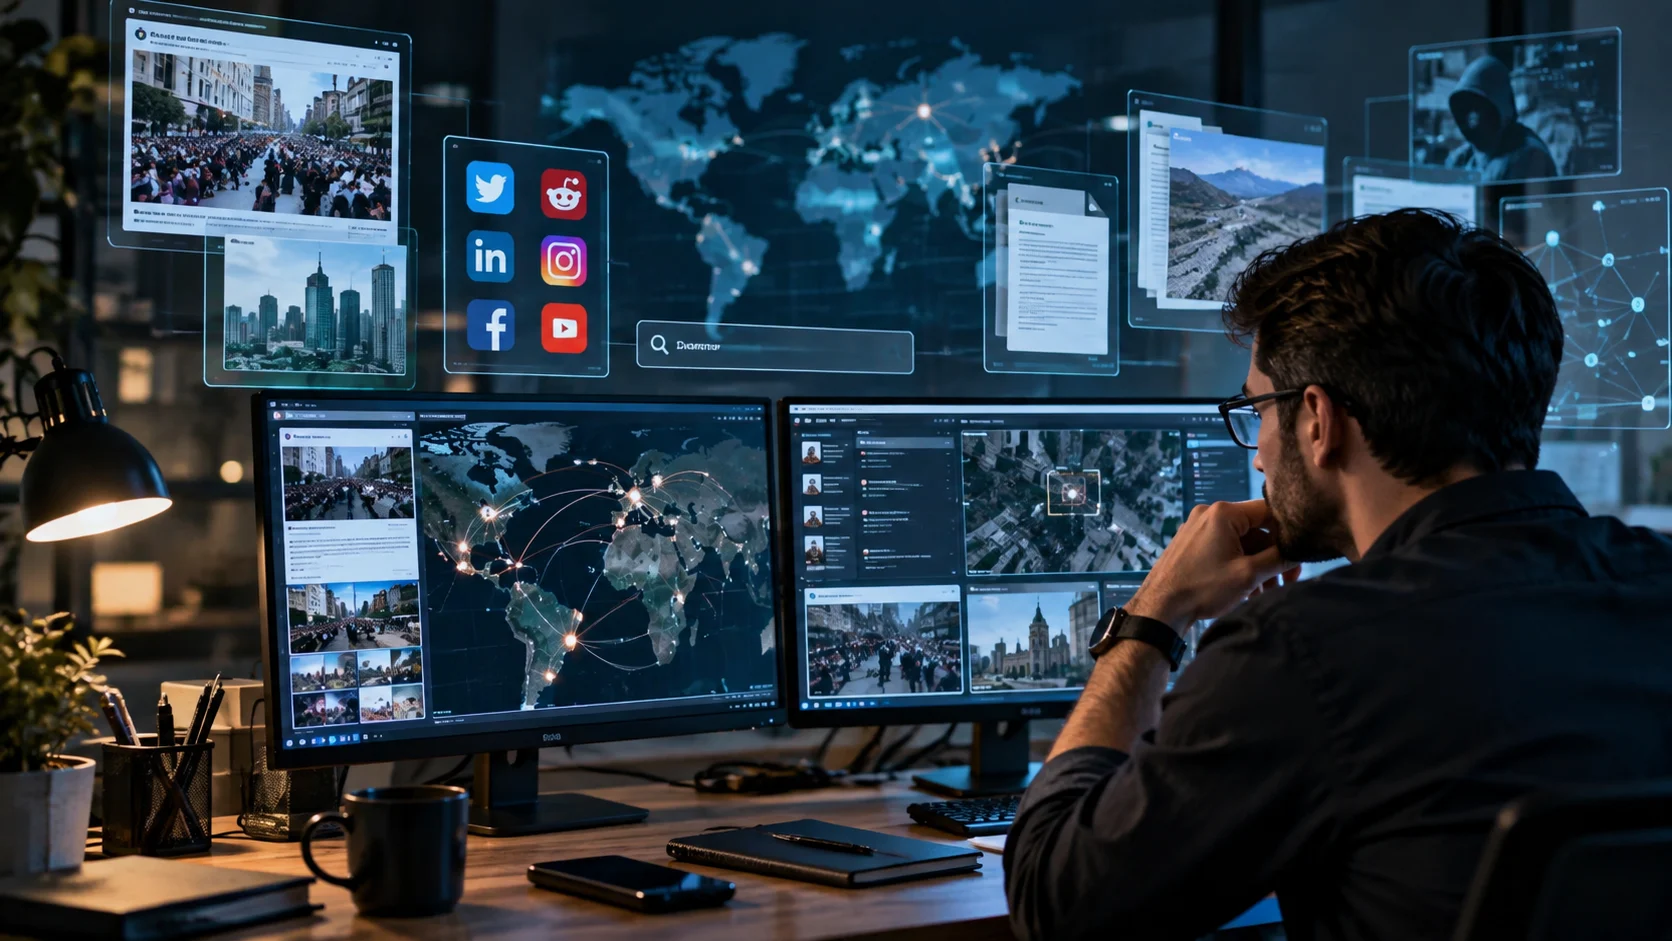
Open-source intelligence, commonly known as OSINT, plays an important role in modern cyber security because valuable information is often publicly available online. Security professionals use OSINT to research domains, IP addresses, companies, employees, technologies, threat actors, and exposed data. When used responsibly, this information can support investigations, threat intelligence, vulnerability assessments, and defensive security planning.
If you are asking what is OSINT in cyber security, OSINT means collecting and analyzing information from publicly accessible sources. These sources may include websites, social media platforms, public databases, search engines, technical records, news reports, code repositories, and online forums. The goal is not simply to collect information, but to identify useful patterns and security-related insights.
OSINT is used by both defenders and attackers, which makes understanding it especially important. Security teams can use public information to discover exposed assets and investigate threats, while criminals may use similar information for reconnaissance or social engineering. Strong cyber security therefore includes understanding what information is publicly visible and how it could potentially be used.
What Is OSINT in Cyber Security?
OSINT stands for Open-Source Intelligence. In cyber security, it refers to the process of finding, collecting, verifying, and analyzing information that is legally available from public sources. Security professionals use this information to understand potential threats, investigate suspicious activity, discover exposed infrastructure, and improve awareness of an organization’s external digital footprint.
Public information can come from many places. Domain registration records, search engines, social media profiles, company websites, job postings, public documents, technical databases, and developer platforms may all contain useful details. Individually, these pieces of information may appear harmless, but combining them can reveal important connections or security risks.
Understanding what is OSINT in cyber security also requires distinguishing collection from analysis. Simply gathering hundreds of public records does not automatically create intelligence. Analysts need to verify accuracy, remove irrelevant information, understand context, and determine how the findings relate to a specific security question or investigation.
Why Is OSINT Important in Cyber Security?
OSINT gives security teams visibility into information that exists outside their internal systems. Organizations often focus heavily on internal networks while forgetting that websites, cloud services, employee profiles, forgotten subdomains, and exposed documents can reveal useful information to outsiders. OSINT helps defenders see part of the organization from an external perspective.
This outside-in view is valuable for identifying potential weaknesses before attackers use them. A forgotten development server, old employee account, public configuration file, or leaked credential may create unnecessary exposure. Discovering such issues through public information allows security teams to investigate and reduce risk before an incident occurs.
OSINT can also support ongoing threat intelligence. Analysts may research malicious domains, suspicious IP addresses, attacker infrastructure, malware campaigns, and online discussions related to emerging threats. This additional context helps organizations understand whether a security alert is isolated or potentially connected to a larger attack campaign.
What Sources Are Used for OSINT?
Search engines are among the most familiar OSINT sources because they index large amounts of publicly accessible information. Security professionals may use advanced search techniques to locate documents, exposed pages, old website content, technical references, or public mentions of an organization. The value comes from searching carefully rather than simply entering broad keywords.
Social media and professional networking platforms can also reveal useful information. Public profiles may indicate job roles, technologies, office locations, company projects, or organizational changes. Security teams can use this information defensively to understand what details employees may unintentionally expose and how those details could support phishing or impersonation attempts.
Technical sources are especially useful for cyber security investigations. DNS records, certificate transparency logs, IP information, public code repositories, vulnerability databases, and internet-scanning services can reveal infrastructure and software details. Analysts often combine several of these sources to create a more complete picture of a system or threat.
How OSINT Is Used in Threat Intelligence
Threat intelligence teams use OSINT to learn about malicious infrastructure, attacker behavior, and emerging campaigns. Public reports, technical blogs, malware repositories, security forums, and domain data can provide useful indicators. Analysts can then compare these findings with internal alerts to determine whether their organization may be exposed to the same threat.
For example, an analyst investigating a suspicious domain may search for related IP addresses, certificates, registration history, and public reports. These connections can reveal whether the domain is associated with phishing, malware delivery, or other harmful activity. Additional context makes it easier to prioritize the investigation and decide what defensive actions may be appropriate.
OSINT can also help identify trends over time. If several sources report similar attacker techniques, tools, or targets, analysts may recognize a broader pattern. This information can support detection engineering, threat hunting, user awareness training, and security planning across the organization.
How OSINT Helps Cyber Security Analysts
Cyber security analysts often work with incomplete information during investigations. A security alert may contain only an IP address, email address, domain name, file hash, or username. OSINT allows analysts to research these indicators using public sources and gather additional context that may help determine whether the activity is suspicious.
For example, an unfamiliar IP address may be associated with a legitimate cloud provider or with infrastructure previously linked to malicious activity. Public information can help an analyst understand that difference more quickly. This makes OSINT useful for alert triage, incident response, phishing investigations, and threat hunting.
Anyone exploring defensive security careers may also want to understand the responsibilities and earning potential of the role. Learning about cyber security analyst salary alongside practical skills such as OSINT can provide useful context for how research, monitoring, and investigation fit into the profession.
OSINT for Digital Footprint Discovery
Every organization has a digital footprint that extends beyond its main website. Subdomains, cloud services, employee accounts, old documents, mobile applications, public code, and third-party services can all create additional exposure. OSINT techniques help security teams identify these assets and understand what information is visible externally.
This process is sometimes referred to as attack surface discovery. Security teams can search for forgotten systems, development environments, expired services, or public technical information that may create risk. Finding these assets is important because attackers frequently look for overlooked systems that receive less monitoring than major production environments.
Digital footprint discovery should be continuous rather than performed once. Organizations regularly launch new systems, change vendors, hire employees, and migrate infrastructure. OSINT-based monitoring can help defenders notice new exposures and maintain a more accurate picture of what external users can see.
How OSINT Supports Phishing Investigations
Phishing investigations often begin with limited evidence, such as a suspicious email address, sender domain, link, or website. OSINT can help analysts research these details and determine whether they are associated with previous malicious activity. Domain age, hosting information, certificates, and public reports may provide useful clues.
Analysts can also examine how closely a suspicious site resembles a legitimate company. Attackers frequently create lookalike domains or fake login pages designed to steal credentials. Public information about domain registration and infrastructure can help defenders identify patterns that support a phishing classification.
OSINT is also useful for understanding how attackers collect information before creating targeted phishing messages. Public employee names, job titles, company projects, and organizational relationships can help criminals make messages appear more convincing. Security awareness programs can use this knowledge to teach employees why oversharing professional information may increase social engineering risk.
OSINT and Vulnerability Management
OSINT can support vulnerability management by helping security teams discover publicly exposed technologies and services. Information about software versions, server technologies, cloud platforms, and internet-facing systems may sometimes be available through public records or scanning services. This gives defenders another way to identify assets that require security review.
Once exposed technologies are identified, teams can compare them with known vulnerabilities and vendor security information. The goal is not to exploit systems, but to determine whether public-facing assets may require updates, configuration changes, or further assessment. This approach can complement internal vulnerability scanning and asset management.
OSINT can also help locate public discussions about newly discovered vulnerabilities. Security researchers, vendors, and security organizations may share technical details, affected products, and mitigation guidance. Monitoring these public sources helps defenders understand whether a newly announced issue is relevant to their environment.
What Tools Are Commonly Used for OSINT?
OSINT tools vary depending on the type of information being investigated. Search engines, DNS lookup platforms, certificate databases, internet scanners, archive services, social media search tools, and public code repositories can all provide useful information. Analysts usually combine several sources rather than depending entirely on one tool.
Automation can make OSINT research faster when large numbers of indicators need to be checked. Scripts and specialized platforms can collect domain information, resolve IP addresses, search public data, and organize results. However, automated collection still requires human review because public information may be outdated, incomplete, duplicated, or inaccurate.
The best OSINT professionals are not defined by how many tools they know. They understand how to ask useful questions, verify information, compare multiple sources, and recognize misleading results. Tools make research faster, but analytical thinking determines whether the collected information becomes meaningful intelligence.
What Are the Limitations of OSINT?
Public information is not always accurate. Websites may contain outdated details, social media accounts can be fake, and public databases may include incomplete records. Analysts should therefore verify important findings through multiple sources whenever possible instead of treating the first result as unquestionable evidence.
OSINT can also generate enormous amounts of information. Without a clear research question, analysts can spend hours collecting details that do not improve the investigation. Effective OSINT work begins with defining what needs to be discovered and then focusing on sources most likely to provide relevant answers.
Another limitation is visibility. Some useful information may simply not be public, while other data may disappear or become restricted over time. OSINT therefore works best as one part of a larger investigation alongside internal logs, endpoint data, network activity, identity records, and other authorized security information.
Is OSINT Legal and Ethical?
OSINT generally focuses on information that is publicly accessible, but public availability does not mean information can be used without responsibility. Security professionals should respect privacy, organizational policies, applicable laws, and the purpose of the investigation. Ethical research avoids unnecessary collection of personal information that is unrelated to a legitimate security objective.
Analysts should also avoid crossing from passive research into unauthorized access. Viewing public records is different from bypassing authentication, exploiting vulnerabilities, or accessing systems without permission. Cyber security teams should clearly understand their legal authorization before moving beyond publicly available information.
Responsible OSINT also involves secure handling of collected data. Research may contain employee names, email addresses, infrastructure details, or security-related information that could become sensitive when combined. Organizations should store findings carefully, limit access appropriately, and avoid sharing unnecessary personal or operational information.
How to Learn OSINT for Cyber Security
Beginners should start by learning how the internet and common technical systems work. Understanding DNS, domains, IP addresses, websites, certificates, email, social media, and search engines makes OSINT findings easier to interpret. Without this foundation, learners may collect information without understanding why it matters.
Next, practice with safe and legal research exercises. You can study your own digital footprint, analyze intentionally created training examples, research public organizations, or work with cyber security labs designed for learning. These exercises help you develop search techniques, verification habits, and analytical thinking without crossing legal or ethical boundaries.
Finally, learn how to document findings clearly. Good OSINT reports explain what was found, where the information came from, how confident the analyst is, and why the result matters. Clear documentation makes research more useful during investigations and helps other security professionals verify the analysis.
Conclusion
Understanding what is OSINT in cyber security begins with recognizing that valuable security information often exists in public sources. OSINT allows professionals to collect and analyze data from websites, technical records, social platforms, search engines, public databases, and other accessible sources.
Security teams use OSINT for threat intelligence, phishing investigations, digital footprint discovery, vulnerability management, and incident response. It can provide context that internal security alerts may not contain and help defenders understand how their organization appears from the outside.
OSINT is most effective when combined with careful verification, ethical research, and strong analytical skills. Public information can be incomplete or misleading, so analysts should compare multiple sources and remain focused on clear security objectives. Used responsibly, OSINT becomes a valuable part of modern cyber security investigations.
FAQs
What does OSINT stand for in cyber security?
OSINT stands for Open-Source Intelligence. It involves collecting and analyzing publicly accessible information to support cyber security research, threat intelligence, investigations, vulnerability management, and digital footprint discovery.
Is OSINT the same as hacking?
No. OSINT focuses on publicly available information and does not require unauthorized access to systems. Hacking may involve technical interaction with systems, while OSINT primarily involves research and analysis.
What information can OSINT find?
OSINT can reveal domains, IP addresses, public documents, social media profiles, exposed services, technical records, company information, certificates, and other publicly accessible data relevant to an investigation.
Do cyber security analysts use OSINT?
Yes. Analysts use OSINT to research suspicious indicators, investigate phishing, understand attacker infrastructure, discover exposed assets, and add context to alerts generated by internal security tools.
Is OSINT difficult to learn?
OSINT is approachable for beginners, but strong research and verification skills take practice. Learning networking, internet technologies, search techniques, and cyber security fundamentals makes OSINT investigations easier and more accurate.