
What Is BIOS? What It Does & How It Works
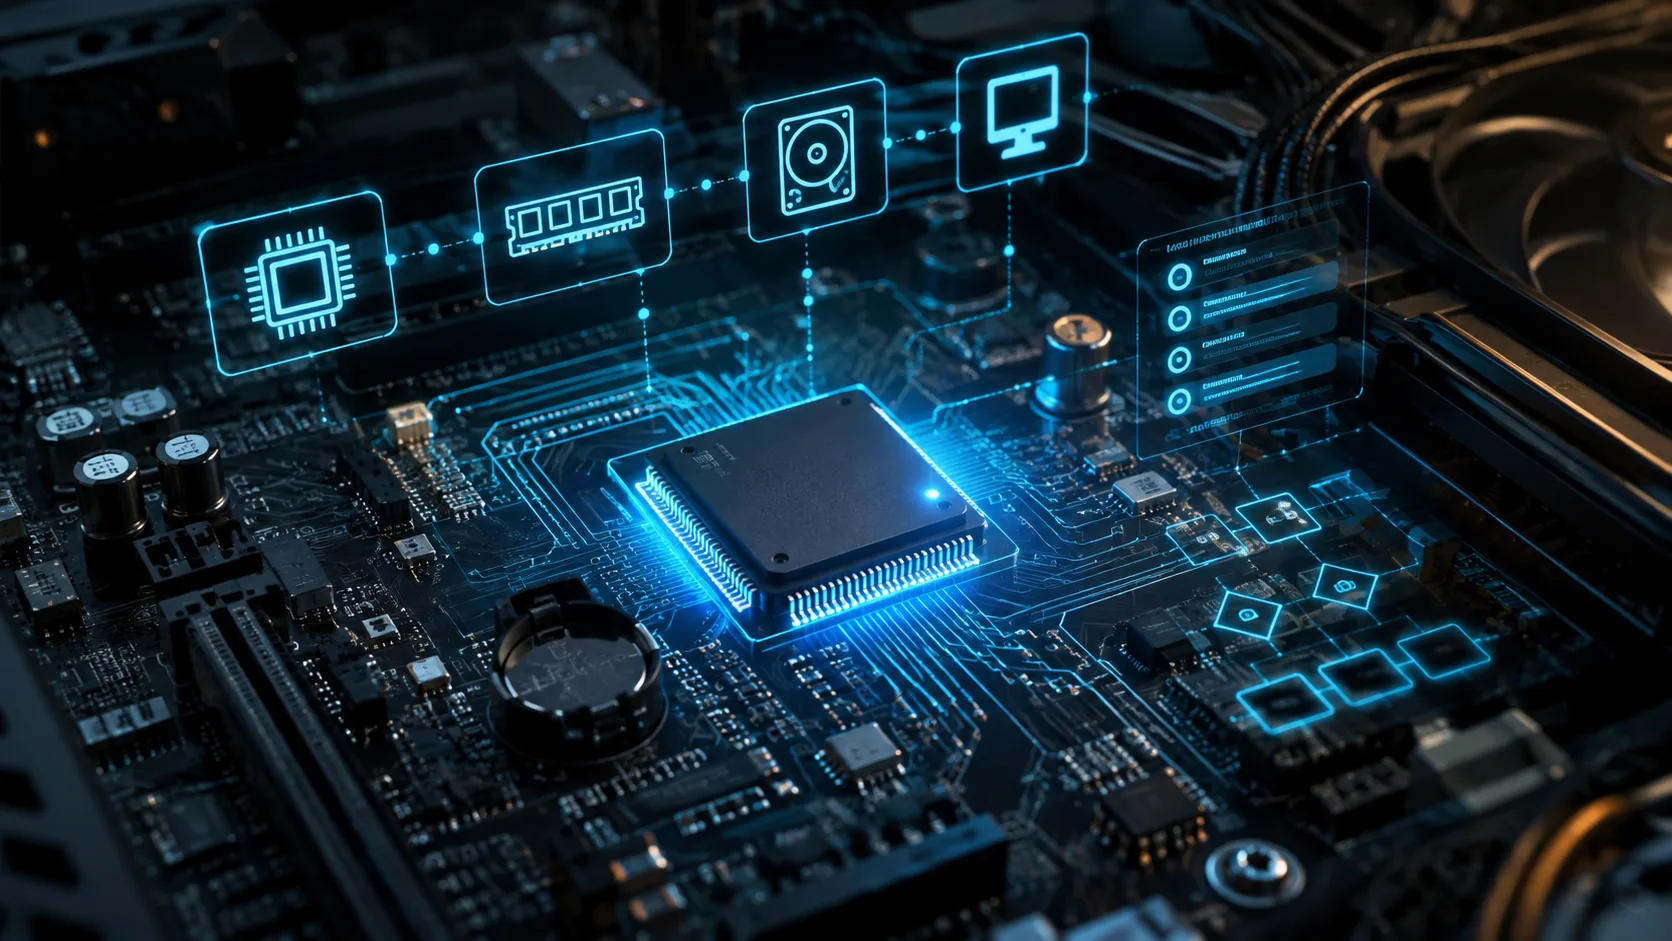
BIOS is one of those computer terms most people have heard but may never think about until a PC refuses to start, a new drive needs to be selected, or a hardware setting must be changed. The term stands for Basic Input/Output System, and traditionally it describes firmware stored on a computer’s motherboard that begins working as soon as the machine powers on. Before Windows, Linux, or another operating system can load, the firmware checks important hardware and prepares the computer for startup. It also provides configuration options for components such as storage devices, processors, memory, and boot drives. Although modern computers usually rely on UEFI rather than traditional BIOS, people still commonly call the firmware setup screen “the BIOS.” Understanding what BIOS does can make computer startup, troubleshooting, hardware upgrades, and system configuration much easier to understand.
Modern firmware has become considerably more advanced than the original BIOS found in older personal computers, but its fundamental purpose remains similar. The computer needs a reliable layer of software that can operate before the main operating system becomes available. This firmware identifies essential hardware, performs startup checks, applies configuration settings, and determines which device should be used to begin loading the operating system. It can also provide security features, hardware monitoring, virtualization settings, fan controls, and firmware update tools. Because these functions operate at a very low level, incorrect settings can sometimes prevent a computer from booting correctly. This guide explains BIOS meaning, how the BIOS works, how it differs from UEFI, what settings it contains, and when ordinary computer users may need to access it.
What Is BIOS?
BIOS stands for Basic Input/Output System and traditionally refers to firmware stored on a chip located on a computer motherboard. Firmware is software that is closely connected to hardware and remains available even when the computer’s main storage drive contains no operating system. When a computer is switched on, BIOS is among the first pieces of software executed by the processor. Its job is to prepare essential hardware so that the computer can continue through the startup process. It identifies important components, performs basic checks, loads stored configuration values, and searches for a bootable device. Once an operating system begins loading, many of the BIOS startup responsibilities are no longer needed until the computer is restarted.
The original BIOS concept became widely associated with IBM-compatible personal computers and remained a standard part of PC architecture for decades. Traditional BIOS firmware was designed for hardware environments that were far simpler than modern computers containing large storage drives, advanced processors, high-speed memory, graphics hardware, wireless devices, and sophisticated security features. As personal computing evolved, the limitations of legacy BIOS became increasingly noticeable. Manufacturers eventually moved toward more capable firmware systems, particularly the Unified Extensible Firmware Interface, commonly abbreviated as UEFI. Despite that transition, the word BIOS remains deeply embedded in everyday computer language. Users, repair technicians, hardware manufacturers, and even software documentation may still say “enter the BIOS” when they actually mean opening a modern UEFI firmware configuration interface.
BIOS should not be confused with an operating system because the two serve different purposes and operate at different stages. An operating system such as Windows manages applications, files, users, networking, security, devices, and everyday interaction after the computer has completed its initial startup sequence. BIOS or UEFI works earlier and provides the basic environment necessary for that operating system to begin loading. It can operate even when Windows has been deleted or a storage drive has been removed because the firmware is stored separately on the motherboard. This separation is why users can often enter the BIOS setup utility even when the operating system cannot boot. It also makes firmware an important diagnostic layer when troubleshooting startup and hardware recognition problems.
The firmware itself is generally stored in nonvolatile flash memory, meaning the code remains available when the computer is switched off. Configuration settings have traditionally been associated with CMOS memory, although modern systems may store firmware settings using technologies that differ from older CMOS implementations. A small motherboard battery helps maintain certain information, particularly the real-time clock and firmware configuration on many systems. When that battery becomes weak, users may notice incorrect system time or firmware settings returning to defaults. However, the BIOS program and the configurable settings are not exactly the same thing. The BIOS is firmware code, while BIOS settings are values that influence how that firmware manages hardware and startup behavior.
The simplest way to understand BIOS is to imagine it as the computer’s startup coordinator. When power reaches the system, the operating system is not immediately ready to control the machine because important hardware must first be identified and prepared. BIOS or UEFI handles that early coordination and provides the bridge between powered hardware and the software that will eventually take control. It checks whether the system has the resources necessary to start, determines where boot information should come from, and hands control to the next stage of the startup process. Without working motherboard firmware, a typical PC cannot proceed normally into its operating system. That makes BIOS a small but essential part of the overall computing architecture.
What Does BIOS Do?
One of the primary functions of BIOS is hardware initialization, which means preparing important components so they can operate correctly during startup. The firmware communicates with the processor, system memory, storage controllers, graphics hardware, keyboard interfaces, and other devices required during the early boot process. It determines which hardware is present and applies configuration information needed before higher-level software takes over. Some devices have their own firmware or initialization procedures, while others depend heavily on motherboard firmware during this stage. The exact sequence varies between computer manufacturers and hardware platforms. However, the overall objective remains the same: transform a collection of powered components into a usable system that is ready to load software.
BIOS also performs a startup diagnostic process commonly known as the Power-On Self-Test, or POST. During POST, the firmware checks whether essential hardware appears to be functioning well enough for the computer to continue booting. Memory, processor initialization, graphics output, keyboard availability, storage interfaces, and other critical components may be examined depending on the system. If the firmware detects a serious problem, startup may stop before the operating system loads. Older systems often communicated problems through combinations of audible beep codes, while modern motherboards may use diagnostic LEDs, display codes, or on-screen error messages. POST therefore provides an important first layer of troubleshooting when a computer powers on but cannot reach its operating system.
Another major responsibility involves determining how the computer should boot. BIOS or UEFI maintains a boot order that tells the system which available devices should be checked for startup information. A computer might be configured to check an internal SSD first, followed by USB storage, optical media, or network boot services. Changing this order is useful when installing an operating system from a USB drive or starting diagnostic software from external media. Modern UEFI systems often store specific boot entries rather than simply searching devices in a traditional sequence. The underlying principle is still similar because the firmware must locate a valid environment capable of continuing the startup process.
BIOS also gives users and technicians access to low-level system configuration settings. Depending on the motherboard, these settings may include processor options, memory profiles, storage controller modes, integrated devices, virtualization support, fan behavior, system clock settings, power management, and security controls. Gaming and enthusiast motherboards may provide extensive options for CPU tuning, memory timings, voltages, fan curves, and performance profiles. Business computers may emphasize features such as firmware passwords, Trusted Platform Module settings, Secure Boot, remote management, and device restrictions. Laptop firmware interfaces are often simpler because manufacturers tightly control hardware configurations. These settings allow firmware behavior to be adjusted without requiring access to the operating system.
A further function of modern firmware is providing a trusted foundation for system security and operating system startup. UEFI platforms can support features such as Secure Boot, which helps prevent unauthorized boot software from loading when the platform is configured appropriately. Firmware may also interact with TPM hardware or firmware-based security modules used by modern operating systems for encryption and identity protection. Some systems provide password controls that can restrict firmware configuration or startup access. Because firmware operates before the operating system, attackers who compromise it could potentially gain unusually deep control over a computer. For this reason, firmware security, signed updates, platform protections, and carefully managed BIOS settings have become increasingly important parts of modern computer security.
How Does BIOS Work When You Turn On a Computer?
The BIOS process begins almost immediately after the user presses the computer’s power button. Electrical power is supplied to the motherboard and connected hardware, while the processor begins executing instructions from a predefined startup location associated with the system firmware. At this moment, Windows or another operating system has not started, and even many hardware components are not yet fully initialized. The firmware establishes the earliest working environment and begins preparing the platform for further operation. It loads essential configuration information and starts communicating with critical motherboard components. Although this stage normally lasts only a few seconds on modern computers, a large amount of low-level coordination occurs before the familiar operating system logo appears.
Once basic processor operation is established, the firmware begins checking and initializing system memory and other essential hardware. Memory initialization is particularly important because normal software cannot run effectively until usable RAM has been prepared. Modern systems may perform memory training, especially when high-performance DDR memory profiles or sophisticated memory controllers are involved. The firmware also initializes graphics output so that diagnostic information or a manufacturer logo can appear on the display. Storage controllers and other important interfaces are prepared during this sequence as well. If the firmware cannot successfully initialize critical hardware, the boot process may stop and produce diagnostic information before any attempt is made to load the operating system.
After hardware initialization, BIOS or UEFI evaluates configured boot information to determine what should happen next. On a traditional legacy BIOS system, firmware typically searches a boot device and loads a small piece of code from a boot sector into memory. That code then continues the process of finding and loading the operating system. Modern UEFI systems use a more sophisticated approach involving files stored on an EFI System Partition. The firmware can directly execute compatible boot applications, such as Windows Boot Manager or a Linux bootloader. This design provides more flexibility than traditional BIOS booting and supports modern storage, security, and system management requirements.
Once the appropriate bootloader has started, control gradually shifts away from the motherboard firmware and toward the operating system. The bootloader locates important operating system components, loads them into memory, and prepares the environment needed for the operating system kernel. Windows, Linux, or another system then detects devices, loads drivers, starts background services, and eventually presents the user with a login screen or desktop. Firmware is not necessarily inactive after this handoff, because modern operating systems can still interact with firmware services and platform information. However, the operating system now controls most of the computer’s everyday activity. The BIOS or UEFI has successfully completed its most visible responsibility: enabling the machine to transition from powered hardware into a working software environment.
The entire startup sequence can feel nearly instantaneous on a modern computer with a fast SSD and optimized firmware settings. Features such as Fast Boot can reduce initialization time by skipping or shortening certain checks when the system configuration has not changed. This speed sometimes makes accessing the firmware setup screen difficult because the window for pressing the required key may be extremely short. Operating systems therefore provide additional ways to restart directly into UEFI settings on supported computers. Faster startup does not mean the firmware has disappeared; it simply means its operations have become more efficient and less visible. Every normal boot still depends on firmware successfully preparing the platform before the operating system can take control.
BIOS vs UEFI: What Is the Difference?
Traditional BIOS and UEFI serve broadly similar purposes, but UEFI is the modern firmware standard used by most contemporary PCs. Legacy BIOS was designed around older PC hardware and includes architectural limitations that became increasingly restrictive as computers evolved. UEFI provides a more flexible environment capable of supporting modern storage devices, graphical interfaces, security features, networking capabilities, and extensible firmware applications. Many users continue using the word BIOS because it is familiar and because manufacturers often describe firmware settings with labels such as BIOS Setup or BIOS Update. Technically, however, a newly purchased Windows computer is far more likely to use UEFI firmware. Knowing this distinction helps explain why modern startup options sometimes behave differently from older BIOS guides.
One major difference involves how the firmware works with storage devices and partition structures. Legacy BIOS is strongly associated with the Master Boot Record, or MBR, partitioning method, while UEFI commonly works with the GUID Partition Table, known as GPT. GPT is better suited to modern storage requirements and avoids several important limitations associated with MBR. UEFI systems can boot from large drives using modern partition layouts that legacy BIOS may not support in the same way. The exact capabilities depend on motherboard firmware and operating system configuration, so compatibility modes can sometimes complicate the picture. Nevertheless, GPT and native UEFI booting have become standard choices for current Windows PCs and many other modern computer systems.
UEFI can also provide a more sophisticated firmware interface than traditional BIOS. Older BIOS setup utilities were typically keyboard-driven screens containing text menus and relatively basic configuration controls. Modern UEFI interfaces may support mouse input, higher-resolution graphics, built-in screenshots, fan control dashboards, storage utilities, firmware update tools, hardware monitoring, and detailed performance settings. Enthusiast motherboards sometimes offer both simplified and advanced interface modes to accommodate beginners and experienced users. These graphical improvements do not fundamentally change the firmware’s core startup responsibility. They do, however, make configuration easier and allow motherboard manufacturers to provide capabilities that would have been difficult to implement in traditional BIOS environments.
Security represents another important difference because UEFI supports modern mechanisms such as Secure Boot. Secure Boot can verify the digital signatures of boot software and help prevent unauthorized or malicious code from replacing trusted startup components. This capability has become increasingly relevant as operating systems place greater emphasis on hardware-backed security. Modern UEFI firmware may also integrate closely with TPM functionality, measured boot processes, firmware protection technologies, and operating system security requirements. Legacy BIOS was created long before many of these threats and security models existed. As a result, UEFI provides a more suitable foundation for current computers that must protect not only files and applications but also the earliest stages of system startup.
Despite its advantages, UEFI is not simply “BIOS but faster,” and users can encounter compatibility issues when changing between legacy and UEFI boot modes. An operating system installed using one boot configuration may fail to start if firmware settings are changed incorrectly afterward. Older expansion hardware or operating systems may also depend on legacy compatibility features that newer devices no longer provide. For most users, the safest approach is to leave firmware boot mode unchanged unless there is a clear technical reason to modify it. When following online instructions, users should also check whether a guide discusses true legacy BIOS or modern UEFI. The distinction affects partitioning, Secure Boot, boot entries, operating system installation, and several troubleshooting procedures.
What Settings Can You Change in BIOS?
Boot settings are among the most commonly changed options inside BIOS or UEFI because they control how the computer searches for operating systems and startup tools. Users may adjust boot priority when installing Windows from a USB drive, running a recovery environment, launching hardware diagnostics, or starting an alternative operating system. Modern firmware may provide both a permanent boot order and a temporary boot menu that applies only to the next startup. Using the temporary boot menu is often safer when no permanent configuration change is necessary. Users may also see entries such as Windows Boot Manager alongside individual drives. Changing boot settings without understanding these entries can make a working operating system appear unavailable even though its files remain intact.
Processor and memory settings can also appear in firmware, particularly on desktop motherboards designed for enthusiasts or professional workstations. Options may include CPU virtualization support, performance limits, processor boost behavior, memory frequency, memory timings, and predefined XMP or EXPO memory profiles. Enabling a supported memory profile can allow compatible RAM to operate at its advertised performance settings rather than conservative defaults. Overclocking controls may let advanced users adjust processor frequency, voltage, and power behavior. These changes can improve performance but may also increase heat, instability, or component stress when configured improperly. Beginners should generally avoid changing voltage and advanced timing values unless they understand the hardware consequences and have a specific reason for doing so.
Storage configuration is another important category found in many firmware interfaces. Users may encounter settings related to SATA controllers, NVMe devices, RAID configurations, storage detection, and drive security. Changing controller modes after an operating system has already been installed can sometimes prevent that operating system from starting because the required drivers or configuration may differ. Firmware may also allow users to view whether drives are detected correctly, which is useful when troubleshooting missing SSDs or hard disks. Modern UEFI environments can provide built-in NVMe information and storage management utilities. However, not every detected storage device will necessarily appear as an independent boot choice if booting depends on a specific UEFI bootloader entry.
Security settings have become increasingly prominent in modern BIOS and UEFI interfaces. Secure Boot can often be enabled or disabled, while TPM-related options may appear under names such as TPM, Intel PTT, AMD fTPM, or security device support. Firmware can also provide administrator passwords, startup passwords, drive security features, and restrictions on external boot devices. Organizations may use these controls to protect business computers from unauthorized configuration changes. Certain operating system features, including some encryption and security capabilities, may depend on appropriate firmware settings. Because disabling or clearing security features can affect encryption keys or operating system access, users should understand the consequences before changing TPM, Secure Boot, or firmware password settings.
Hardware monitoring and cooling controls are also common, especially on modern desktop motherboards. The firmware may display processor temperature, motherboard temperature, fan speeds, voltages, and information about connected cooling devices. Fan control menus can allow users to create curves that change cooling speed based on temperature. A properly configured curve can balance noise and cooling performance, while an aggressive silent configuration could potentially allow temperatures to rise unnecessarily. Some firmware interfaces also provide warnings if a CPU fan is not detected. These features make BIOS useful not only for startup configuration but also for diagnosing cooling issues before the operating system or manufacturer utilities become available.
How to Enter BIOS or UEFI Settings
The traditional way to enter BIOS or UEFI is to press a specific keyboard key immediately after turning on or restarting the computer. Common keys include Delete, F2, F10, F12, or Esc, although the correct key depends on the motherboard or computer manufacturer. A startup message may briefly display instructions such as “Press F2 to enter Setup” before the operating system begins loading. Because modern computers start quickly, users may need to begin pressing the key soon after powering on the machine. Repeatedly pressing the appropriate key is often more reliable than attempting to time one exact keystroke. Laptop keyboards may also require the Fn key depending on how the manufacturer configures function keys.
Windows provides another method for opening UEFI settings on supported computers, which can be useful when the startup sequence is too fast for manual key presses. Through advanced startup options, Windows can restart the computer into a recovery environment containing troubleshooting and firmware-related choices. Selecting the UEFI firmware settings option instructs the system to restart directly into the firmware interface. The exact menu path may vary slightly between Windows versions and updates, but the feature is generally available on properly configured UEFI systems. This approach avoids repeatedly restarting the PC while attempting to press the correct key. If the firmware option does not appear, the system may use a different configuration or may not expose that function through Windows.
Once the firmware interface opens, users should navigate carefully because changes can affect startup, security, performance, and hardware behavior. Most interfaces separate settings into categories such as Main, Boot, Advanced, Security, Power, and Exit, although naming varies significantly between manufacturers. Modern UEFI interfaces may also offer an Easy Mode that displays important information without exposing every advanced option. Before changing a setting, it is useful to record its original value or take a photograph so the previous configuration can be restored if necessary. Some firmware interfaces support screenshots saved to USB storage. Users should avoid modifying several unfamiliar options simultaneously because doing so makes troubleshooting much harder if the computer later behaves unexpectedly.
Saving changes usually requires selecting an option such as Save & Exit or pressing a designated shortcut key. The firmware may show a summary of modified values before restarting the computer, giving the user an opportunity to review what changed. Choosing Exit Without Saving discards adjustments made during the session and restores the previous configuration. Many systems also provide a Load Optimized Defaults or Restore Defaults option that returns firmware settings to manufacturer-recommended values. Restoring defaults can sometimes help when incorrect configuration prevents normal startup, although it may also remove intentional settings such as custom boot order or memory profiles. For that reason, default restoration should be treated as a troubleshooting step rather than an automatic solution for every problem.
Users who cannot access the firmware because the computer does not display anything may be dealing with a hardware or configuration issue rather than simply pressing the wrong key. Problems with memory installation, graphics hardware, monitor connections, power delivery, processor support, or corrupted firmware can prevent the normal setup screen from appearing. Desktop motherboards may provide diagnostic LEDs or error codes that help identify the stage where startup fails. Clearing firmware settings can sometimes resolve configuration-related boot problems, but the proper procedure depends on the motherboard. Hardware manuals are especially useful in this situation because jumper locations, reset buttons, supported processors, and diagnostic indicators differ between systems. Randomly removing components or shorting motherboard pins without clear instructions can create additional problems.
What Is a BIOS Update and When Do You Need One?
A BIOS update is a firmware update provided by a computer or motherboard manufacturer to replace or modify the code stored in the firmware chip. Manufacturers release updates for reasons such as processor compatibility, memory stability, security improvements, hardware bug fixes, device support, and overall system reliability. On modern systems, these updates are often technically UEFI firmware updates even when vendors continue calling them BIOS updates. Firmware versions are specific to particular motherboard or computer models, so installing the wrong file can cause serious problems. Users should therefore confirm the exact model and revision before beginning an update. Firmware updating deserves more caution than installing an ordinary application because failed firmware can prevent the computer from starting.
Not every available BIOS update needs to be installed immediately simply because a newer version exists. If a computer is operating correctly and the update does not address anything relevant, some users may reasonably leave the existing version unchanged. On the other hand, an update can be important when it contains a significant security fix, resolves a known stability problem, supports a newly installed processor, or addresses compatibility with specific memory or storage hardware. Laptop and prebuilt computer manufacturers may also distribute firmware updates through their own support utilities or operating system update mechanisms. The release notes are especially useful because they explain what changed. Reviewing those notes helps users decide whether the potential benefit justifies performing the update.
Firmware can be updated through several methods depending on the manufacturer. Many motherboards include a built-in flashing utility that reads a firmware file from a USB drive, allowing the process to occur directly inside the UEFI environment. Some vendors provide Windows-based tools, although firmware-level update utilities are often preferred by experienced users because fewer operating system processes can interfere. Certain modern motherboards include dedicated BIOS Flashback functionality that can update firmware from USB even when a supported processor is not installed or normal startup is unavailable. Prebuilt laptops and desktops may use manufacturer-specific update packages. Whatever method is used, users should follow instructions designed specifically for their exact hardware rather than relying on generic procedures.
The most important requirement during a firmware update is preventing interruption while new firmware is being written. A power failure or forced shutdown at the wrong moment can leave the firmware incomplete and make the computer unable to boot. Desktop users in locations with unreliable electricity may benefit from using an uninterruptible power supply when performing important firmware updates. Laptop users should generally connect the AC adapter and ensure the battery has sufficient charge before beginning. The update process may restart the computer several times or leave the display blank temporarily, which does not necessarily indicate failure. Users should not interrupt the process simply because it takes longer than expected unless official instructions clearly indicate that something has gone wrong.
After an update, some firmware settings may return to defaults, and the computer may perform a longer first startup while retraining memory or reconfiguring hardware. Users who previously enabled memory profiles, virtualization, custom fan curves, specific boot settings, or other configuration options may need to review them again. Security-related settings should also be checked carefully, particularly on systems using encryption or specialized boot configurations. Occasionally, firmware updates introduce new bugs or compatibility issues, although manufacturers may release later revisions to correct them. Some motherboards support firmware recovery or rollback, while others restrict downgrading for security or technical reasons. Keeping a record of important settings before updating can make post-update configuration significantly easier.
Common BIOS Problems and How to Troubleshoot Them
A computer that powers on but fails to reach the operating system can sometimes have a firmware-related configuration problem. An incorrect boot order may cause the machine to search for an empty USB drive, disconnected storage device, or invalid network boot entry instead of the operating system. Opening the boot menu and selecting the correct Windows Boot Manager or system drive may immediately identify the cause. If the expected drive does not appear at all, the issue could involve storage hardware, cables, controller configuration, or drive failure rather than the boot order itself. Users should distinguish between a drive that is detected but not bootable and one that firmware cannot detect. Those two situations require different troubleshooting approaches.
Incorrect firmware settings can also cause instability after users experiment with CPU overclocking, memory profiles, voltages, or advanced hardware options. Symptoms may include repeated restarts, failure to complete POST, random crashes, or a computer that switches on without producing a normal display. Returning the relevant settings to their previous values may solve the problem if firmware setup remains accessible. When the computer cannot reach setup, clearing the firmware configuration may restore safe default values. Desktop motherboards may provide a Clear CMOS button, jumper, or other reset procedure described in their manuals. Because the exact method varies, users should follow manufacturer instructions rather than assuming that every motherboard resets in the same way.
A weak CMOS or motherboard battery can cause another recognizable group of problems on older or heavily used systems. The computer may repeatedly forget the correct date and time, lose certain configuration settings, or display checksum-related warnings during startup. Desktop motherboards commonly use a replaceable coin-cell battery, although laptops and specialized systems may use different arrangements. Replacing the battery can resolve these symptoms when the underlying firmware and hardware are otherwise healthy. However, incorrect time can also result from operating system settings, synchronization problems, or other causes. Users should therefore confirm that firmware settings are actually being lost before assuming the battery needs replacement.
Failed or corrupted firmware is a more serious problem because the computer may no longer complete the earliest stages of startup. Symptoms can include a black screen, repeated recovery attempts, firmware error indicators, or failure to initialize hardware that previously worked correctly. Some modern motherboards contain backup firmware, USB recovery procedures, or BIOS Flashback features that can restore firmware without normal startup. Prebuilt computers may provide manufacturer-specific recovery methods using special key combinations or prepared USB drives. Recovery procedures must match the exact model because firmware files and flashing methods are hardware-specific. If no recovery function exists, professional repair or motherboard replacement may be necessary in severe cases.
Not every startup failure should be blamed on BIOS simply because the operating system does not load. Faulty RAM, defective storage, loose cables, incompatible processors, graphics problems, power supply issues, damaged motherboards, and corrupted operating system files can produce similar symptoms. Effective troubleshooting begins by identifying the stage at which startup stops. If the computer cannot complete POST, hardware or firmware initialization is more likely to be involved. If firmware detects the drive but the operating system displays repair errors, the problem may exist later in the boot process. Separating power-on, POST, bootloader, and operating system stages makes diagnosis more systematic and helps avoid unnecessary firmware changes.
Why BIOS Security Matters on Modern Computers
Firmware security matters because BIOS or UEFI operates before the main operating system and has unusually deep access to the computer. Malware that successfully compromises firmware can potentially survive some operating system reinstalls because the malicious code may remain outside the primary storage environment. Such attacks are significantly less common for ordinary users than typical phishing, malicious downloads, or credential theft, but they are important enough that modern hardware platforms include dedicated firmware protections. Manufacturers increasingly use signed firmware updates, hardware-backed verification, boot protection, and security monitoring to make unauthorized firmware modification more difficult. Keeping manufacturer firmware reasonably current can therefore contribute to overall device security when updates address known vulnerabilities.
Secure Boot is one of the best-known UEFI security features and is designed to help ensure that trusted boot software runs during startup. When properly configured, the firmware verifies digital signatures before allowing certain boot components to execute. This can help defend against malicious software that attempts to take control before the operating system’s normal security protections become active. Secure Boot does not replace antivirus software, operating system updates, strong passwords, or other security measures because it addresses a specific part of the startup chain. Some users disable it temporarily when working with specialized operating systems or hardware, but disabling security features without a clear reason can reduce protection. Modern operating systems are generally designed to work with Secure Boot enabled.
TPM technology often appears beside firmware security settings because modern operating systems use it for functions such as encryption, credential protection, and device integrity. Some systems use a physical Trusted Platform Module chip, while others provide firmware-based implementations such as Intel PTT or AMD fTPM. Changing or clearing TPM settings without understanding their role can affect encrypted data or authentication features. A user with BitLocker or another hardware-backed encryption system should ensure recovery information is available before making significant firmware security changes. Firmware menus may present warnings before sensitive actions, and those warnings should not be dismissed casually. Low-level security configuration is powerful precisely because it can influence the computer before normal software starts.
BIOS passwords provide another security layer but should not be confused with Windows account passwords. A firmware administrator password can restrict who is allowed to modify BIOS or UEFI settings, while some systems also support passwords that must be entered during startup. These controls can be valuable in business environments, schools, kiosks, and other situations where administrators need to prevent unauthorized configuration. However, forgetting a firmware password can create significant difficulties because recovery procedures vary by manufacturer and may require proof of ownership or hardware servicing. Users should therefore record important firmware credentials securely. A BIOS password is most useful when it forms part of a broader security strategy rather than being treated as the computer’s only protection.
Physical security remains relevant because someone with direct access to a computer may attempt to alter boot settings, start external tools, remove storage devices, or reset certain firmware configurations. Organizations can reduce these risks using restricted firmware access, encrypted storage, Secure Boot, device management, and controlled physical access. Personal users may not require every enterprise-level control, but enabling appropriate platform security features can still provide meaningful protection. The key is understanding that BIOS or UEFI is not merely an obscure menu for enthusiasts. It is part of the trust foundation that determines how the computer starts and which software receives control first. As operating system security becomes stronger, protecting the firmware and boot process becomes increasingly important.
Frequently Asked Questions About BIOS
What does BIOS stand for?
BIOS stands for Basic Input/Output System. It traditionally refers to motherboard firmware that initializes hardware and helps start the computer before the operating system loads.
Is BIOS the same as UEFI?
Not exactly. UEFI is the modern replacement for traditional BIOS, although many people still use the word BIOS when referring to a computer’s UEFI firmware settings.
Can a computer work without BIOS?
A typical PC requires working system firmware such as BIOS or UEFI to initialize essential hardware and begin the boot process. If that firmware is severely corrupted or unavailable, the computer usually cannot start normally.
Should I update my BIOS?
A BIOS update can be worthwhile when it fixes a relevant security issue, solves hardware problems, improves stability, or adds support for a component you need. If the system works correctly and the update offers nothing relevant, updating solely because a newer version exists may not always be necessary.
Is it safe to change BIOS settings?
Changing well-understood settings is generally safe, but incorrect values can cause startup problems, instability, security changes, or hardware issues. Users should record original settings and avoid changing advanced voltage, boot, storage, or security options unless they understand the consequences.