
What Is CNAPP?
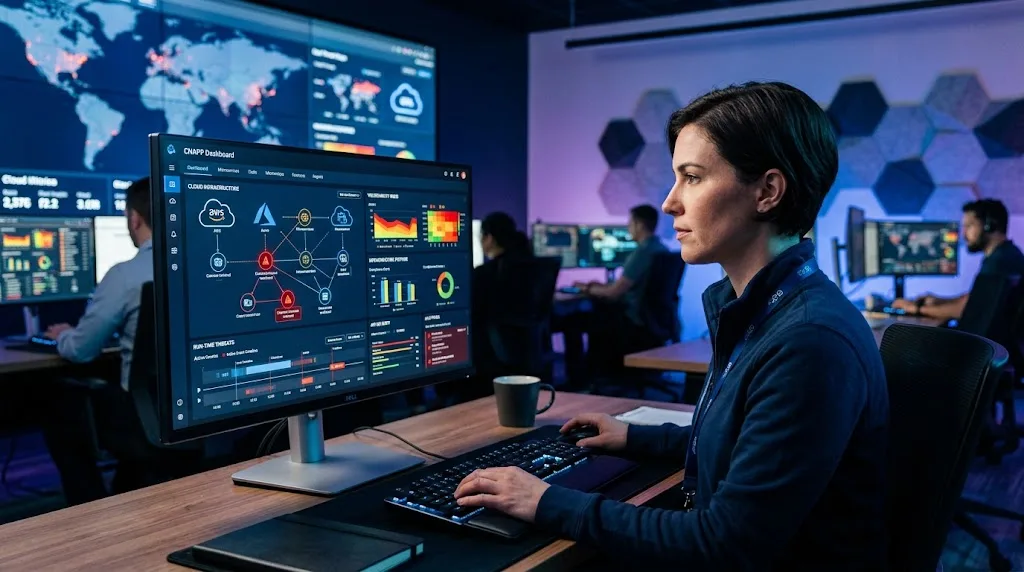
CNAPP stands for Cloud-Native Application Protection Platform. It is a security platform that brings together tools for discovering, assessing, and managing risks across cloud environments. A CNAPP can give security, development, and cloud operations teams a shared view of applications, infrastructure, identities, and configurations.
Cloud-native applications commonly use containers, Kubernetes, microservices, serverless functions, APIs, and managed cloud services. These components can be created, changed, and removed quickly, sometimes across several cloud providers. A CNAPP helps organizations monitor this shifting environment and apply security controls from the development stage through deployment and runtime.
CNAPP is a broad product category, not a guarantee that every platform includes the same features. One product may combine cloud configuration checks, workload protection, and identity analysis, while another may emphasize additional areas. Organizations should compare a platform’s actual capabilities, integrations, and coverage with the systems they need to secure.
Why Cloud-Native Security Is Complex
Traditional security approaches often assume that systems and network boundaries stay relatively stable. Cloud-native applications are more distributed: a single service may depend on containers, cloud storage, APIs, databases, and services managed by a cloud provider. Teams need to understand how these parts connect, even when separate groups build and operate them.
Cloud resources can also change faster than manual review processes can keep up with. A storage bucket may become publicly accessible, a container image may include a known vulnerability, or a service may receive broader permissions than it needs. These conditions can appear during routine deployment and remain in place unless monitoring detects them.
Cloud security also follows a shared responsibility model. Providers protect the underlying infrastructure, while customers remain responsible for many application, identity, data, and configuration decisions. A CNAPP can help teams review parts of the customer’s environment, but it does not transfer security responsibility to the platform or replace the organization’s own policies and processes.
Core Capabilities of a CNAPP
Cloud security posture management (CSPM) checks cloud accounts and services for risky configurations, policy violations, and compliance gaps. It can flag issues such as unexpected public access or security settings that do not meet an organization’s standards. CSPM gives teams a way to review posture across accounts, regions, and cloud services.
Cloud workload protection (CWPP) focuses on workloads such as virtual machines, containers, and serverless functions. Depending on the platform, it may assess vulnerabilities, detect malware, or monitor behavior at runtime. Container image scanning can identify known vulnerabilities before deployment, giving developers an opportunity to address issues earlier in the software delivery process.
Cloud infrastructure entitlement management (CIEM) examines access granted to users, roles, and applications in cloud environments. It can help identify excessive permissions, unused privileges, or access combinations that create risk. Other CNAPP capabilities may include infrastructure-as-code scanning, Kubernetes security checks, compliance reporting, secrets detection, and risk prioritization.
How a CNAPP Works Across the Application Lifecycle
A CNAPP can check for risks during development by scanning infrastructure-as-code files, container images, and other deployment artifacts. These checks may catch an insecure configuration or vulnerable component before the application reaches production. Developers can then address findings within their existing workflows, reducing the chance that an issue will need urgent attention later.
During deployment, the platform can assess cloud configurations, identity permissions, network exposure, and workload settings. It may compare these details with security policies and highlight conditions that need review. When findings are connected to specific resources, teams can better understand where an issue exists and which team or person should handle it.
After deployment, continuous monitoring can identify changes in cloud posture, new vulnerabilities, and unusual activity. Some platforms correlate signals across assets and identities to show how separate issues may contribute to a larger risk. Integrations with development, cloud, and ticketing tools can help teams assign findings and automate selected responses.
What Risks Can a CNAPP Help Identify?
A CNAPP can help detect cloud misconfigurations, such as exposed services, overly permissive network rules, or storage that is more accessible than intended. It can also identify resources that do not follow security policies. These checks matter because a configuration mistake can create a route to sensitive systems or data.
The platform may find vulnerabilities in operating systems, container images, or application dependencies, depending on its scanning coverage. Identity analysis can reveal access that exceeds what a user or service needs. When findings are connected, teams can prioritize a vulnerable, internet-facing workload with powerful permissions over an isolated issue with limited exposure.
Some CNAPPs monitor workload activity to identify suspicious behavior, such as unexpected processes or unusual connections. Detection depends on what data the platform collects and how its rules are configured. Organizations still need incident response plans and trained staff to investigate alerts, confirm threats, contain affected systems, and restore normal service.
Benefits of Using a CNAPP
A unified view can make it easier to understand security across cloud accounts, identities, workloads, and development stages. Teams may spend less time switching between disconnected dashboards or reconciling findings manually. Seeing a configuration issue alongside the affected service and its permissions can help security staff investigate context before deciding what to address first.
Risk prioritization can help teams focus on issues with a plausible path to impact. A vulnerability may be more urgent when it affects an exposed workload that handles sensitive data and has broad permissions. Context does not replace expert judgment, but it can help reduce alert fatigue and direct limited security resources toward more consequential risks.
CNAPP tools can also support collaboration between developers, cloud operations, and security teams. Findings linked to code or specific cloud resources make ownership clearer and can help organizations build security checks into software delivery. Teams can track remediation, repeatable patterns, and compliance needs without treating every security issue as a separate investigation.
CNAPP, CSPM, CWPP, and CIEM: What’s the Difference?
CSPM focuses on cloud configuration, exposure, and compliance posture. A CNAPP may include CSPM as one part of a wider platform that also covers workloads, identities, or development artifacts. The relationship varies by vendor, so check whether a product includes the CSPM controls and cloud services your organization needs.
CWPP centers on protecting workloads, while CIEM analyzes permissions and access in cloud environments. CNAPP platforms often combine some of these capabilities, but vendors may define feature names and product boundaries differently. Ask a provider to demonstrate how its platform scans your actual services, finds a risk, and helps your team resolve it.
A CNAPP does not necessarily replace every security tool. An organization may still need dedicated application security testing, secrets management, endpoint protection, identity governance, API security, or data protection. The right mix depends on its existing controls, cloud architecture, regulatory needs, and the expertise available to manage each tool.
Common CNAPP Use Cases
One common use case is monitoring security posture across multiple cloud accounts or providers. A CNAPP can help teams find misconfigurations, review compliance policies, and understand which resources need attention. This is especially useful when different departments deploy cloud services independently and the security team needs consistent visibility.
Another use case is protecting containerized applications and Kubernetes environments. Teams can scan images before deployment, assess cluster configurations, and monitor workloads for risks after they go live. As industries such as telecommunications adopt cloud-native infrastructure for services including 5G Standalone, security teams need ways to assess the applications, workloads, identities, and cloud settings supporting those environments.
Organizations can also use a CNAPP to connect development checks with runtime findings. If a risky configuration appears in code and later affects a production workload, linking the two can help identify the source and prevent recurrence. This provides a path toward a consistent DevSecOps process, where security checks support delivery instead of appearing only at the end.
How to Choose a CNAPP
Begin by listing the cloud environments, workloads, and development tools your organization needs to protect. Then identify its biggest security challenges, such as misconfiguration, container vulnerabilities, excessive permissions, or limited runtime visibility. A clear use case makes vendor comparisons more useful and helps prevent choosing a product based only on a long feature list.
During a product evaluation, ask vendors to demonstrate common tasks using an environment similar to yours. Check how the platform connects to cloud accounts, scans infrastructure-as-code and images, maps identities to workloads, and prioritizes related findings. Review integration options, reporting, deployment requirements, data handling, and the ongoing effort needed to maintain the platform.
Consider usability and total operating cost alongside technical coverage. Teams should be able to understand how findings are generated, investigate alerts, and track remediation. Ask about unsupported services, agent or integration requirements, alert tuning, and pricing as cloud usage expands. A suitable CNAPP is one the organization can operate consistently and connect to clear ownership.
Implementing a CNAPP Effectively
Start with a clear inventory of cloud accounts, projects, teams, and workloads. Select one representative environment or application for a pilot, then connect it to the platform in a controlled way. Establish visibility before enabling every available control, and record which assets, identities, and data are included in the initial assessment.
Next, prioritize a small number of policies tied to meaningful risks. These could include reviewing unexpected public access, reducing excessive permissions, or checking vulnerable images before deployment. Agree on severity levels, remediation timelines, and escalation routes with development and cloud operations teams, so every finding has an understandable next step.
Expand coverage gradually after the pilot process works. Track practical results, such as time to remediate high-risk findings, repeated configuration issues, and coverage of important workloads. Use those results to tune policies and consider automating well-understood actions. The goal is a repeatable cloud security process that keeps pace with change without overwhelming the teams responsible for delivery.
Conclusion
A CNAPP brings cloud security capabilities together to help protect applications and infrastructure across development, deployment, and runtime. Depending on the platform, it may connect configuration management, workload protection, identity analysis, and other checks in a shared view of risk.
This visibility can help teams find issues earlier, see how risks relate, and coordinate remediation across security, development, and cloud operations. Results depend on the platform’s coverage, its integration with existing workflows, and the organization’s ability to investigate and resolve findings.
Before selecting a CNAPP, map your environment and identify the security gaps that matter most. Evaluate products against real workloads, begin with a focused rollout, and expand controls as teams establish clear ownership and a reliable remediation process.
Frequently Asked Questions
What does CNAPP stand for?
CNAPP stands for Cloud-Native Application Protection Platform. It describes a category of platforms that combine security capabilities to protect cloud-native applications and infrastructure.
What is the main purpose of a CNAPP?
A CNAPP helps teams find, prioritize, and manage cloud security risks across areas such as configurations, workloads, identities, and development workflows.
Is CNAPP the same as CSPM?
No. CSPM focuses on cloud configuration and security posture, while a CNAPP may combine CSPM with workload protection, identity analysis, and other cloud security capabilities.
Does a CNAPP replace a cloud security team?
No. A CNAPP can provide visibility and automation, but people still need to set policies, investigate alerts, make risk decisions, and coordinate remediation.
When should an organization consider a CNAPP?
An organization may consider one when cloud environments are difficult to monitor across separate tools or when it needs connected visibility into risks from development through runtime.