
Microsegmentation: How It Strengthens Network Security
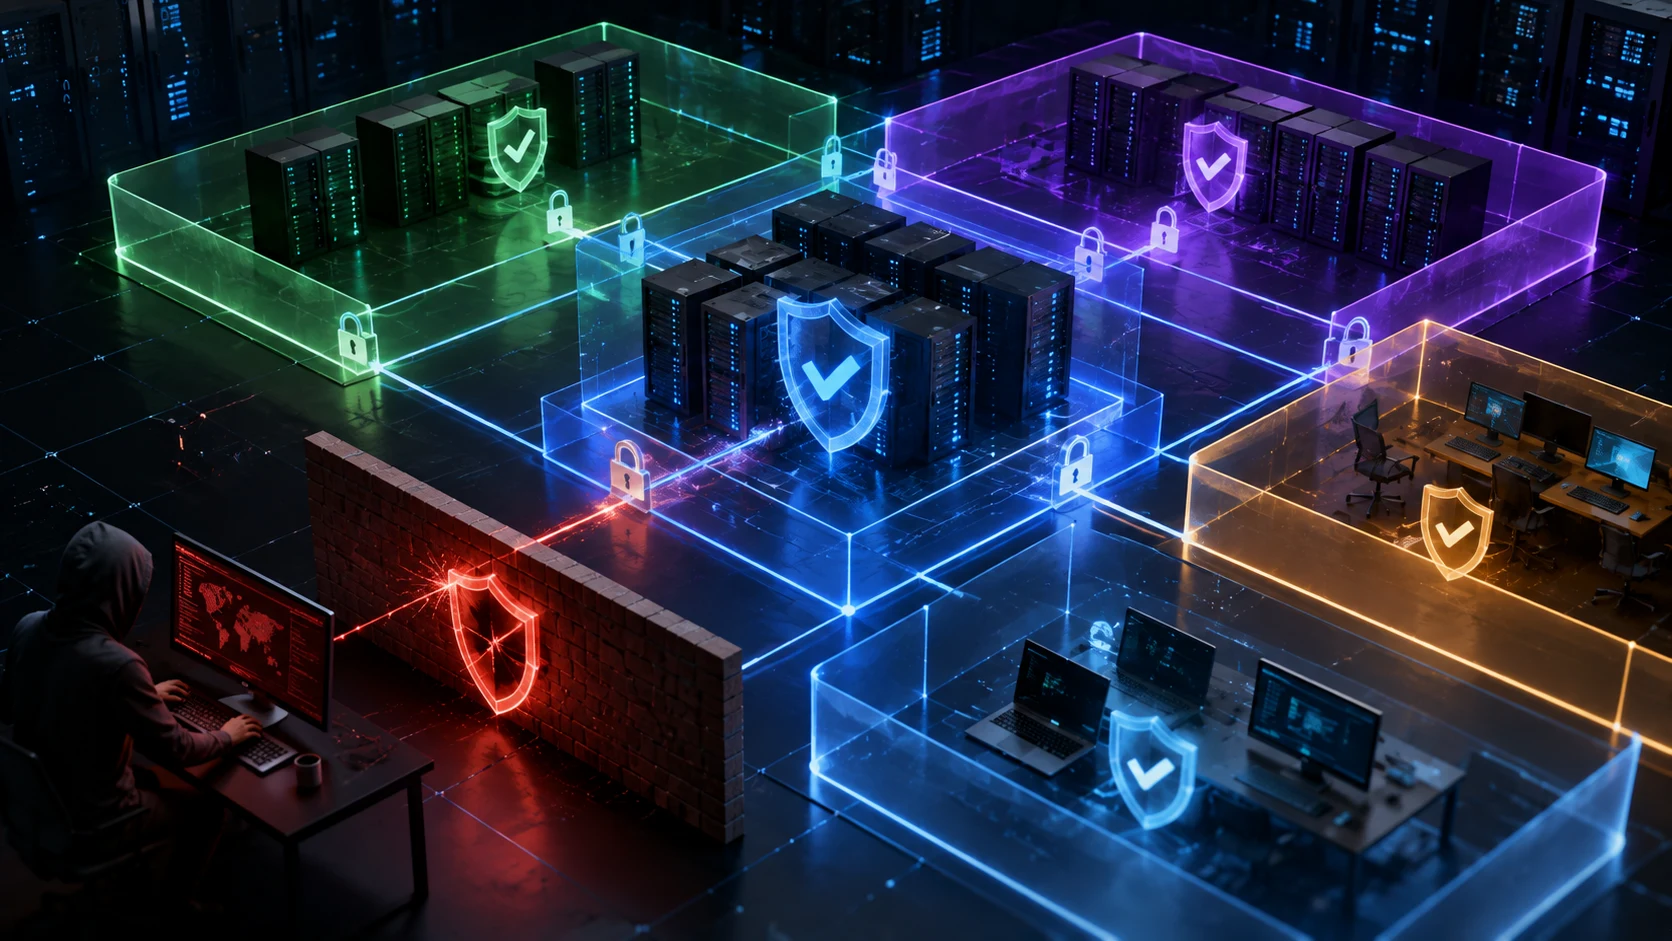
Microsegmentation is a cybersecurity strategy that divides a network or computing environment into smaller, isolated security zones so organizations can control how workloads, applications, users, and services communicate. Traditional network security often focuses heavily on defending the outer perimeter, but modern environments contain cloud platforms, remote users, containers, virtual machines, APIs, and distributed applications that communicate internally. Once an attacker gets past perimeter defenses, broad internal access can create opportunities for lateral movement. Microsegmentation addresses this problem by applying more granular security policies inside the environment. Instead of automatically trusting internal traffic, organizations can determine exactly which systems are allowed to communicate. This approach helps reduce attack paths and contain security incidents before they spread widely.
The concept has become particularly important as businesses adopt cloud computing, hybrid infrastructure, virtualization, and zero trust security models. Traditional network segmentation commonly relies on VLANs, subnets, and physical network boundaries, while microsegmentation can apply controls closer to individual workloads or applications. A database server may be permitted to communicate only with a specific application, while unrelated workloads are blocked even if they operate within the same broader network. Security policies can also consider application identity, workload labels, user context, or other attributes. This greater precision allows organizations to design access around actual business requirements. The result is a network environment with fewer unnecessary communication paths available to attackers.
Microsegmentation does not mean creating thousands of arbitrary firewall rules without understanding application behavior. Effective implementation begins by identifying assets, mapping communication flows, understanding dependencies, and defining which connections are genuinely necessary. Organizations can then create policies that follow the principle of least privilege, allowing required traffic while restricting everything else. Monitoring and automation become important because modern environments change frequently. New cloud workloads may appear quickly, applications may scale automatically, and containers can exist for only a short period. Static network controls alone may struggle to keep up with this level of change, which is why modern microsegmentation platforms increasingly use identity and workload context.
Cybersecurity teams use microsegmentation for several objectives, including ransomware containment, breach prevention, workload protection, compliance, cloud security, and zero trust architecture. If malware compromises one endpoint, segmentation controls can make it harder for the malicious software to connect freely to databases, administrative systems, or other valuable assets. Similar controls can reduce unnecessary access between development, production, employee, and sensitive data environments. The strategy cannot guarantee that an attacker will never compromise a system, but it can significantly reduce what happens after the initial compromise. In security, limiting the blast radius of an incident can be almost as important as preventing the first intrusion.
This guide explains what microsegmentation means, how it works, how it differs from traditional network segmentation, and why it has become an important part of modern network security. It also explores zero trust, east-west traffic, lateral movement, policy enforcement, application dependency mapping, cloud workloads, ransomware, implementation challenges, and practical deployment strategies. Related semantic terms such as network segmentation, least privilege access, workload security, security zones, software-defined networking, identity-based policies, attack surface reduction, and breach containment are included naturally throughout the discussion. The objective is to explain microsegmentation clearly without reducing it to marketing terminology. By understanding the underlying security model, organizations can determine where it provides meaningful protection.
What Is Microsegmentation?
Microsegmentation is the practice of creating highly granular security boundaries around applications, workloads, devices, services, or other computing resources. Instead of treating an entire internal network as one broadly trusted area, security teams divide access according to specific communication requirements. A workload processing customer information, for example, might communicate with only its authorized application servers and management tools. Other internal systems would not automatically gain access simply because they belong to the same organization. Policies can be enforced using host-based controls, software-defined networking, cloud security mechanisms, virtualization platforms, or dedicated segmentation technologies. The central idea is to reduce unnecessary connectivity and make each permitted communication relationship intentional.
Traditional network designs often create large trust zones based on physical location or network addresses. Devices connected to the corporate network may receive considerably more access than devices arriving from the public internet. Microsegmentation challenges this assumption by recognizing that internal location alone does not prove trustworthiness. An employee laptop can be compromised, a server can contain vulnerable software, or stolen credentials can be used from an apparently legitimate account. Security controls therefore need to evaluate communication at a more detailed level. Microsegmentation can restrict connections even between resources residing in the same subnet, data center, or cloud environment. This creates internal barriers that are difficult to achieve through perimeter firewalls alone.
The term “micro” refers to the smaller scale at which security policies can be applied. Segmentation might be defined around individual applications, groups of workloads, service tiers, sensitive databases, development environments, or specific business functions. The exact level of granularity should reflect operational requirements rather than an assumption that every device needs its own isolated zone. Excessive segmentation can create unnecessary complexity if policies become impossible to understand or maintain. Effective microsegmentation therefore balances security precision with manageability. The objective is not to block communication randomly but to allow the minimum connectivity required for systems to perform their legitimate functions.
Modern microsegmentation solutions often separate security policy from fixed network addressing. A workload can move between servers, cloud environments, or IP addresses while retaining policies associated with its identity or role. This is valuable in dynamic infrastructure because traditional rules based entirely on network location can become difficult to maintain. Containers and automatically scaled cloud instances may be created and removed frequently, making static IP-based policies especially inconvenient. Identity-based or label-based segmentation allows policies to follow the workload more naturally. Security teams can describe what an application is allowed to communicate with instead of continuously rewriting rules whenever infrastructure changes underneath it.
Microsegmentation should be viewed as a security architecture rather than one particular product. Organizations can implement the concept using several technologies depending on their environment. Host firewalls, hypervisor controls, cloud security groups, software-defined networks, container networking platforms, and specialized policy engines can all contribute to segmentation. The important question is whether access is being restricted at the appropriate level and managed consistently. A successful strategy also includes visibility, monitoring, policy governance, and change management. Technology provides enforcement, but security teams still need a clear understanding of business applications and communication dependencies to decide which traffic should actually be allowed.
How Microsegmentation Works
Microsegmentation begins with visibility into how systems communicate. Security teams need to know which applications exist, where workloads are located, which ports and protocols they use, and what dependencies connect different components. A web application might communicate with an application server, which then connects to a database and authentication service. Monitoring these traffic flows helps teams distinguish legitimate communication from unnecessary exposure. Without this discovery stage, administrators may accidentally block essential business traffic or leave overly broad policies in place. Application dependency mapping is therefore one of the most important early steps because segmentation rules should be based on actual operational behavior rather than assumptions about how systems work.
Once communication patterns are understood, resources can be grouped according to business purpose, sensitivity, environment, ownership, or technical function. Production systems may be separated from development resources, while payment applications may receive stronger isolation than ordinary internal services. Organizations can also distinguish user endpoints, administrative tools, databases, application tiers, and internet-facing workloads. These groupings form the basis for security policy. Instead of creating rules for every IP address individually, administrators may define that workloads with one security label can communicate with another group only through approved ports. This policy abstraction can make large-scale environments easier to manage while maintaining granular control over network relationships.
Enforcement occurs when network traffic is compared against the defined policy. If communication matches an approved rule, it is allowed to continue. If the traffic is not authorized, the enforcement point can block or reject it according to the configured security model. Enforcement may occur directly on the workload, within a virtual network, through cloud controls, or at another software-defined security layer. The closer enforcement occurs to the protected resource, the less an attacker can benefit from simply moving around a traditional network boundary. Distributed enforcement is therefore an important characteristic of many microsegmentation architectures because protection can exist wherever workloads operate.
Many organizations begin with monitoring rather than immediately blocking unfamiliar communication. An observation or visibility mode allows security teams to see what would be denied under proposed policies without disrupting production systems. This approach helps identify hidden dependencies that application owners may have forgotten or never documented. Once the expected traffic is understood, policies can gradually move into enforcement. Starting with critical applications or sensitive data can make deployment more manageable than attempting to segment the entire organization simultaneously. Incremental implementation also allows teams to refine naming conventions, approval workflows, testing procedures, and exception handling before the environment becomes highly complex.
Automation becomes increasingly important as environments grow. Manually creating and maintaining thousands of individual access rules can produce configuration errors and outdated policies. Modern tools can use tags, identities, application metadata, orchestration platforms, and infrastructure information to apply policies automatically. When a new workload receives a particular classification, the appropriate security rules can follow without administrators creating every rule from scratch. Automation should still operate within governance and review processes because an incorrect automated policy can affect many systems quickly. The strongest implementations combine centralized policy management with distributed enforcement, continuous visibility, and controlled automation that reflects clearly defined security objectives.
Microsegmentation vs Traditional Network Segmentation
Traditional network segmentation divides a larger network into separate zones using technologies such as VLANs, subnets, routers, access control lists, and firewalls. These techniques remain useful and should not be considered obsolete simply because microsegmentation offers greater granularity. A company might place guest devices, employee computers, production servers, and administrative systems on different network segments. Traffic crossing those boundaries can then be inspected or restricted. This reduces some forms of unnecessary connectivity and can improve both security and network management. However, traditional segmentation often creates relatively large zones in which many systems can still communicate freely once traffic has crossed the primary boundary.
Microsegmentation applies security boundaries at a smaller and often more flexible level. Two servers located within the same subnet can be given completely different communication permissions according to their roles. An application server might be permitted to query a specific database while being prevented from initiating connections to neighboring systems. This capability limits the amount of implicit trust associated with network location. It also supports environments where workloads move frequently and cannot be tied conveniently to fixed physical network structures. Microsegmentation therefore complements traditional segmentation by adding detailed controls inside broader zones rather than necessarily replacing every VLAN, subnet, or firewall already in use.
Traditional segmentation is often described as north-south focused because perimeter controls commonly inspect traffic moving into or out of protected network zones. Microsegmentation places greater emphasis on east-west traffic, meaning communication between workloads operating inside data centers, cloud platforms, or enterprise environments. East-west visibility matters because attackers who compromise one internal resource frequently attempt to discover and access additional systems. If internal communication is broadly allowed, lateral movement can become easier. Microsegmentation inserts controls into those internal pathways. By restricting which workloads can communicate, organizations can prevent one compromised asset from automatically becoming a bridge toward more sensitive parts of the environment.
Another difference involves the way policies are expressed. Traditional rules frequently depend heavily on IP addresses, network ranges, interfaces, and physical or virtual topology. Microsegmentation can use those elements but may also incorporate application labels, workload identities, security groups, service roles, and contextual attributes. This can make policy easier to align with business intent. A security team can define that “payment application servers may communicate with the payment database” rather than maintaining a list of individual addresses manually. When infrastructure changes, policy can remain associated with the application identity. This abstraction becomes particularly valuable in cloud and container environments where addresses may change much more frequently than traditional data-center servers.
Organizations should generally treat traditional segmentation and microsegmentation as complementary layers. Network zones remain useful for separating major environments and controlling broad traffic flows. Microsegmentation can then protect high-value systems or reduce excessive communication inside those zones. Defense in depth is stronger when multiple independent security controls support one another. A perimeter firewall may block unauthorized internet traffic, network segmentation can separate major departments, and microsegmentation can restrict communication between individual application tiers. If one control is bypassed, another may still limit the attacker. Combining these approaches creates more resilient network security than depending entirely on a single boundary to protect everything behind it.
How Microsegmentation Supports Zero Trust Security
Zero trust security is built around the principle that access should not be granted automatically because a user or device happens to be inside a trusted network. Instead, organizations should verify identities, evaluate context, enforce least privilege, and continuously manage access according to risk and business requirements. Microsegmentation supports this model by removing unnecessary trust between internal workloads. A compromised device cannot simply communicate with every nearby server because each connection can be governed by policy. This approach moves security away from the older idea of a hard perimeter surrounding a trusted interior. The network becomes a collection of controlled relationships rather than one large trusted environment.
Least privilege is central to both zero trust and microsegmentation. Every workload should receive only the connectivity required to perform its legitimate role. A web server that needs database access on one specific service should not automatically receive permission to connect to administrative tools, file servers, backup systems, or unrelated databases. Reducing unnecessary access lowers the number of pathways available during an attack. Least privilege also makes unusual behavior easier to identify because approved communication patterns are more narrowly defined. When a workload suddenly attempts to reach an unexpected system, monitoring tools can treat the behavior as suspicious instead of assuming internal traffic is harmless.
Identity plays an increasingly important role in zero trust segmentation. Traditional networking often relies primarily on IP addresses, but modern infrastructure can associate policies with workload identities, service accounts, application labels, user roles, or device posture. This context allows security decisions to remain meaningful even when workloads move or addresses change. In a cloud environment, for example, a newly created application instance can automatically receive policies associated with its role. Identity-based segmentation can therefore improve consistency and reduce dependence on fragile manual configuration. However, identity systems themselves must be protected carefully because compromised credentials or incorrectly assigned labels can undermine the security model.
Continuous verification is another zero trust principle that complements microsegmentation. Access should not necessarily remain trusted forever simply because a connection was allowed at one point. Organizations can monitor workloads, authentication events, network behavior, and security signals to identify changes in risk. If a system begins behaving unusually or becomes associated with a security incident, segmentation policies may be tightened automatically or manually. This type of adaptive response can limit exposure while analysts investigate. Microsegmentation provides the enforcement capability, while monitoring and identity systems provide additional context. Together, these components create a more dynamic defense than static network rules alone.
Microsegmentation does not create a complete zero trust architecture by itself. Zero trust also involves identity management, endpoint security, authentication, device health, data protection, application security, monitoring, and governance. An organization could implement excellent workload segmentation while still leaving weak passwords or insecure endpoints unaddressed. The value of microsegmentation comes from its role as one important control within the broader strategy. It reduces implicit network trust and creates more precise access boundaries. When combined with strong identity and continuous security monitoring, it helps transform zero trust from an abstract principle into enforceable rules governing how systems actually communicate.
How Microsegmentation Limits Lateral Movement and Ransomware
Lateral movement occurs when an attacker who has compromised one system attempts to reach additional resources inside the environment. The initial entry point may be a user laptop, vulnerable application, stolen account, or exposed server. Attackers often perform discovery after gaining access, looking for databases, administrative tools, file shares, identity systems, backup infrastructure, and other valuable targets. Flat networks can make this process easier because internal communication may face relatively few restrictions. Microsegmentation reduces available pathways by requiring connections to match explicit security policies. A compromised endpoint can therefore remain isolated from many systems that would otherwise be reachable.
Ransomware frequently becomes more damaging when malicious software or attackers can move between systems and access shared resources. If every workload can communicate broadly, one successful compromise may expose file servers, management platforms, virtual infrastructure, or other important systems. Microsegmentation can reduce this blast radius by preventing unauthorized communication between security zones. An infected user device might be able to reach required business applications without being permitted to connect directly to server management interfaces. Similarly, application workloads can be prevented from communicating with systems outside their operational dependencies. These restrictions cannot guarantee ransomware prevention, but they can make widespread propagation substantially more difficult.
High-value assets often deserve especially strict segmentation. Identity infrastructure, backup systems, payment applications, administrative platforms, sensitive databases, and security management tools can be placed behind narrow access policies. Only authorized workloads and administrators should be permitted to communicate with them through required ports and protocols. This strategy creates additional obstacles for attackers seeking privilege escalation or persistence. Protecting backup environments is particularly important because some ransomware operations attempt to damage recovery capabilities before encrypting production systems. Segmentation can reduce direct pathways to those systems and support a recovery strategy that assumes some parts of the environment may eventually become compromised.
Microsegmentation also improves incident response because security teams can contain affected systems more precisely. Instead of disconnecting an entire department or network segment, administrators may isolate a compromised workload while keeping unrelated services operational. Automated response platforms can sometimes apply emergency policies when suspicious activity is detected. This can reduce the time attackers have to expand their access. Precise containment is particularly valuable for businesses that cannot easily shut down large production environments. However, emergency segmentation procedures should be tested in advance because poorly understood application dependencies can cause disruption when access rules are tightened quickly during a real incident.
The effectiveness of ransomware containment depends on policy quality. If administrators create broad rules such as allowing all internal systems to communicate with each other, the existence of a microsegmentation platform provides little practical protection. Policies should reflect real application requirements and minimize unnecessary pathways. Security teams should also monitor denied traffic because repeated attempts to access unauthorized systems can reveal scanning, malware behavior, misconfiguration, or attack activity. Combined with endpoint detection, identity security, backups, vulnerability management, and user awareness, microsegmentation becomes a powerful layer of ransomware defense. Its greatest contribution is reducing how far an attacker can travel after successfully compromising the first resource.
Microsegmentation in Cloud, Hybrid and Data Center Environments
Cloud computing has made microsegmentation increasingly relevant because workloads can be created, moved, scaled, and removed much faster than in traditional infrastructure. Cloud platforms provide several native controls that can restrict communication between instances, networks, services, and applications. Security groups, virtual network policies, identity controls, and service-level permissions can all contribute to segmentation. However, cloud environments can become complicated when organizations operate hundreds of accounts, subscriptions, regions, and services. A consistent security model is therefore important. Microsegmentation helps businesses define expected communication relationships rather than assuming everything inside one cloud environment should automatically communicate.
Hybrid environments create additional challenges because applications may span private data centers, public clouds, branch locations, and software-as-a-service platforms. Traditional network controls can become difficult to manage when workloads cross these boundaries. Security teams may need a policy model that works consistently across several infrastructure types. Workload identity and centralized policy management can help reduce dependence on where a system physically resides. A database running on premises and an application operating in the cloud can still follow tightly defined communication rules. This consistency is valuable during cloud migration because organizations rarely move every workload at the same time.
Virtual machines are well suited to microsegmentation because virtualization platforms can enforce security policies close to individual workloads. Two virtual machines running on the same physical host may be prevented from communicating even though traditional network hardware would view them as being located together. Distributed virtual networking allows security controls to follow workloads as they move between hosts. This approach reduces the need to route every internal connection through centralized hardware firewalls. It can also provide more detailed visibility into east-west traffic. Virtualized data centers therefore became an important early environment for software-defined microsegmentation and remain a common deployment scenario.
Containers and Kubernetes environments introduce another level of dynamism because application components can be created and destroyed rapidly. A container may exist briefly while performing one function, making permanent IP-based firewall rules difficult to maintain. Kubernetes network policies and related security technologies can restrict communication according to namespaces, labels, pods, services, or application identities. Microsegmentation concepts therefore fit naturally with containerized infrastructure. A frontend service can be permitted to reach an application API while being blocked from contacting a sensitive database directly. Policy automation becomes especially important because manual management cannot realistically keep pace with thousands of short-lived container instances.
Cloud and data-center segmentation should ultimately follow the same fundamental principle: allow necessary communication and restrict unnecessary access. The implementation technology may differ, but workload relationships remain central. Organizations should map applications, classify assets, identify sensitive systems, and define appropriate trust boundaries before choosing enforcement mechanisms. They also need centralized visibility because fragmented policies across multiple clouds can become difficult to audit. Security teams should understand where rules are enforced and how exceptions are documented. A consistent microsegmentation architecture can provide stronger protection across hybrid infrastructure without forcing every environment to use identical networking technology underneath.
Key Benefits and Challenges of Microsegmentation
Attack surface reduction is one of the most important benefits of microsegmentation. Every unnecessary network pathway creates an opportunity that could potentially be abused after a compromise. By limiting connectivity according to legitimate business requirements, organizations reduce the number of systems each workload can reach. This does not remove vulnerabilities from the environment, but it makes exploiting one system less likely to provide unrestricted access elsewhere. Attackers may need to overcome additional security controls for every stage of lateral movement. Smaller trust zones therefore create more obstacles and improve the chances that suspicious behavior will be detected before the attacker reaches highly sensitive assets.
Breach containment provides another major advantage. Security professionals increasingly design environments with the assumption that prevention will occasionally fail. Phishing, software vulnerabilities, stolen credentials, supply-chain compromises, and configuration mistakes can all provide attackers with an initial foothold. Microsegmentation helps organizations prepare for this possibility by limiting the blast radius of that foothold. A compromised application should not automatically expose unrelated workloads. This resilience supports a defense-in-depth strategy in which security controls continue providing value even after another layer has failed. Containment can reduce operational disruption, data exposure, recovery costs, and the number of systems requiring forensic investigation.
Compliance and governance can also benefit from segmentation. Organizations handling regulated or sensitive information often need to demonstrate that access is restricted according to legitimate requirements. Separating systems that process payment data, healthcare information, confidential business records, or customer identities can reduce unnecessary exposure. Detailed policy logs may also help demonstrate how network communication is controlled. However, implementing microsegmentation does not automatically guarantee compliance with any regulation or standard. Requirements may include encryption, access reviews, logging, retention, authentication, and many other controls. Segmentation should therefore support a broader compliance program rather than being treated as a complete compliance solution by itself.
The largest challenge is often complexity. Enterprise applications can have hundreds of dependencies that were never documented clearly. Applying strict policies without understanding these relationships can break authentication, monitoring, backups, software updates, or integrations. Security teams may also struggle with large rule sets if policies are created manually without consistent naming and governance. Organizational cooperation becomes necessary because network teams may not know how every business application works. Application owners, developers, cloud teams, infrastructure specialists, and security professionals need to collaborate. Successful segmentation projects therefore involve discovery and operational planning as much as they involve security technology.
Policy maintenance is another ongoing challenge because networks constantly change. New applications appear, services move to the cloud, employees adopt new tools, and software updates can introduce different communication requirements. A policy that was accurate six months ago may eventually become too restrictive or unnecessarily broad. Automation, tagging, continuous monitoring, and periodic reviews can reduce this problem. Organizations should also establish clear procedures for requesting exceptions and retiring outdated rules. Microsegmentation is not a one-time configuration project that can be forgotten after deployment. Its long-term value depends on maintaining an accurate relationship between security policy and the evolving reality of business applications.
How to Implement Microsegmentation Successfully
A successful microsegmentation project should begin with clearly defined objectives. Organizations should decide whether the primary goal is ransomware containment, zero trust adoption, sensitive-data protection, cloud security, regulatory scope reduction, or general lateral movement prevention. These goals influence which applications and environments should be prioritized. Attempting to segment every device immediately can create excessive complexity and slow progress. A focused project might begin with backup infrastructure or a critical business application before expanding into additional areas. Clear objectives also make it easier to measure success because security teams know which risks the project is expected to reduce.
Asset discovery and application dependency mapping should come next. Organizations need an accurate inventory of workloads, applications, databases, user devices, cloud services, and management systems. Traffic monitoring can reveal which resources communicate and through which protocols or ports. Application owners should validate these findings because automated discovery may not explain the business reason for every connection. Dependencies should also be observed over a meaningful period so infrequent but legitimate activity is not missed. End-of-month reporting, backup operations, certificate renewal, and maintenance tasks may occur only occasionally. Comprehensive visibility reduces the risk that enforcement will interrupt important processes that were absent during a short monitoring window.
Policies should then be designed around least privilege and understandable business relationships. Instead of creating thousands of isolated technical rules, organizations can group resources according to roles and define communication between those groups. Naming conventions should be consistent enough that administrators understand what each policy protects. High-risk services such as remote administration, databases, identity infrastructure, and backup systems should receive particularly careful attention. Policies can initially operate in monitoring mode where supported, allowing teams to observe potential blocks. After dependencies have been validated, enforcement can begin gradually. This staged approach reduces disruption while still moving toward a deny-by-default model.
Testing is essential before expanding segmentation across critical production systems. Security teams should verify normal application transactions, authentication, monitoring, backup, disaster recovery, software deployment, and administrative access. Failure scenarios should also be tested so responders understand how segmentation behaves during outages or incidents. Organizations should maintain documented emergency procedures for temporarily modifying policies when legitimate services are unexpectedly blocked. However, emergency access should not become a permanent shortcut around normal governance. Every exception should have an owner, reason, and review process. Strong change management prevents the microsegmentation environment from gradually accumulating broad rules that recreate the same excessive trust it was designed to eliminate.
The final stage is continuous improvement rather than project completion. Security teams should review traffic patterns, denied connections, policy exceptions, newly discovered assets, and changes in application architecture. Metrics can track how many critical workloads are segmented, how much unnecessary connectivity has been removed, and whether high-risk communication remains controlled. Incident exercises can test whether segmentation actually limits lateral movement under realistic attack scenarios. Automation can help ensure newly created workloads inherit appropriate policies immediately. Over time, microsegmentation should become part of standard infrastructure design rather than a separate security initiative applied after applications are already deployed.
Conclusion
Microsegmentation strengthens network security by dividing computing environments into smaller trust zones and controlling communication according to explicit policies. Instead of assuming that everything inside a corporate network is trustworthy, the strategy evaluates which workloads genuinely need to communicate. This approach reduces unnecessary connectivity and makes lateral movement more difficult after an attacker compromises one system. Microsegmentation can protect individual applications, server groups, databases, virtual machines, containers, and cloud workloads. Its granular controls make it particularly useful in modern environments where applications are distributed across multiple infrastructure platforms. The fundamental objective is simple: allow required communication while eliminating unnecessary network access.
The strategy complements traditional network segmentation rather than making it irrelevant. VLANs, subnets, firewalls, and network zones remain useful for separating major environments and controlling traffic at broader boundaries. Microsegmentation adds detailed controls inside those boundaries, particularly for east-west communication between workloads. This creates a defense-in-depth model in which attackers must overcome multiple restrictions instead of gaining broad access after crossing one perimeter. Identity-based policies can also make controls more flexible when workloads move between hosts or cloud environments. Combining macro-level network segmentation with workload-level microsegmentation can create stronger protection than relying exclusively on either approach.
Microsegmentation is also closely connected with zero trust architecture. Both approaches reject unnecessary implicit trust and emphasize least privilege. A user, server, or application should not receive broad access simply because it exists inside the organization. Communication should be permitted according to identity, role, business requirement, and security context. Microsegmentation provides an enforcement mechanism for applying these principles to workload communication. However, zero trust also requires identity security, endpoint protection, authentication, monitoring, data controls, and governance. Segmentation is therefore a major building block rather than the entire zero trust strategy.
Ransomware and other modern attacks demonstrate why containment matters. Organizations cannot assume that perimeter defenses will stop every phishing message, stolen credential, vulnerable application, or supply-chain compromise. When prevention fails, security architecture should limit how far an attacker can move. Microsegmentation creates internal barriers around critical resources such as databases, management tools, identity infrastructure, and backups. These barriers can reduce the blast radius of an incident and give security teams more opportunities to detect suspicious behavior. Although no single control guarantees protection from ransomware, restricting unnecessary internal connectivity can make large-scale compromise considerably harder.
Effective implementation depends on visibility, planning, automation, and ongoing maintenance. Organizations should discover assets, map application dependencies, classify sensitive resources, create least-privilege policies, test carefully, and introduce enforcement gradually. Rules should evolve as applications and infrastructure change instead of remaining static for years. The best microsegmentation programs also integrate with broader cybersecurity practices including vulnerability management, endpoint detection, identity protection, secure backups, and incident response. When implemented thoughtfully, microsegmentation transforms the network from a broadly trusted internal environment into a controlled collection of communication relationships. That shift can significantly improve resilience against lateral movement and modern cyberattacks.
FAQs About Microsegmentation
What is microsegmentation in cybersecurity?
Microsegmentation is a security approach that divides networks and workloads into smaller protected zones and controls communication between them using granular policies. It helps prevent users, applications, or compromised systems from accessing resources they do not legitimately need.
How does microsegmentation improve network security?
Microsegmentation reduces unnecessary connectivity and limits lateral movement after a system has been compromised. By allowing only approved communication paths, it can contain attacks and reduce the number of resources exposed during a breach.
What is the difference between segmentation and microsegmentation?
Traditional network segmentation generally separates larger network areas using VLANs, subnets, routers, and firewalls. Microsegmentation applies more granular controls around individual workloads, applications, services, or small resource groups, even when they operate within the same traditional network segment.
Is microsegmentation part of zero trust?
Microsegmentation is commonly used as an important component of zero trust architecture because it supports least privilege and reduces implicit trust between internal resources. However, complete zero trust strategies also include identity security, authentication, endpoint protection, data controls, monitoring, and other safeguards.
Can microsegmentation stop ransomware?
Microsegmentation cannot guarantee that ransomware will never enter an organization, but it can make spreading between systems significantly more difficult. When combined with endpoint security, backups, vulnerability management, identity protection, and monitoring, it can substantially reduce the potential blast radius of a ransomware incident.