
Cybersecurity Tools: Essential Types & How They Work
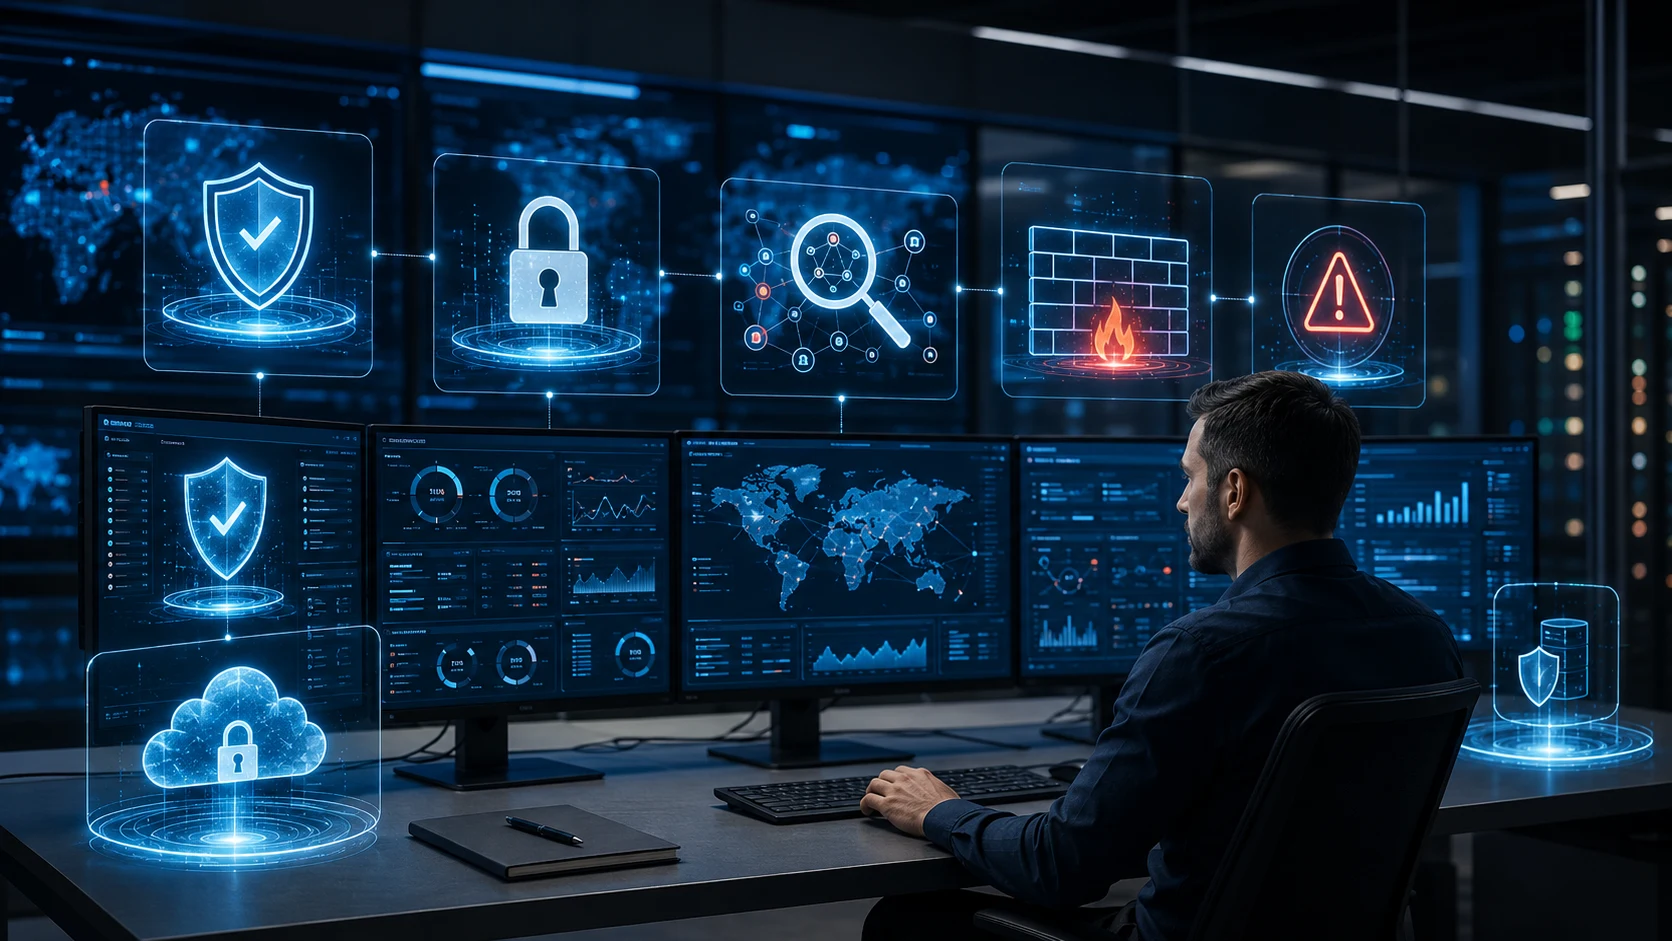
Cybersecurity tools are technologies used to protect computers, networks, applications, cloud environments, accounts, and sensitive data from unauthorized access or malicious activity. Organizations use different security tools because no single product can defend against every cyber threat. Antivirus software may detect malicious files, while a firewall controls network traffic, an identity system protects user accounts, and a SIEM platform analyzes security events across many systems. Modern cybersecurity environments also include endpoint detection and response, vulnerability management, cloud security, email protection, encryption, data loss prevention, and threat intelligence. These tools work together to prevent attacks, detect suspicious behavior, limit the impact of successful intrusions, and support incident response. The strongest security programs combine technology with people, processes, policies, and regular testing.
The cybersecurity tool landscape has expanded as businesses adopt cloud computing, remote work, mobile devices, SaaS applications, APIs, and increasingly interconnected systems. Traditional antivirus and perimeter firewalls are still useful, but modern attackers may target identities, cloud permissions, third-party software, and legitimate administrative tools rather than relying only on obvious malware. Security teams therefore need visibility across endpoints, networks, email, applications, identities, and data. The right tools depend on the organization’s size, technology environment, risk level, and regulatory responsibilities. Buying more products does not automatically create better security if those products are poorly configured or generate alerts nobody reviews. This guide explains the essential types of cybersecurity tools, how they work, where they fit, and how organizations can build a practical layered defense.
What Are Cybersecurity Tools?
Cybersecurity tools are software, hardware, or cloud-based services designed to reduce the likelihood or impact of cyberattacks. They can identify malicious files, block unauthorized network connections, monitor user behavior, protect sensitive data, detect software vulnerabilities, and help security teams investigate incidents. Some tools operate directly on computers and servers, while others monitor traffic or collect information from many systems centrally. Cloud-native security platforms may evaluate identities, workloads, containers, and configuration without requiring traditional on-premises hardware. The specific technology varies, but the purpose remains the same: reduce opportunities for attackers and improve the organization’s ability to recognize and respond when something suspicious occurs.
Security tools are often divided into preventive, detective, and responsive categories. Preventive controls attempt to stop malicious activity before damage occurs, such as multifactor authentication, web filtering, or firewall rules. Detective controls look for suspicious events that have already started or passed through earlier defenses, including endpoint monitoring and intrusion detection. Responsive tools help contain, investigate, or recover from incidents after they are identified. Many modern products perform more than one of these roles at the same time. An EDR platform, for example, can block known threats, detect unusual behavior, isolate an infected device, and provide investigation data to responders.
Cybersecurity tools also vary according to what they protect. Endpoint security focuses on laptops, desktops, and servers, while network security monitors communication between systems. Identity tools protect user accounts and permissions, and application security products identify weaknesses in software. Data security tools concentrate on information itself through encryption, access control, and data loss prevention. Cloud security platforms evaluate infrastructure, workloads, and SaaS environments. Dividing security into these areas helps organizations identify coverage gaps and avoid relying too heavily on one defensive layer.
Automation has become increasingly important because modern organizations produce enormous numbers of security events every day. A large environment may contain thousands of users, endpoints, applications, and cloud resources generating logs continuously. Human analysts cannot review every login, network request, file change, or process manually. Cybersecurity tools therefore use rules, behavioral analytics, threat intelligence, machine learning, and correlation to identify activity that deserves attention. Automation can also perform actions such as isolating an endpoint or disabling a suspicious account. Human judgment remains important because automated detections can produce false positives or miss activity that does not match expected patterns.
The most effective security toolset is usually layered rather than dependent on one product. An attacker who bypasses an email filter may still encounter endpoint protection when the malicious attachment runs. If credentials are stolen, multifactor authentication can reduce the chance that the attacker successfully logs in. Network segmentation can limit movement even after one device is compromised, while centralized monitoring may detect unusual behavior later. Backup systems provide recovery if destructive malware succeeds despite previous controls. Layered security accepts that individual defenses can fail and creates additional opportunities to stop or limit the attack.
Antivirus, EDR, and Endpoint Security Tools
Antivirus software is one of the most familiar cybersecurity tools and is designed primarily to detect and remove malicious software from endpoints. Traditional antivirus products relied heavily on signatures, which are recognizable patterns associated with known malware. When a file matched a known malicious signature, the security tool could block or quarantine it. Modern antivirus systems also use behavioral and reputation-based techniques because attackers can modify malware frequently to avoid exact signature matches. They may evaluate how a file behaves, where it came from, and whether similar files have been seen elsewhere. Antivirus remains useful, but sophisticated attacks require broader endpoint visibility than file scanning alone can provide.
Endpoint Detection and Response, commonly called EDR, continuously monitors activity on computers and servers to identify suspicious behavior. It can record process execution, command lines, network connections, file changes, login activity, and other endpoint events. Instead of asking only whether a file is known malware, EDR can detect behaviors such as unusual scripting, credential access, persistence creation, or suspicious parent-child process relationships. Security analysts can then investigate what happened before and after an alert. Many EDR tools also allow responders to isolate a compromised device remotely. This reduces the chance that an infected computer communicates with other systems while investigation continues.
Extended Detection and Response, or XDR, expands the idea of EDR by correlating signals from multiple security layers. An XDR platform may combine endpoint telemetry with email alerts, identity events, cloud activity, and network data. If a phishing email leads to an unusual login and then suspicious endpoint activity, XDR can connect those events into one larger incident. This reduces the burden of manually investigating separate alerts across several security consoles. The effectiveness of XDR depends heavily on the quality of integrations and detection logic. It is most useful when organizations already collect meaningful data across several parts of the environment.
Application control can strengthen endpoint protection by limiting which software is allowed to run. Instead of trying to identify every possible malicious program, the organization can allow approved applications and block unknown or unauthorized executables. This approach is especially useful for systems that perform predictable functions, such as kiosks, industrial workstations, or administrative servers. Application control needs careful management because legitimate updates and new software can be blocked accidentally. Organizations therefore need approval workflows and monitoring to keep allowed applications current. When implemented well, application control can stop many malware techniques before they begin.
Endpoint security also includes device encryption, host firewalls, exploit protection, USB controls, and configuration management. Full-disk encryption helps protect information if a laptop is lost or stolen. Host-based firewalls restrict network communication even when the device operates outside the corporate office. Exploit protection makes certain memory attacks more difficult, while USB restrictions can prevent unapproved storage devices from transferring data. Centralized endpoint management ensures security settings remain consistent across thousands of devices. These capabilities demonstrate why modern endpoint security is broader than antivirus alone and focuses on reducing several attack opportunities at once.
Firewalls and Network Security Tools
A firewall controls network traffic based on defined security rules. It can allow, block, or inspect connections according to source address, destination, port, protocol, application, user identity, or other attributes depending on the technology. Traditional network firewalls sit between different network zones, such as an internal business network and the public internet. They reduce unnecessary exposure by preventing external systems from connecting freely to internal services. Firewalls can also separate sensitive internal environments from ordinary employee networks. The objective is to restrict communication to what the organization actually needs rather than allowing every device to connect everywhere automatically.
Next-generation firewalls add deeper inspection capabilities beyond basic IP addresses and ports. They can identify application traffic, inspect certain content, apply intrusion prevention rules, and integrate with user identity systems. A connection using a common web port may be allowed or blocked depending on the application actually generating it. Some firewalls can also decrypt selected encrypted traffic for security inspection when the organization has appropriate technical and legal controls. These features improve visibility but also increase processing requirements and configuration complexity. A powerful firewall provides little benefit if overly broad rules allow almost every connection.
Intrusion Detection Systems, or IDS, monitor network traffic for suspicious patterns without necessarily blocking it automatically. They may identify exploit attempts, unusual protocol behavior, scanning activity, or communication associated with known threats. Intrusion Prevention Systems, or IPS, add the ability to stop or reject traffic when detection rules trigger. These tools can be integrated into firewalls or deployed separately. Signature-based detection works well for known threats, while anomaly-based approaches look for behavior that differs from expected network activity. Network detection is valuable because it can reveal attacks even when endpoint security is missing from a particular device.
Network segmentation reduces cyber risk by dividing systems into controlled zones rather than maintaining one large flat network. Security tools such as firewalls, software-defined networking, and access-control systems enforce which zones can communicate. Employee laptops may not need direct access to database servers, while guest devices should not reach internal applications at all. Sensitive administrative networks can have stronger restrictions than ordinary user areas. Segmentation limits lateral movement if attackers compromise one device. It also makes monitoring more meaningful because unusual communication between normally separate zones becomes easier to identify.
Network Access Control, commonly called NAC, determines whether devices are permitted to join specific network resources. A NAC system can evaluate device identity, user credentials, security posture, and location before granting access. An unmanaged laptop might receive only guest internet connectivity, while a company-owned device with current security software receives broader internal access. NAC can also place compromised devices into quarantine networks automatically. This helps organizations manage environments where many employee, contractor, and mobile devices connect to wired or wireless infrastructure. Identity-aware network access is especially useful when the traditional idea of a trusted internal network is no longer sufficient.
Identity and Access Management Security Tools
Identity and Access Management, commonly called IAM, controls who can access systems and what they are permitted to do after authentication. IAM platforms maintain user identities, group memberships, roles, application access, and security policies across business environments. They can connect employees with cloud applications, internal systems, and administrative resources through centralized identity services. When someone changes jobs or leaves the organization, access can be modified or removed from one central workflow. This reduces the risk of forgotten accounts remaining active indefinitely. Identity has become a major cybersecurity focus because attackers frequently use legitimate credentials instead of obvious malware to gain access.
Multifactor authentication, or MFA, strengthens login security by requiring something beyond a password. The additional factor might be a security key, authentication application, biometric method, or another supported mechanism. A stolen password becomes less useful when the attacker cannot complete the second authentication requirement. Some methods provide stronger resistance to phishing than others, particularly hardware-backed or passkey-style approaches that verify the legitimate website before authenticating. MFA should be prioritized for email, cloud administration, remote access, financial systems, and privileged accounts. It is one of the most effective controls for reducing credential-based compromise.
Single Sign-On, or SSO, allows users to authenticate through one identity provider and then access several connected applications without maintaining separate passwords everywhere. This can improve both convenience and security because organizations enforce consistent authentication policies centrally. SSO also makes it easier to disable access quickly when an employee leaves. The identity provider becomes highly important, however, because compromise of the central account can provide access to many applications. Strong MFA, monitoring, conditional access, and administrative separation are therefore essential. Centralization improves control when the identity platform itself is protected carefully.
Privileged Access Management, commonly called PAM, focuses on administrator and other high-risk accounts. These accounts may have power to change security settings, create users, access sensitive databases, or control infrastructure. PAM systems can store privileged credentials securely, require approval before administrative sessions, rotate passwords automatically, and record high-risk activity. Just-in-time access can grant elevated privileges only for the period required to complete a task. This reduces the number of permanently powerful accounts available to attackers. Privileged identities deserve stronger controls because one compromised administrator can often cause far more damage than an ordinary user account.
Conditional access and identity analytics add context to authentication decisions. A login from a trusted device in a normal location may be treated differently from one arriving from an unusual country using a newly seen browser. Security systems can evaluate device health, user risk, network location, application sensitivity, and previous behavior before allowing access. High-risk attempts may require stronger authentication or be blocked entirely. Behavioral analysis can also identify impossible travel, unusual privilege changes, or abnormal access patterns. These tools help organizations move beyond a simple password-based model toward continuous evaluation of identity risk.
SIEM, Log Management, and Security Monitoring Tools
Security Information and Event Management, commonly called SIEM, collects and analyzes logs from many systems across an organization. Firewalls, endpoints, servers, applications, cloud platforms, identity providers, and databases can all send security events into the SIEM. Centralizing this information makes it easier to identify suspicious patterns that would be difficult to recognize by reviewing each system independently. A failed login on one application may look harmless, but hundreds of failures across several accounts can indicate an attack. SIEM tools use correlation rules, analytics, and threat intelligence to identify activity requiring investigation. They also preserve historical logs that can be valuable during incident response.
Log management is a foundational part of SIEM because security investigations depend on accurate records of what happened. Logs can contain timestamps, usernames, IP addresses, device names, actions, errors, and other event information. Organizations need to collect the right logs without storing unnecessary data indefinitely. Time synchronization is important so analysts can compare events from different systems accurately. Access to security logs should also be protected because attackers may attempt to delete evidence after compromising a system. Reliable logging turns security activity into evidence that responders can analyze later.
Security analytics can detect patterns that fixed rules may miss. User and Entity Behavior Analytics, often abbreviated UEBA, attempts to establish normal behavior for users or devices and identify meaningful deviations. An employee who normally accesses a few files during office hours might suddenly download thousands of documents late at night. The behavior may be legitimate, but it deserves closer examination. Machine learning can assist with ranking unusual activity, although it does not remove the need for human investigation. Effective analytics should reduce noise rather than generate large numbers of unexplained anomaly alerts.
Security Orchestration, Automation, and Response, known as SOAR, can automate parts of incident investigation and response. When a phishing alert arrives, a SOAR workflow might collect sender information, inspect links, search for similar messages, and check whether recipients clicked them. If the threat is confirmed, the workflow may remove related emails and disable a compromised account after required approvals. Automation saves analysts time on repetitive tasks and can reduce response delays. However, organizations should be cautious about automatically taking disruptive actions based on weak detections. Good SOAR workflows combine automation with clear decision points and human oversight.
A Security Operations Center, or SOC, brings these monitoring tools together with analysts and incident processes. The SOC may use SIEM, EDR, threat intelligence, email security, and other platforms to watch for suspicious activity continuously. Some organizations operate internal SOC teams, while others use managed detection and response providers. Tools alone cannot replace analysts who understand business context and can distinguish legitimate unusual activity from actual attacks. Effective monitoring requires tuned detections, clear escalation procedures, and regular improvement. The objective is not to produce the highest possible number of alerts but to identify meaningful threats quickly enough to reduce damage.
Vulnerability Management and Application Security Tools
Vulnerability scanners identify known security weaknesses across computers, servers, network devices, applications, and other technology assets. They compare software versions, configurations, and services against information about known vulnerabilities and insecure settings. The resulting findings often include severity ratings and remediation guidance. Organizations can use these reports to prioritize patches and configuration changes before attackers exploit the weaknesses. Scanning should occur regularly because new vulnerabilities are discovered continuously. A one-time scan provides only a snapshot of the environment and can become outdated quickly as systems and threats change.
Risk-based vulnerability management goes beyond ranking findings only by technical severity. A critical flaw on an isolated test device may present less immediate danger than a medium-severity vulnerability on an internet-facing authentication server. Modern platforms may consider exploit availability, active threat activity, asset importance, internet exposure, and business context. This helps teams focus on vulnerabilities attackers are realistically more likely to use. Large organizations often discover far more vulnerabilities than they can fix immediately, making prioritization essential. The goal is to reduce meaningful exposure rather than simply close the largest number of scanner findings.
Static Application Security Testing, commonly called SAST, analyzes source code or compiled application components for potential security weaknesses without running the application normally. It can identify coding patterns associated with injection flaws, unsafe data handling, insecure cryptographic use, or other problems depending on the language and tool. Developers can run SAST during software development so weaknesses are identified before production deployment. False positives still require review because automated analysis cannot understand every application context perfectly. Integrating security testing into development pipelines helps make remediation part of ordinary software engineering rather than a late-stage activity.
Dynamic Application Security Testing, or DAST, examines a running application from the outside and attempts to identify weaknesses through its exposed interfaces. The scanner may test inputs, authentication flows, web requests, and application responses for signs of exploitable behavior. DAST does not need full access to source code, which makes it useful for testing deployed web applications. Interactive and hybrid testing approaches can combine runtime behavior with code-level insight. Application security programs often use several testing methods because each reveals different types of weaknesses. Manual penetration testing can then provide deeper investigation of high-risk systems.
Software Composition Analysis, commonly called SCA, identifies third-party libraries and open-source components used inside applications. Modern software relies heavily on external packages, which means one vulnerable dependency can affect many different products. SCA tools inventory these components and compare versions with known vulnerability information. They can also help teams understand licensing obligations and outdated packages. Dependency scanning should be integrated into development workflows so risky libraries are identified before release. Application security therefore includes not only code written internally but also the large ecosystem of software components developers reuse.
Email, Web, and Phishing Protection Tools
Email security tools filter incoming and outgoing messages for spam, phishing, malware, suspicious links, and impersonation attempts. Email remains one of the most common attack channels because criminals can send convincing messages directly to employees. Security gateways can inspect attachments, analyze sender reputation, and identify domains that resemble trusted companies. Some systems rewrite links so they can be checked when a user clicks them rather than only when the message first arrives. Machine learning can help identify unusual language or sender behavior. Effective email security reduces the number of threats employees need to recognize manually.
Attachment sandboxing provides deeper analysis of suspicious files. Instead of trusting a file because it has no known malware signature, the security system opens it in an isolated environment and observes what it tries to do. A document that launches scripts, creates persistence, or contacts suspicious servers can be blocked before reaching the user. Sandboxing is valuable against newly modified malware that traditional signatures may not recognize. Attackers may still design files that attempt to detect sandbox environments, so no single inspection method is perfect. Combining reputation, signatures, behavioral analysis, and sandboxing provides stronger coverage.
Secure web gateways and DNS filtering help prevent users from reaching malicious or inappropriate internet destinations. A DNS security service can block known phishing, malware, or command-and-control domains before the browser connects. Secure web gateways can inspect web requests and apply organizational policies based on category, risk, or content. These tools are useful when employees work remotely because protection can follow the device beyond the office network. Encrypted web traffic complicates inspection, so organizations must balance security with privacy, performance, and legal considerations. Blocking known harmful destinations provides value even without inspecting every piece of content.
Browser isolation is another technique for reducing web-based risk. Instead of allowing potentially dangerous website code to execute directly on the employee’s device, the session runs inside an isolated remote or local environment. The user sees a rendered version of the page while malicious scripts have less direct access to the endpoint. Browser isolation can be useful for unknown websites or high-risk user groups. The technology adds infrastructure and may affect some interactive websites, so it is often applied selectively. It demonstrates how cybersecurity tools can reduce risk by separating untrusted content from valuable systems rather than trying to detect every possible exploit.
Phishing simulation and security-awareness platforms focus on the human side of email attacks. Organizations can send controlled test messages to employees and provide targeted training when users interact with them. The goal should be improving recognition and reporting rather than embarrassing individuals. Security teams can measure whether employees report suspicious messages and identify departments needing additional support. Training works best when combined with technical controls because even experienced users can be deceived by convincing attacks. People should represent one defensive layer, not the final barrier protecting the entire organization.
Data Protection, Encryption, DLP, and Backup Tools
Encryption protects information by transforming it into a form that cannot be read easily without the appropriate cryptographic key. Full-disk encryption protects data stored on laptops if the device is lost or stolen, while database and storage encryption protect information held on servers or cloud services. Transport encryption protects data while it moves across networks. Strong encryption does not prevent an attacker from stealing data through an already authorized account, but it can reduce risk when storage media or network traffic is exposed directly. Key management is critical because encrypted information becomes vulnerable if attackers obtain the corresponding keys.
Data Loss Prevention, commonly called DLP, helps organizations identify and control sensitive information as employees use, share, or transfer it. DLP tools can recognize patterns associated with payment information, government identifiers, confidential documents, or organization-defined data labels. Policies may warn users, block uploads, or require approval when sensitive information is sent outside approved channels. Endpoint DLP can monitor USB devices and local file movement, while cloud DLP focuses on SaaS applications and storage. DLP requires careful tuning because overly aggressive rules can interfere with legitimate work. The objective is to reduce accidental and unauthorized data movement without making normal business processes impossible.
Data classification tools help organizations understand which information requires the strongest protection. Documents can be labeled public, internal, confidential, or highly restricted according to business policy. Classification may be applied manually by users or automatically based on content and context. Security systems can then use those labels to enforce encryption, sharing, retention, and DLP rules. A public marketing brochure should not receive the same restrictions as payroll records or source code. Classification makes security more targeted because controls follow the sensitivity of the information rather than treating every file identically.
Backup tools provide recovery when data is deleted, corrupted, encrypted by ransomware, or lost through system failure. Good backup strategies maintain separate copies and protect them from the same credentials that ordinary administrators use. Immutable or offline backups can make it harder for ransomware operators to destroy recovery points. Organizations should test restoration regularly because a backup that cannot be restored reliably provides limited protection. Recovery objectives should also reflect business priorities so critical systems can return within acceptable timeframes. Backups are therefore both an IT operations tool and an important cybersecurity control.
Secrets management protects passwords, API keys, certificates, and other credentials used by applications and automated systems. Developers sometimes place secrets directly inside source code or configuration files because it is convenient, creating a serious risk if those files are exposed. Secrets managers store credentials centrally, control which applications can retrieve them, and may rotate them automatically. Access can be logged so security teams know when sensitive credentials were used. This is particularly important in cloud and DevOps environments where machine identities may outnumber human users. Protecting nonhuman credentials is now a major part of modern data and application security.
Cloud Security and Modern Cybersecurity Platforms
Cloud Security Posture Management, commonly called CSPM, identifies risky configurations across cloud environments. It can detect publicly exposed storage, overly permissive firewall rules, missing encryption, weak logging, and other settings that increase risk. Cloud infrastructure changes rapidly, so manual reviews can become outdated within hours or days. CSPM tools continuously evaluate resources against security policies and recommended practices. They can also help organizations understand which teams own problematic resources. Configuration security is essential because many cloud incidents result from incorrect permissions or exposure rather than sophisticated attacks against the cloud provider itself.
Cloud Workload Protection Platforms, or CWPP, focus on workloads such as virtual machines, containers, and serverless services. They may provide vulnerability scanning, runtime monitoring, malware protection, and configuration analysis tailored to cloud environments. Containers introduce unique security challenges because workloads can be created and removed quickly from shared images. Scanning container images before deployment reduces the chance of known vulnerabilities reaching production. Runtime protection then watches for unexpected behavior after deployment. Cloud workload security extends familiar endpoint concepts into infrastructure that may be highly dynamic and distributed.
Cloud Infrastructure Entitlement Management, or CIEM, focuses on identities and permissions within cloud platforms. Cloud access models can become complicated because users, roles, services, and automated resources may receive privileges through several overlapping policies. CIEM tools analyze these relationships and identify excessive or unused permissions. An application may need access to one storage bucket but accidentally receive permission to administer the entire cloud account. Reducing these privileges follows the principle of least access. Identity exposure is particularly important in cloud environments because attackers can perform significant actions without compromising traditional servers directly.
Cloud-Native Application Protection Platforms, commonly abbreviated CNAPP, combine several cloud security capabilities into one broader platform. A CNAPP may include posture management, workload protection, vulnerability analysis, identity risk, infrastructure-as-code scanning, and attack-path analysis. The objective is to provide a connected view of risk from development through production. Instead of showing hundreds of unrelated findings, modern platforms may identify combinations such as an internet-facing workload with a known vulnerability and powerful cloud permissions. This context helps teams focus on exposure that could realistically lead to serious compromise.
Security Service Edge and Zero Trust-oriented platforms address users who access applications from many locations rather than operating only inside a traditional corporate network. Cloud-delivered security can enforce web filtering, application access, data controls, and identity policies regardless of whether the employee works from the office or home. Zero Trust Network Access can provide application-specific access instead of placing remote users broadly onto an internal network. The philosophy is to verify identity and context continuously rather than assuming traffic is trustworthy because it originates from one location. Modern cybersecurity increasingly follows users, applications, and data rather than relying solely on one network perimeter.
Frequently Asked Questions About Cybersecurity Tools
What are cybersecurity tools?
Cybersecurity tools are software, hardware, or cloud services used to prevent, detect, investigate, and respond to cyber threats. Examples include antivirus, EDR, firewalls, SIEM, vulnerability scanners, identity security, encryption, email protection, DLP, and cloud security platforms.
What are the most important cybersecurity tools?
The most important tools depend on the environment, but strong endpoint protection, multifactor authentication, firewalls, vulnerability management, email security, centralized logging, reliable backups, and data protection are common foundations. Larger organizations usually need additional monitoring and cloud security capabilities.
What is the difference between antivirus and EDR?
Antivirus focuses mainly on identifying and blocking malicious files and known malware behavior. EDR provides deeper continuous monitoring of endpoint activity and gives security teams investigation and response capabilities such as process analysis and device isolation.
What does a SIEM tool do?
A SIEM collects security logs and events from many systems and analyzes them for suspicious patterns. It helps security teams detect incidents, investigate what happened, correlate related events, and maintain historical security records.
Can cybersecurity tools stop every cyberattack?
No cybersecurity tool can stop every possible attack. Strong security uses multiple layers of prevention, detection, response, access control, monitoring, backup, employee awareness, and secure processes so one failed control does not expose the entire organization.